|
Nilorea Library
C utilities for networking, threading, graphics
|
|
Nilorea Library
C utilities for networking, threading, graphics
|
Functions | |
| int | n_x509_generate_ca (const char *cn, int days, N_STR **ca_cert_pem, N_STR **ca_key_pem) |
| Generate a self-signed certificate authority (CA) keypair and cert. | |
| int | n_x509_keypair_pem (int bits, N_STR **key_pem) |
| Generate an RSA private key and return it as a PEM string. | |
| int | n_x509_mint_host_cert (const char *host, const N_STR *ca_cert_pem, const N_STR *ca_key_pem, int days, N_STR **leaf_cert_pem, N_STR **leaf_key_pem) |
| Mint a per-host leaf certificate signed by the given CA. | |
Generate a self-signed certificate authority (CA) keypair and cert.
The CA is meant to be installed by the user in their browser/OS trust store so a MITM proxy can present host certificates it signs. The certificate has basicConstraints CA:TRUE and keyUsage keyCertSign,cRLSign and is signed with SHA-256.
| cn | common name for the CA subject/issuer (for example "Fissure CA"). |
| days | validity in days from now. |
| ca_cert_pem | out: newly allocated CA certificate PEM, owned by the caller. |
| ca_key_pem | out: newly allocated CA private key PEM, owned by the caller. |
Definition at line 226 of file n_x509.c.
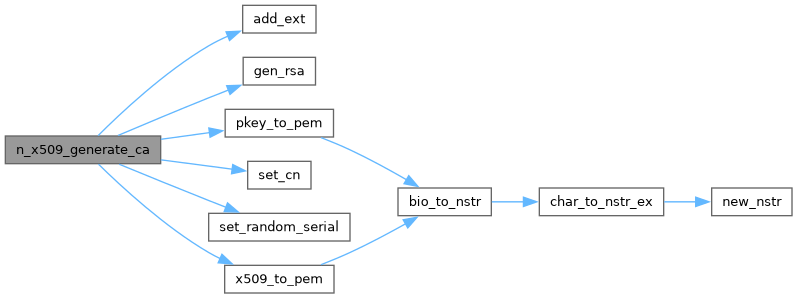
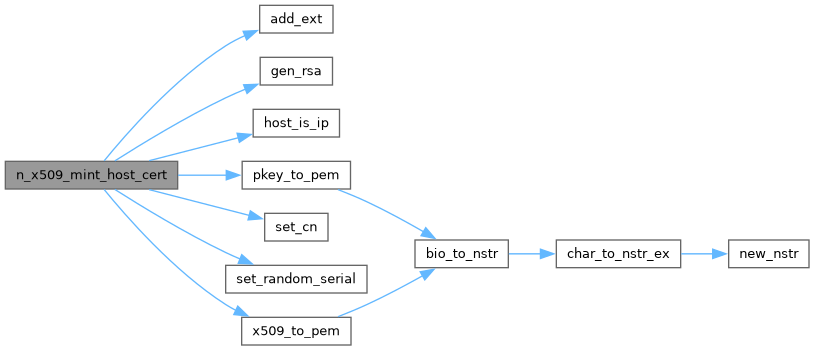
References __n_assert, add_ext(), free_nstr, gen_rsa(), LOG_ERR, n_log, N_X509_INIT, N_X509_KEY_BITS, pkey_to_pem(), set_cn(), set_random_serial(), X509_getm_notAfter, X509_getm_notBefore, and x509_to_pem().
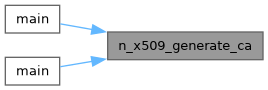
Referenced by main(), and main().
| int n_x509_keypair_pem | ( | int | bits, |
| N_STR ** | key_pem ) |
Generate an RSA private key and return it as a PEM string.
| bits | RSA modulus size in bits (for example 2048). |
| key_pem | out: newly allocated PEM private key, owned by the caller. |
Definition at line 209 of file n_x509.c.
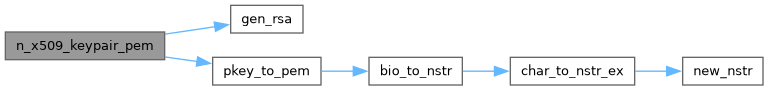
References __n_assert, gen_rsa(), LOG_ERR, n_log, N_X509_INIT, N_X509_KEY_BITS, and pkey_to_pem().
Referenced by main().
| int n_x509_mint_host_cert | ( | const char * | host, |
| const N_STR * | ca_cert_pem, | ||
| const N_STR * | ca_key_pem, | ||
| int | days, | ||
| N_STR ** | leaf_cert_pem, | ||
| N_STR ** | leaf_key_pem ) |
Mint a per-host leaf certificate signed by the given CA.
The leaf has basicConstraints CA:FALSE, extendedKeyUsage serverAuth, a subjectAltName of DNS:host (or IP:host when host is a literal IP address), a fresh random serial, and is signed with the CA key using SHA-256. Cache the result per host to avoid re-minting on every connection.
| host | the requested host name (or IP) to certify. |
| ca_cert_pem | the CA certificate PEM (issuer). |
| ca_key_pem | the CA private key PEM (signer). |
| days | validity in days from now. |
| leaf_cert_pem | out: newly allocated leaf certificate PEM, owned by the caller. |
| leaf_key_pem | out: newly allocated leaf private key PEM, owned by the caller. |
Definition at line 285 of file n_x509.c.
References __n_assert, add_ext(), N_STR::data, free_nstr, gen_rsa(), host_is_ip(), LOG_ERR, n_log, N_X509_INIT, N_X509_KEY_BITS, N_X509_SAN_BUF, pkey_to_pem(), set_cn(), set_random_serial(), N_STR::written, X509_getm_notAfter, X509_getm_notBefore, and x509_to_pem().
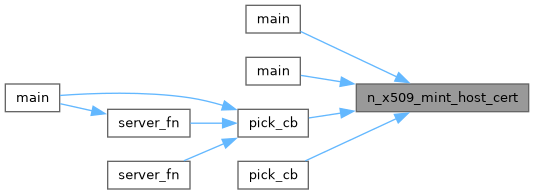
Referenced by main(), main(), pick_cb(), and pick_cb().
 1.15.0