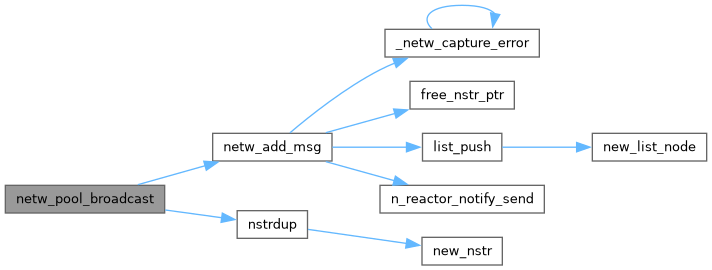
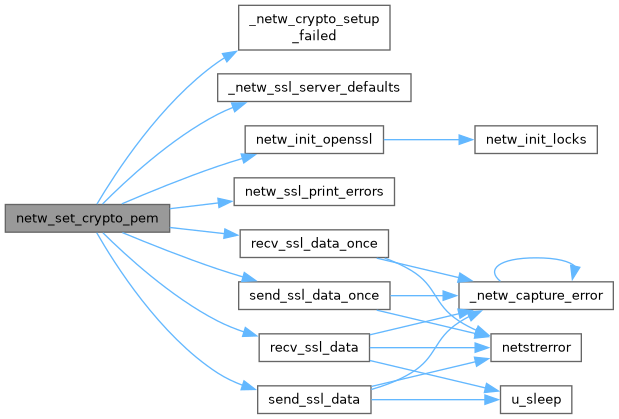
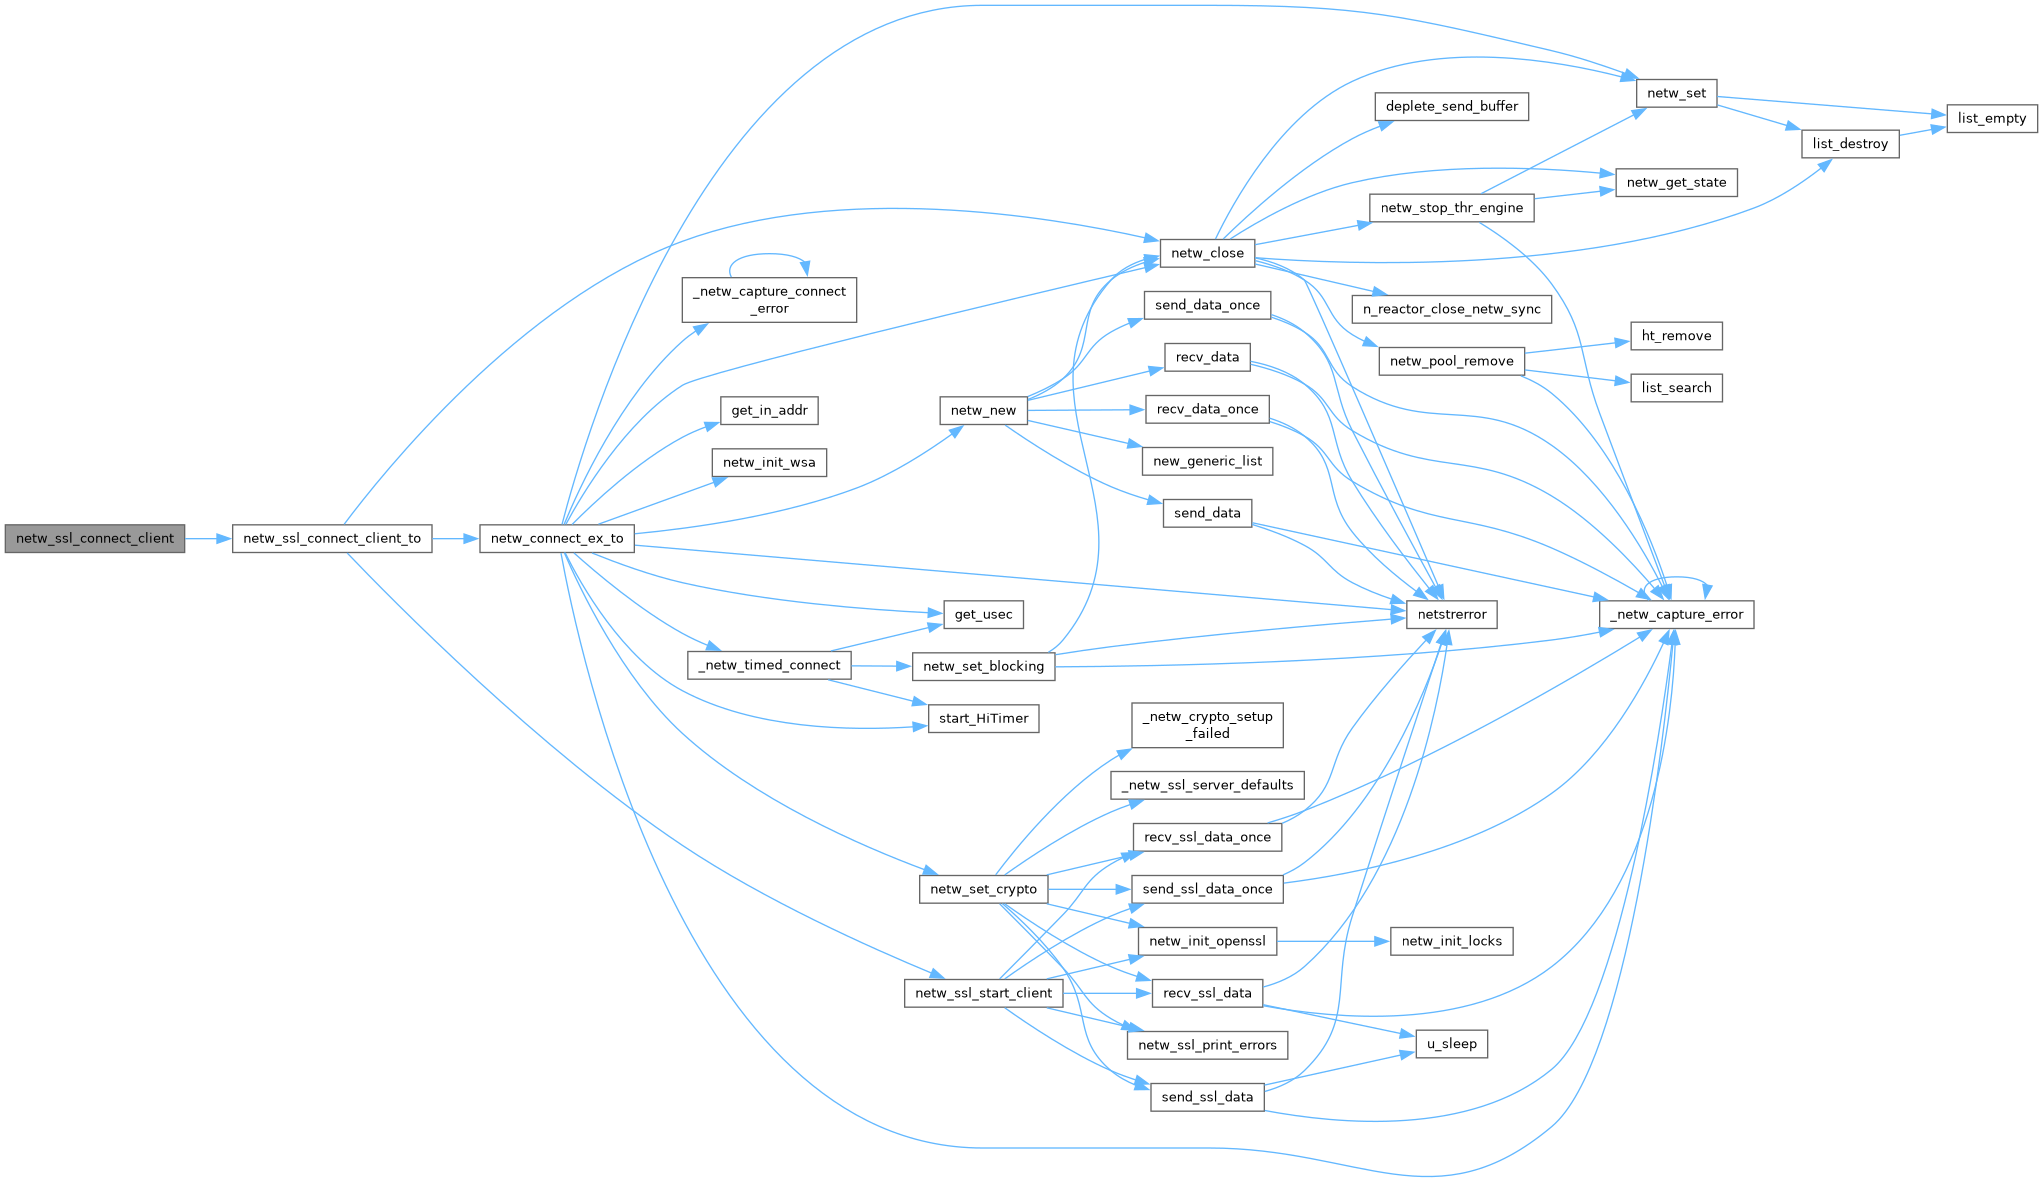
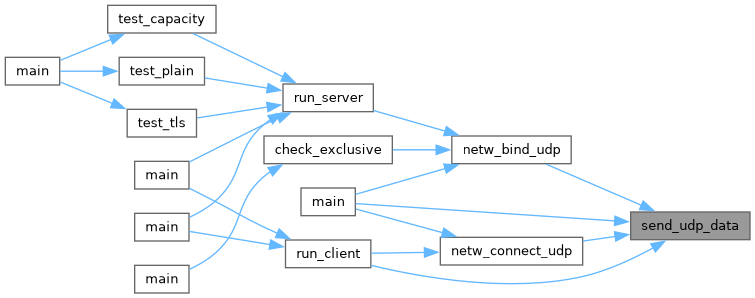
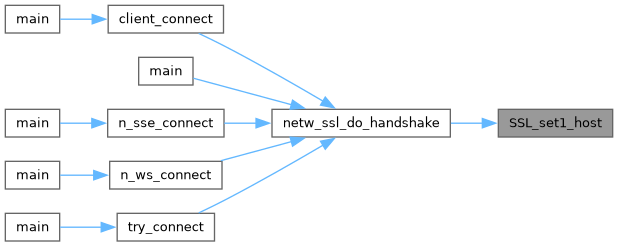
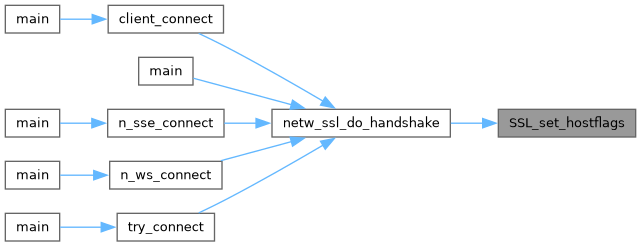
|
Nilorea Library
C utilities for networking, threading, graphics
|
|
Nilorea Library
C utilities for networking, threading, graphics
|
Data Structures | |
| struct | N_HTTP_MULTIPART_PART |
| a single part of a parsed multipart/form-data body More... | |
| struct | N_HTTP_REQUEST |
| parsed HTTP request for mock server callback More... | |
| struct | N_HTTP_RESPONSE |
| HTTP response to send from mock server callback. More... | |
| struct | N_MOCK_SERVER |
| mock HTTP server handle More... | |
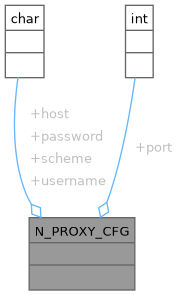
| struct | N_PROXY_CFG |
| Parsed proxy URL components. More... | |
| struct | N_SOCKET |
| Structure of a N_SOCKET. More... | |
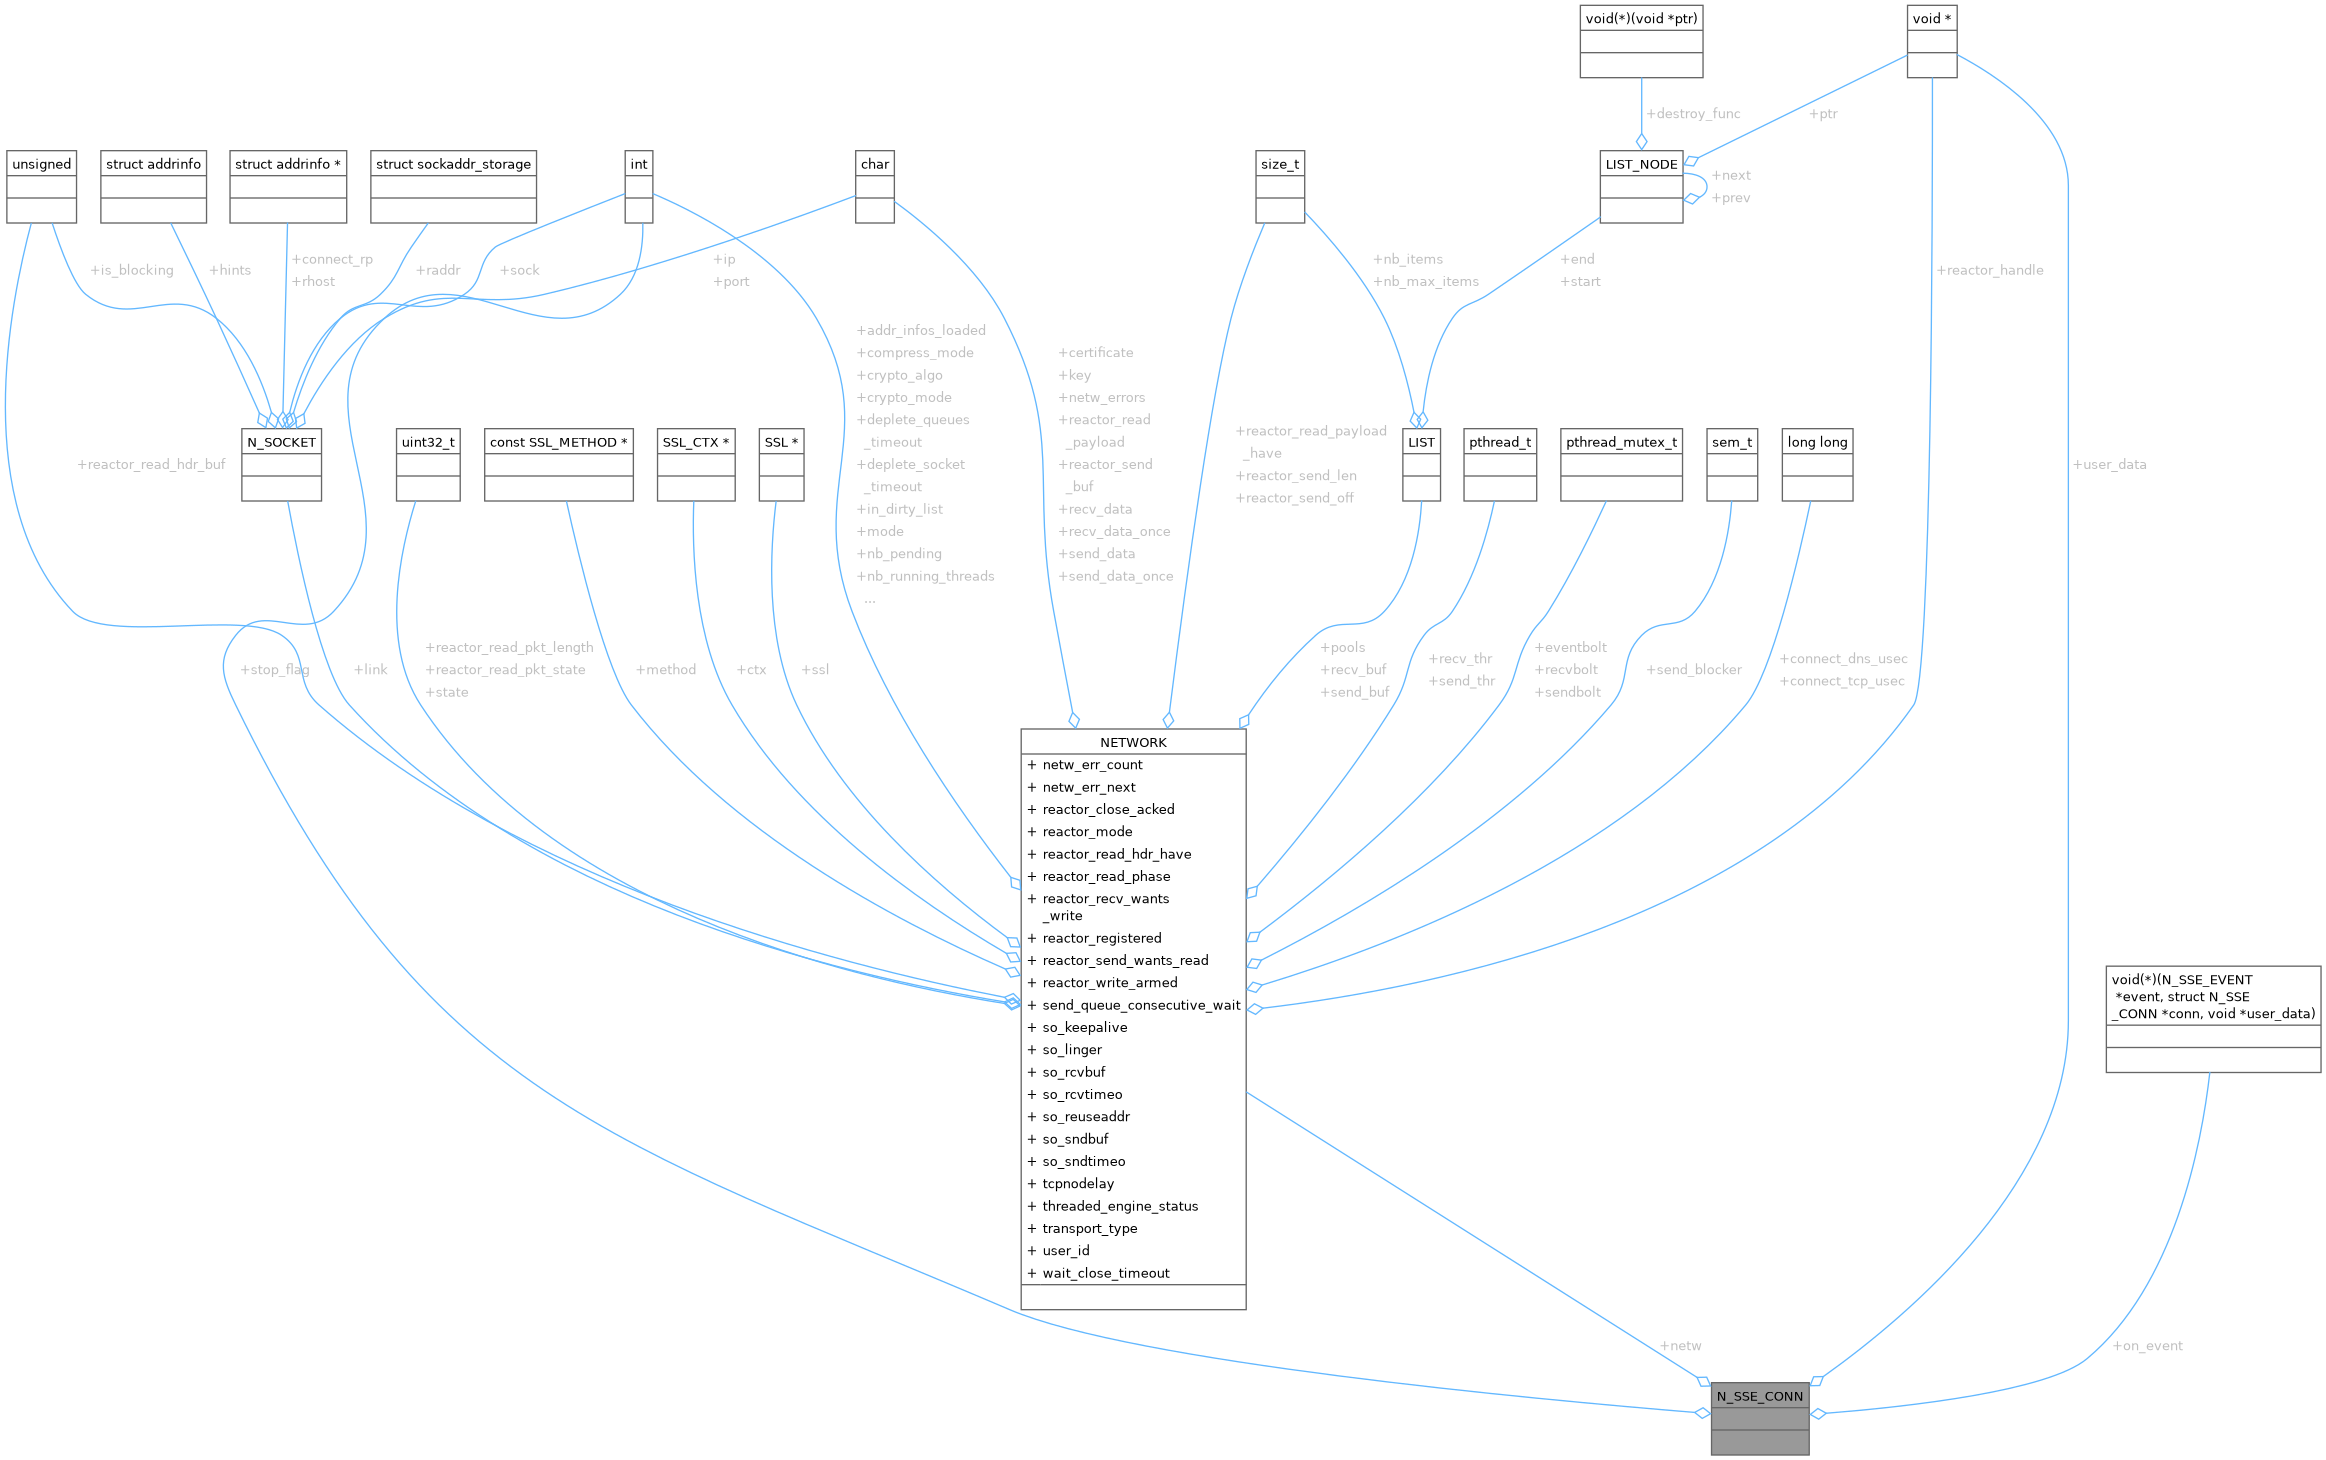
| struct | N_SSE_CONN |
| SSE connection handle. More... | |
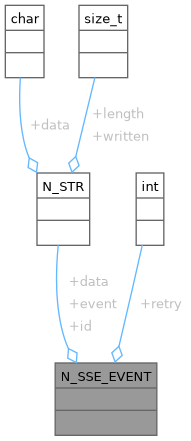
| struct | N_SSE_EVENT |
| SSE event received from server. More... | |
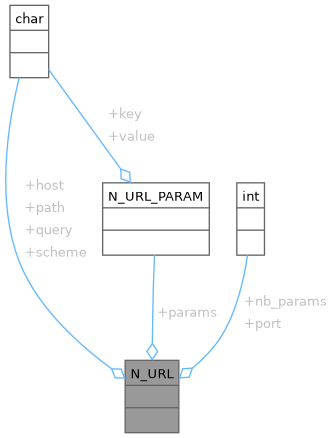
| struct | N_URL |
| parsed URL components More... | |
| struct | N_URL_PARAM |
| a single query parameter key=value pair More... | |
| struct | N_WS_CONN |
| WebSocket connection. More... | |
| struct | N_WS_FRAME |
| A single parsed WebSocket frame (RFC 6455). More... | |
| struct | N_WS_MESSAGE |
| WebSocket message. More... | |
| struct | NETWORK |
| Structure of a NETWORK. More... | |
| struct | NETWORK_HTTP_INFO |
| structure for splitting HTTP requests More... | |
| struct | NETWORK_POOL |
| structure of a network pool More... | |
Macros | |
| #define | _OPEN_SYS_SOCK_IPV6 1 |
| #define | HEAD_CODE 3 |
| Code of a HEAD message. | |
| #define | HEAD_SIZE 10 |
| Size of a HEAD message. | |
| #define | N_ENUM_netw_code_type(_) |
| Network codes definition. | |
| #define | N_URL_MAX_PARAMS 64 |
| maximum number of parsed query parameters | |
| #define | N_WS_MAX_PAYLOAD (64 * 1024 * 1024) |
| Largest WebSocket payload n_ws_recv() will accept from a peer, in bytes. | |
| #define | N_WS_OP_BINARY 0x02 |
| #define | N_WS_OP_CLOSE 0x08 |
| #define | N_WS_OP_PING 0x09 |
| #define | N_WS_OP_PONG 0x0A |
| #define | N_WS_OP_TEXT 0x01 |
| WebSocket opcodes per RFC 6455. | |
| #define | netw_atomic_read_reactor_handle(netw) |
| Same contract for the back-pointer to the reactor. | |
| #define | netw_atomic_read_reactor_mode(netw) |
| Lock-free atomic read of the reactor_mode flag. | |
| #define | netw_atomic_read_state(netw) |
| Lock-free atomic read of the network state field. | |
| #define | netw_atomic_write_reactor_handle(netw, val) |
| #define | netw_atomic_write_reactor_mode(netw, val) |
| #define | netw_atomic_write_state(netw, val) |
| Lock-free atomic write of the network state field. | |
| #define | NETW_COMPRESS_MIN_RATIO 10u |
| #define | NETW_COMPRESS_THRESHOLD 256u |
| Opportunistic compression policy. | |
| #define | NETW_COMPRESSED NETW_COMPRESSED_ZLIB |
| Legacy alias, the first compression commit shipped a single NETW_COMPRESSED flag before LZ4 was added. | |
| #define | NETW_HAVE_TLS13 N_OSSL_HAVE_TLS13 |
| 1 when the linked TLS library can negotiate TLS 1.3, 0 otherwise. | |
| #define | NETW_IO_WANT_READ -10 |
| single-attempt I/O (send_data_once / recv_data_once): the operation cannot progress until the socket is READABLE. | |
| #define | NETW_IO_WANT_WRITE -11 |
| single-attempt I/O: the operation cannot progress until the socket is WRITABLE. | |
| #define | NETW_MAX_RETRIES 8 |
| Send or recv max number of retries. | |
| #define | NETW_MSG_MAX_FRAME_SIZE (1024UL * 1024UL * 1024UL) |
| Maximum accepted size, in bytes, of a single received message frame payload. | |
| #define | NETW_RETRY_DELAY 1000 |
| Send or recv delay between retries in usec. | |
| #define | NETW_SOCKET_DISCONNECTED -2 |
| Code for a disconnected recv. | |
| #define | NETW_SOCKET_ERROR -1 |
| code for a socket error | |
| #define | NETW_THR_EXIT_ERROR 666 |
| Internal DONE value indicating a send/recv thread observed NETW_ERROR without an in-flight local shutdown. | |
| #define | NETW_THR_EXIT_OK 100 |
| Internal DONE value indicating a send/recv thread reached end-of-life cleanly (peer QUIT or local NETW_EXIT_ASKED ack'd). | |
| #define | NETW_TLS_MAX_VERSION TLS1_2_VERSION |
| highest TLS version the linked TLS library can negotiate, as a TLS*_VERSION constant. | |
| #define | NETWORK_CONSECUTIVE_SEND_WAIT 2048 |
| Flag to set consecutive send waiting timeout. | |
| #define | NETWORK_DEPLETE_QUEUES_TIMEOUT 1024 |
| Flag to set network queues depletion timeout. | |
| #define | NETWORK_DEPLETE_SOCKET_TIMEOUT 512 |
| Flag to set send buffer depletion timeout. | |
| #define | NETWORK_DISABLE_ZERO_LENGTH_RECV FALSE |
| Enable/disable recv of length 0. | |
| #define | NETWORK_IPALL 0 |
| Flag for auto detection by OS of ip version to use. | |
| #define | NETWORK_IPV4 1 |
| Flag to force IPV4. | |
| #define | NETWORK_IPV6 2 |
| Flag to force IPV6. | |
| #define | NETWORK_TCP 0 |
| Flag for TCP transport (default). | |
| #define | NETWORK_UDP 1 |
| Flag for UDP transport. | |
| #define | NETWORK_WAIT_CLOSE_TIMEOUT 4096 |
| Flag to set network closing wait timeout. | |
| #define | SOCKET_SIZE_FORMAT "%d" |
| socket associated printf style | |
| #define | SSL_get1_peer_certificate(ssl) |
Typedefs | |
| typedef ssize_t(* | netw_func) (void *, char *, uint32_t) |
| send/recv func ptr type | |
| typedef int(* | netw_sni_pick_cb) (const char *sni, N_STR **cert_pem, N_STR **key_pem, void *user_data) |
| SNI cert-pick callback for netw_accept_ssl_with_sni_cb: given the client SNI host (may be NULL), fill *cert_pem and *key_pem with a server certificate and key (newly allocated; n_network frees them). | |
| typedef int | SOCKET |
| default socket declaration | |
Enumerations | |
| enum | __netw_code_type { NETW_CLIENT = 2 , NETW_SERVER = 4 , NETW_RESTART_TIMER = 8 , NETW_EMPTY_SENDBUF = 16 , NETW_EMPTY_RECVBUF = 32 , NETW_RUN = 64 , NETW_EXIT_ASKED = 128 , NETW_EXITED = 256 , NETW_ERROR = 512 , NETW_ENCRYPT_NONE = 1024 , NETW_ENCRYPT_OPENSSL = 2048 , NETW_THR_ENGINE_STARTED = 4096 , NETW_THR_ENGINE_STOPPED = 8192 , NETW_DESTROY_RECVBUF = 16384 , NETW_DESTROY_SENDBUF = 32768 , NETW_COMPRESSED_ZLIB = 65536 , NETW_COMPRESSED_LZ4 = 131072 , ____netw_code_type_UNKNOWN_VALUE__ } |
| Network codes declaration. More... | |
| enum | NETW_COMPRESS_MODE { NETW_COMPRESS_NONE = 0 , NETW_COMPRESS_ZLIB = 1 , NETW_COMPRESS_LZ4 = 2 } |
| Compression mode selector for NETWORK.compress_mode. More... | |
Functions | |
| int | deplete_send_buffer (int fd, int timeout) |
| wait for send buffer to be empty | |
| size_t | htonst (size_t value) |
| host to network size_t | |
| N_STR * | n_http_build_multipart (LIST *parts, const char *boundary) |
| build a multipart/form-data body from a LIST of N_HTTP_MULTIPART_PART* using boundary (without "--"); returns a new N_STR (free with free_nstr) or NULL. | |
| int | n_http_decompress_body (const N_STR *body, const char *encoding, N_STR **out) |
| decompress an HTTP body per its Content-Encoding ("gzip"/"deflate"; identity/NULL/unknown copies through). | |
| int | n_http_multipart_boundary (const char *content_type, char *out, size_t outsz) |
| copy the boundary token from a Content-Type value into out (without the leading "--"). | |
| void | n_http_multipart_free (LIST **parts) |
| free a LIST returned by n_http_parse_multipart and NULL the pointer | |
| LIST * | n_http_parse_multipart (const N_STR *body, const char *boundary) |
| parse a multipart body (boundary given without "--") into a LIST of N_HTTP_MULTIPART_PART*; free with n_http_multipart_free. | |
| int | n_http_status_class (int status_code) |
| leading digit of an HTTP status code (1..5), or 0 when outside 100..599 | |
| int | n_http_status_is_client_error (int status_code) |
| 1 when status_code is a client error (4xx), else 0 | |
| int | n_http_status_is_informational (int status_code) |
| 1 when status_code is informational (1xx), else 0 | |
| int | n_http_status_is_redirect (int status_code) |
| 1 when status_code is a redirect (3xx), else 0 | |
| int | n_http_status_is_server_error (int status_code) |
| 1 when status_code is a server error (5xx), else 0 | |
| int | n_http_status_is_success (int status_code) |
| 1 when status_code is success (2xx), else 0 | |
| void | n_mock_server_free (N_MOCK_SERVER **server) |
| free a mock server and close the listening socket | |
| void | n_mock_server_run (N_MOCK_SERVER *server) |
| run the mock server accept loop (blocks until stop_flag is set) | |
| N_MOCK_SERVER * | n_mock_server_start (int port, void(*on_request)(N_HTTP_REQUEST *, N_HTTP_RESPONSE *, void *), void *user_data) |
| start a mock HTTP server on localhost:port (returns immediately) | |
| void | n_mock_server_stop (N_MOCK_SERVER *server) |
| signal the mock server to stop accepting connections | |
| void | n_netw_clear_connect_errors (void) |
| Clear pre-connection errors on this thread. | |
| void | n_netw_clear_errors (NETWORK *netw) |
| Clear captured errors on a NETWORK handle. | |
| const char * | n_netw_get_connect_error (int index) |
| Get pre-connection error message by index. | |
| int | n_netw_get_connect_error_count (void) |
| Get number of pre-connection errors captured on this thread. | |
| const char * | n_netw_get_error (const NETWORK *netw, int index) |
| Get captured error message by index (0 = oldest). | |
| int | n_netw_get_error_count (const NETWORK *netw) |
| Get number of captured errors on a NETWORK handle. | |
| void | n_proxy_cfg_free (N_PROXY_CFG **cfg) |
| Free an N_PROXY_CFG created by n_proxy_cfg_parse(). | |
| N_PROXY_CFG * | n_proxy_cfg_parse (const char *url) |
| Parse a proxy URL string into an N_PROXY_CFG struct. | |
| int | n_proxy_connect_socks5 (const N_PROXY_CFG *proxy, const char *target_host, int target_port) |
| Open a TCP connection through a SOCKS5 proxy. | |
| int | n_proxy_connect_tunnel (const N_PROXY_CFG *proxy, const char *target_host, int target_port) |
| Open a TCP connection through an HTTP proxy using CONNECT tunneling. | |
| int | n_proxy_connect_tunnel_ssl (const N_PROXY_CFG *proxy, const char *target_host, int target_port) |
| Open a TCP connection through an HTTPS proxy using CONNECT tunneling. | |
| void | n_sse_conn_free (N_SSE_CONN **conn) |
| free an SSE connection | |
| N_SSE_CONN * | n_sse_connect (const char *host, const char *port, const char *path, int use_ssl, const char *user_agent, void(*on_event)(N_SSE_EVENT *, N_SSE_CONN *, void *), void *user_data) |
| connect to an SSE endpoint and start reading events (blocks until stopped). | |
| void | n_sse_event_clean (N_SSE_EVENT *event) |
| free an SSE event's contents (does not free the event struct itself) | |
| void | n_sse_stop (N_SSE_CONN *conn) |
| signal the SSE connection to stop reading | |
| N_STR * | n_url_build (const N_URL *u) |
| build a URL string from parsed components | |
| N_STR * | n_url_canonicalize (const N_URL *u) |
| produce a canonical URL string for dedup (lowercase scheme/host, drop default port, remove . | |
| N_STR * | n_url_canonicalize_string (const char *url) |
| parse and canonicalize a URL string in one call | |
| N_STR * | n_url_decode (const char *str) |
| decode a percent-encoded string (returns N_STR) | |
| N_STR * | n_url_encode (const char *str) |
| percent-encode a string for use in URLs (delegates to n_str_url_encode()) | |
| void | n_url_free (N_URL **u) |
| free a N_URL and all its members | |
| N_URL * | n_url_parse (const char *url) |
| parse a URL string into components | |
| N_STR * | n_url_resolve (const char *base, const char *ref) |
| resolve a (possibly relative) reference against an absolute base URL (RFC 3986 section 5) | |
| void | n_ws_close (N_WS_CONN *conn) |
| send close frame and close the connection | |
| void | n_ws_conn_free (N_WS_CONN **conn) |
| free a WebSocket connection structure | |
| N_WS_CONN * | n_ws_connect (const char *host, const char *port, const char *path, int use_ssl) |
| connect to a WebSocket server (ws:// or wss://) and perform the HTTP/1.1 upgrade handshake | |
| size_t | n_ws_frame_build (int fin, int opcode, int do_mask, const unsigned char *payload, size_t len, const unsigned char mask_key[4], unsigned char *out, size_t out_cap) |
| build a WebSocket frame into out (optionally masking the payload). | |
| int | n_ws_frame_parse (const unsigned char *buf, size_t len, N_WS_FRAME *frame, size_t *consumed) |
| parse one WebSocket frame from a byte buffer (stateless). | |
| int | n_ws_recv (N_WS_CONN *conn, N_WS_MESSAGE *msg_out) |
| receive one WebSocket frame | |
| int | n_ws_send (N_WS_CONN *conn, const char *payload, size_t len, int opcode) |
| send a WebSocket frame (client always masks) | |
| void | n_ws_unmask (unsigned char *dst, const unsigned char *src, size_t len, const unsigned char mask[4]) |
| XOR-unmask len bytes of src into dst using a 4-byte WebSocket mask key. | |
| NETWORK * | netw_accept_from (NETWORK *from) |
| Accepting routine. | |
| NETWORK * | netw_accept_from_ex (NETWORK *from, size_t send_list_limit, size_t recv_list_limit, int blocking, int *retval) |
| Accepting routine extended. | |
| NETWORK * | netw_accept_nonblock_from (NETWORK *from, int blocking) |
| Accepting routine. | |
| NETWORK * | netw_accept_ssl_with_sni_cb (NETWORK *listen, netw_sni_pick_cb pick, void *user_data) |
| accept a TLS connection, selecting the server certificate per client SNI via pick() during the handshake | |
| int | netw_add_msg (NETWORK *netw, N_STR *msg) |
| Add a message to send in aimed NETWORK. | |
| int | netw_add_msg_ex (NETWORK *netw, char *str, unsigned int length) |
| Add a char message to send in the aimed NETWORK. | |
| int | netw_adopt_client_fd (NETWORK **netw, SOCKET fd, const char *host, const char *port) |
| adopt an already-connected socket fd into a fresh client NETWORK (plain send/recv) | |
| int | netw_bind_udp (NETWORK **netw, char *addr, char *port, int ip_version) |
| Create a UDP bound socket. | |
| int | netw_build_http_response (N_STR **http_response, int status_code, const char *server_name, const char *content_type, char *additional_headers, N_STR *body) |
| build HTTP response | |
| size_t | netw_calculate_urlencoded_size (const char *str, size_t len) |
| calculate URL-encoded size | |
| int | netw_close (NETWORK **netw) |
| Closing. | |
| int | netw_connect (NETWORK **netw, char *host, char *port, int ip_version) |
| Connecting. | |
| int | netw_connect_check (NETWORK *netw) |
| advance a non-blocking connect: TRUE connected, NETW_IO_WANT_WRITE keep polling for writability, FALSE all addresses failed | |
| int | netw_connect_ex (NETWORK **netw, char *host, char *port, size_t send_list_limit, size_t recv_list_limit, int ip_version, char *ssl_key_file, char *ssl_cert_file) |
| Connecting, extended. | |
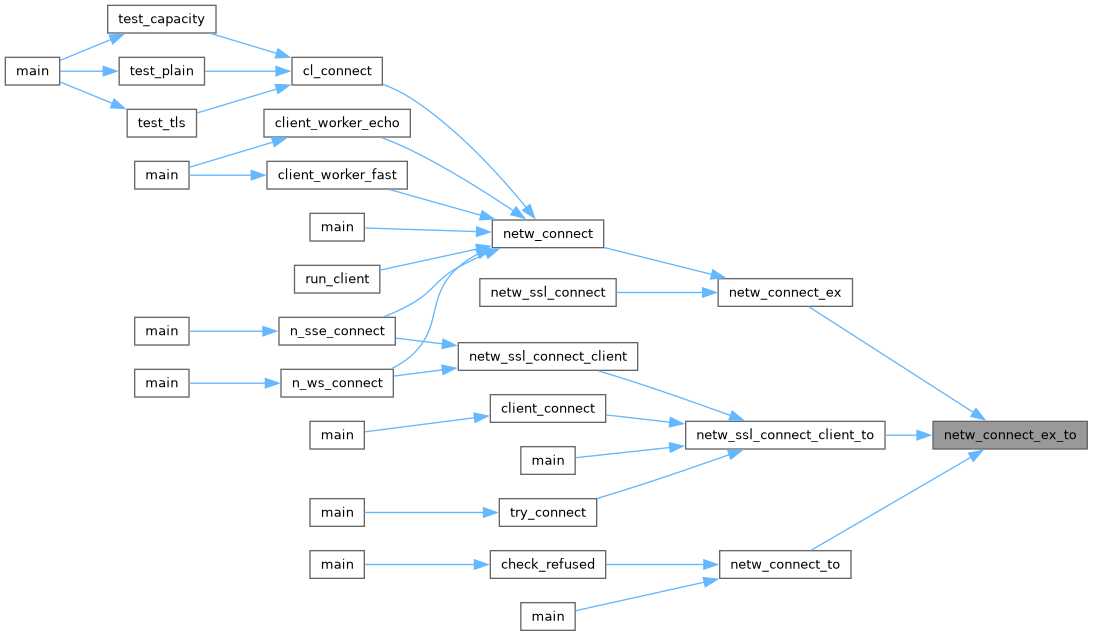
| int | netw_connect_ex_to (NETWORK **netw, char *host, char *port, size_t send_list_limit, size_t recv_list_limit, int ip_version, char *ssl_key_file, char *ssl_cert_file, int connect_timeout_ms) |
| Connecting, extended, with a bounded connection-establishment time (connect_timeout_ms, 0 = OS default). | |
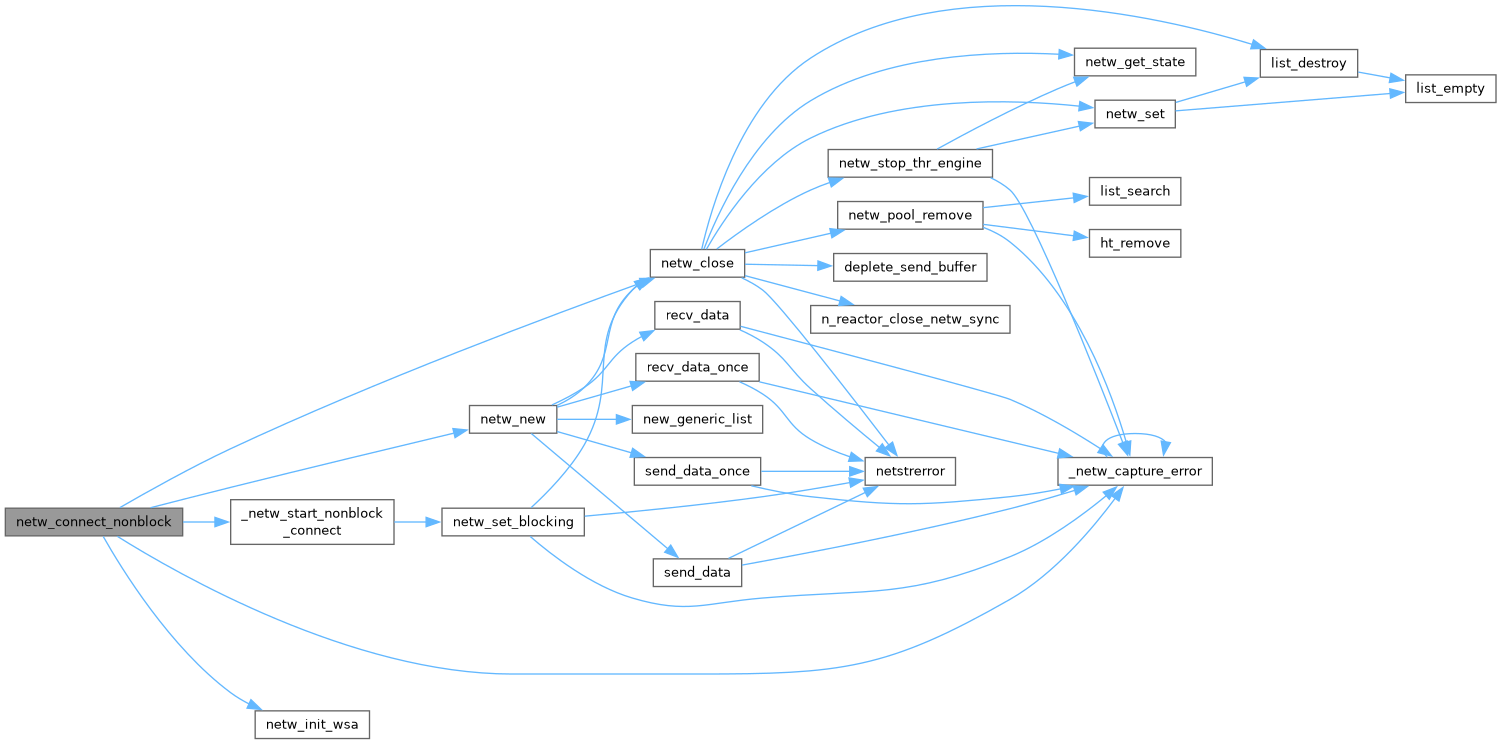
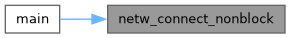
| int | netw_connect_nonblock (NETWORK **netw, char *host, char *port, int ip_version) |
| begin a non-blocking TCP connect: resolve and initiate connect() without waiting; drive to completion with netw_connect_check() | |
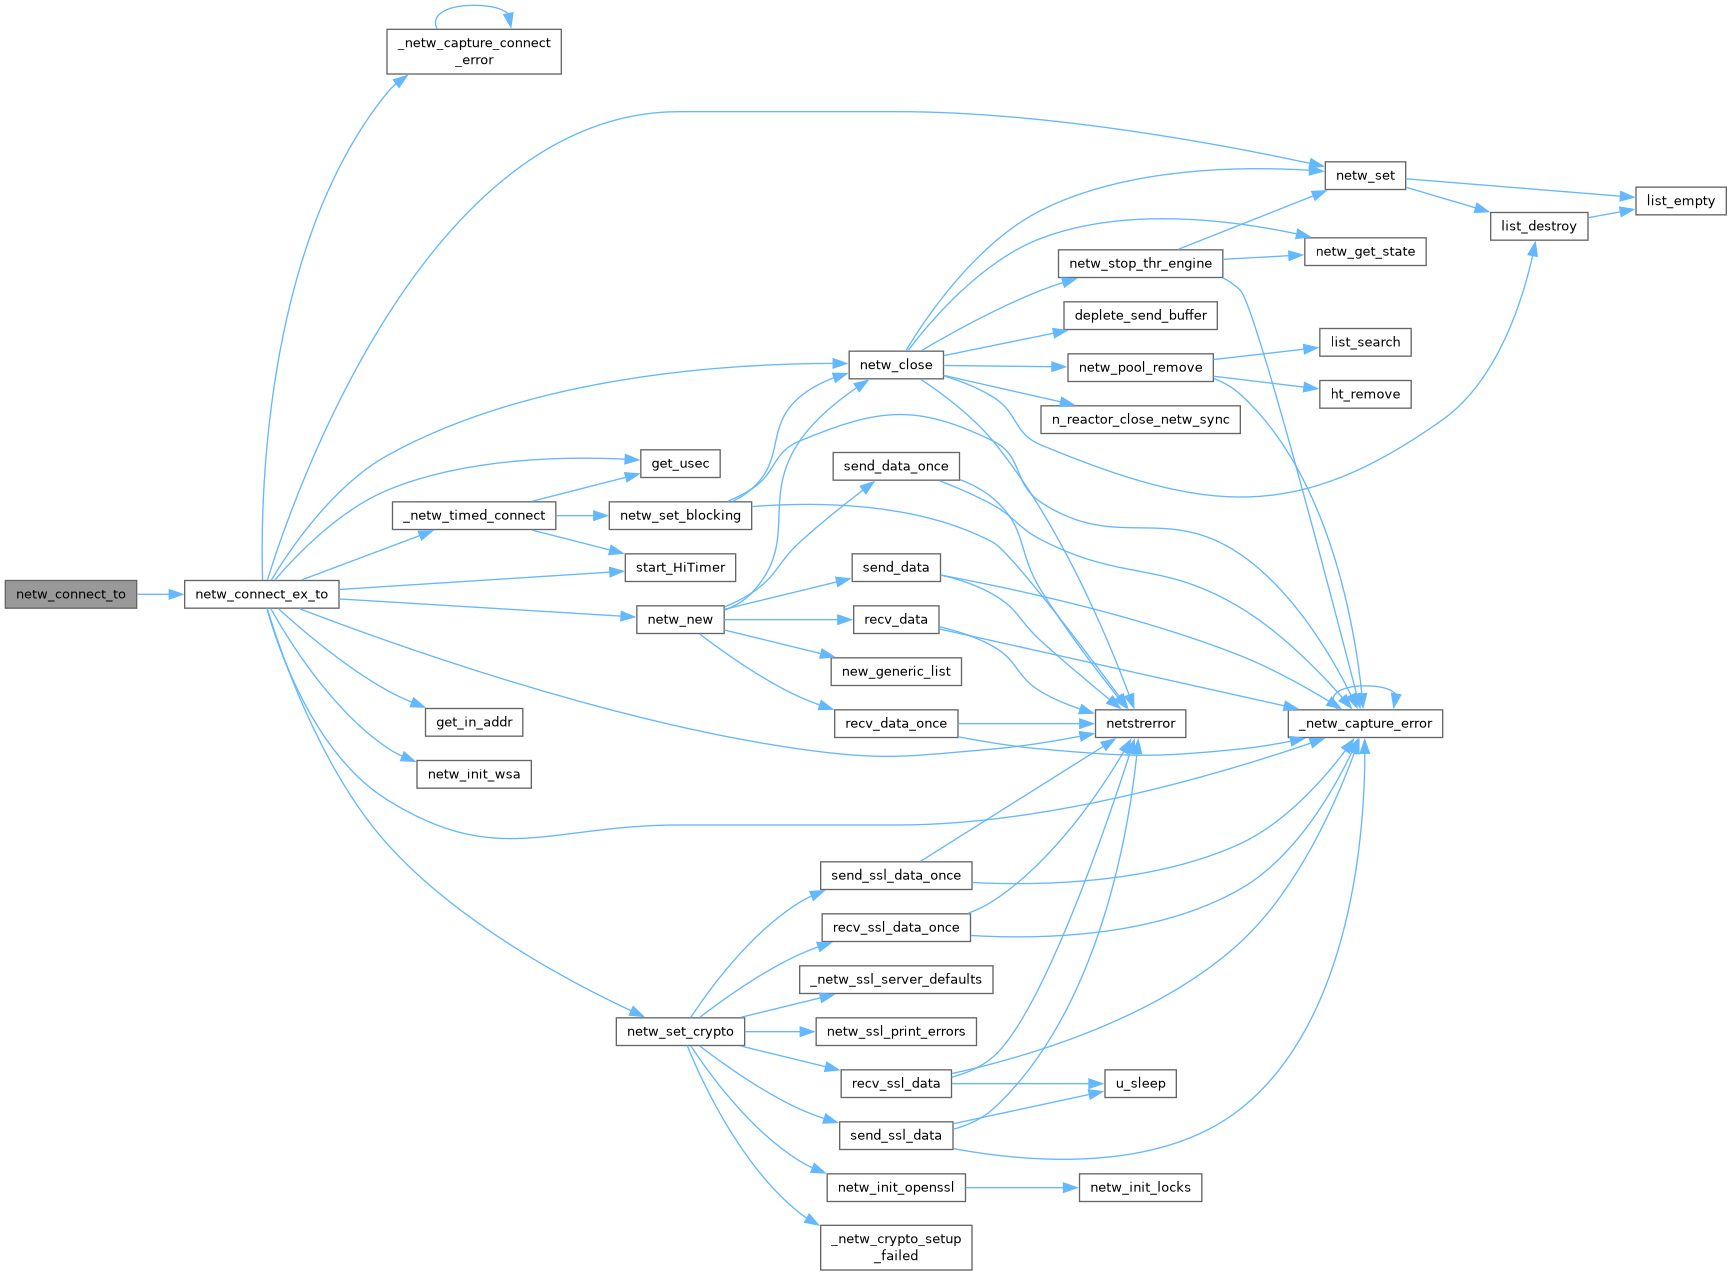
| int | netw_connect_to (NETWORK **netw, char *host, char *port, int ip_version, int connect_timeout_ms) |
| Connecting, with a bounded connection-establishment time (connect_timeout_ms, 0 = OS default). | |
| int | netw_connect_udp (NETWORK **netw, char *host, char *port, int ip_version) |
| Connect a UDP socket to a remote host. | |
| int | netw_destroy_pool (NETWORK_POOL **netw_pool) |
| destroy pool | |
| NETWORK_HTTP_INFO | netw_extract_http_info (char *request) |
| extract HTTP info from request | |
| char * | netw_extract_http_request_type (const char *request) |
| extract HTTP request type | |
| int | netw_get_http_date (char *buffer, size_t buffer_size) |
| get current HTTP date string | |
| const char * | netw_get_http_status_message (int status_code) |
| get HTTP status message string | |
| N_STR * | netw_get_msg (NETWORK *netw) |
| Get a message from aimed NETWORK. | |
| int | netw_get_queue_status (NETWORK *netw, size_t *nb_to_send, size_t *nb_to_read) |
| get queue status | |
| int | netw_get_state (NETWORK *netw, uint32_t *state, int *thr_engine_status) |
| Get flags from network. | |
| int | netw_get_url_from_http_request (const char *request, char *url, size_t size) |
| get URL from HTTP request | |
| const char * | netw_guess_http_content_type (const char *url) |
| guess HTTP content type from URL | |
| int | netw_info_destroy (NETWORK_HTTP_INFO http_request) |
| destroy HTTP info structure | |
| int | netw_init_openssl (void) |
| init ssl helper | |
| int | netw_init_wsa (int mode, int v1, int v2) |
| Used by Init & Close network. | |
| int | netw_make_listening (NETWORK **netw, char *addr, char *port, int nbpending, int ip_version) |
| Listening network. | |
| NETWORK_POOL * | netw_new_pool (size_t nb_min_element) |
| init pools | |
| HASH_TABLE * | netw_parse_post_data (const char *post_data) |
| parse POST data into hash table | |
| int | netw_pool_add (NETWORK_POOL *netw_pool, NETWORK *netw) |
| add network to pool | |
| int | netw_pool_broadcast (NETWORK_POOL *netw_pool, const NETWORK *from, N_STR *net_msg) |
| broadcast message to pool | |
| size_t | netw_pool_nbclients (NETWORK_POOL *netw_pool) |
| get nb clients | |
| void | netw_pool_netw_close (void *netw_ptr) |
| close pool | |
| int | netw_pool_remove (NETWORK_POOL *netw_pool, NETWORK *netw) |
| remove network from pool | |
| void * | netw_recv_func (void *NET) |
| Thread Receiving management function. | |
| void * | netw_send_func (void *NET) |
| Thread Sending management function. | |
| int | netw_send_ident (NETWORK *netw, int type, int id, N_STR *name, N_STR *passwd) |
| send ident message | |
| int | netw_send_ping (NETWORK *netw, int type, int id_from, int id_to, int time) |
| send ping message | |
| int | netw_send_position (NETWORK *netw, int id, double X, double Y, double vx, double vy, double acc_x, double acc_y, int time_stamp) |
| send position message | |
| int | netw_send_quit (NETWORK *netw) |
| send quit message | |
| int | netw_send_string_to (NETWORK *netw, int id_to, N_STR *name, N_STR *chan, N_STR *txt, int color) |
| send string to a specific target | |
| int | netw_send_string_to_all (NETWORK *netw, N_STR *name, N_STR *chan, N_STR *txt, int color) |
| send string to all targets | |
| int | netw_set (NETWORK *netw, int flag) |
| Set flags on network. | |
| int | netw_set_blocking (NETWORK *netw, unsigned long int is_blocking) |
| set blocking mode | |
| int | netw_set_compression_mode (NETWORK *netw, int mode) |
| Pick send-side compression algorithm for this NETWORK: NETW_COMPRESS_NONE, _ZLIB, _LZ4. | |
| void | netw_set_connect_abort_cb (int(*cb)(void *ctx), void *ctx) |
| register a process-wide callback polled during connect; non-zero aborts the in-progress connect (NULL removes) | |
| int | netw_set_crypto (NETWORK *netw, char *key, char *certificate) |
| set SSL | |
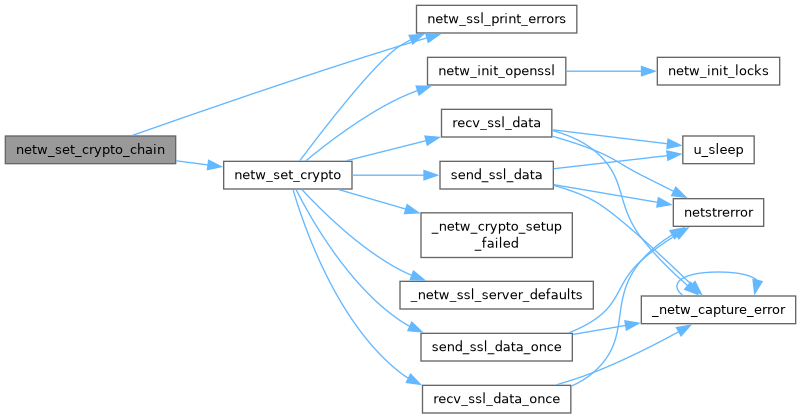
| int | netw_set_crypto_chain (NETWORK *netw, char *key, char *certificate, char *ca_file) |
| set SSL certificate chain from PEM file | |
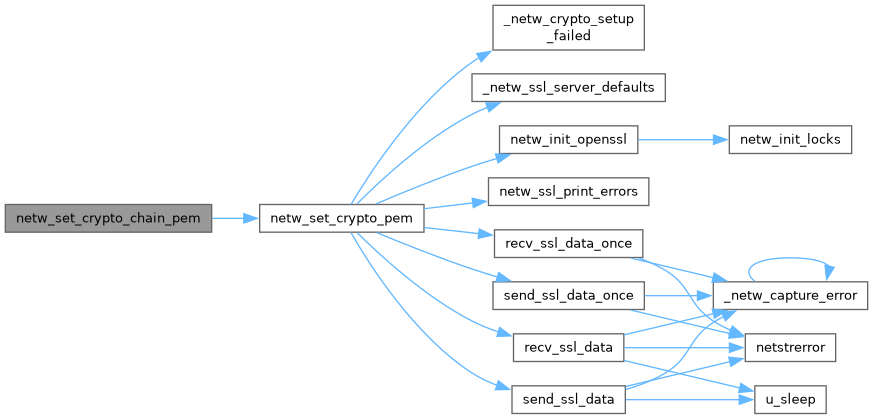
| int | netw_set_crypto_chain_pem (NETWORK *netw, const char *key_pem, const char *cert_pem, const char *ca_pem) |
| set SSL certificate chain from PEM strings in memory | |
| int | netw_set_crypto_pem (NETWORK *netw, const char *key_pem, const char *cert_pem) |
| set SSL from PEM strings in memory | |
| int | netw_set_crypto_pem_ctx (NETWORK *netw, const N_STR *key_pem, const N_STR *cert_pem) |
| install an in-memory cert/key on THIS connection's SSL only (per-connection, unlike the context-wide netw_set_crypto_pem) | |
| int | netw_set_user_id (NETWORK *netw, int id) |
| set user id on a netw | |
| int | netw_setsockopt (NETWORK *netw, int optname, int value) |
| Set common socket options (disable naggle, send/recv buf, reuse addr). | |
| int | netw_ssl_connect (NETWORK **netw, char *host, char *port, int ip_version, char *ssl_key_file, char *ssl_cert_file) |
| connect ssl helper | |
| int | netw_ssl_connect_client (NETWORK **netw, char *host, char *port, int ip_version) |
| connect as SSL client without client certificate (TCP + SSL_CTX, no handshake yet) | |
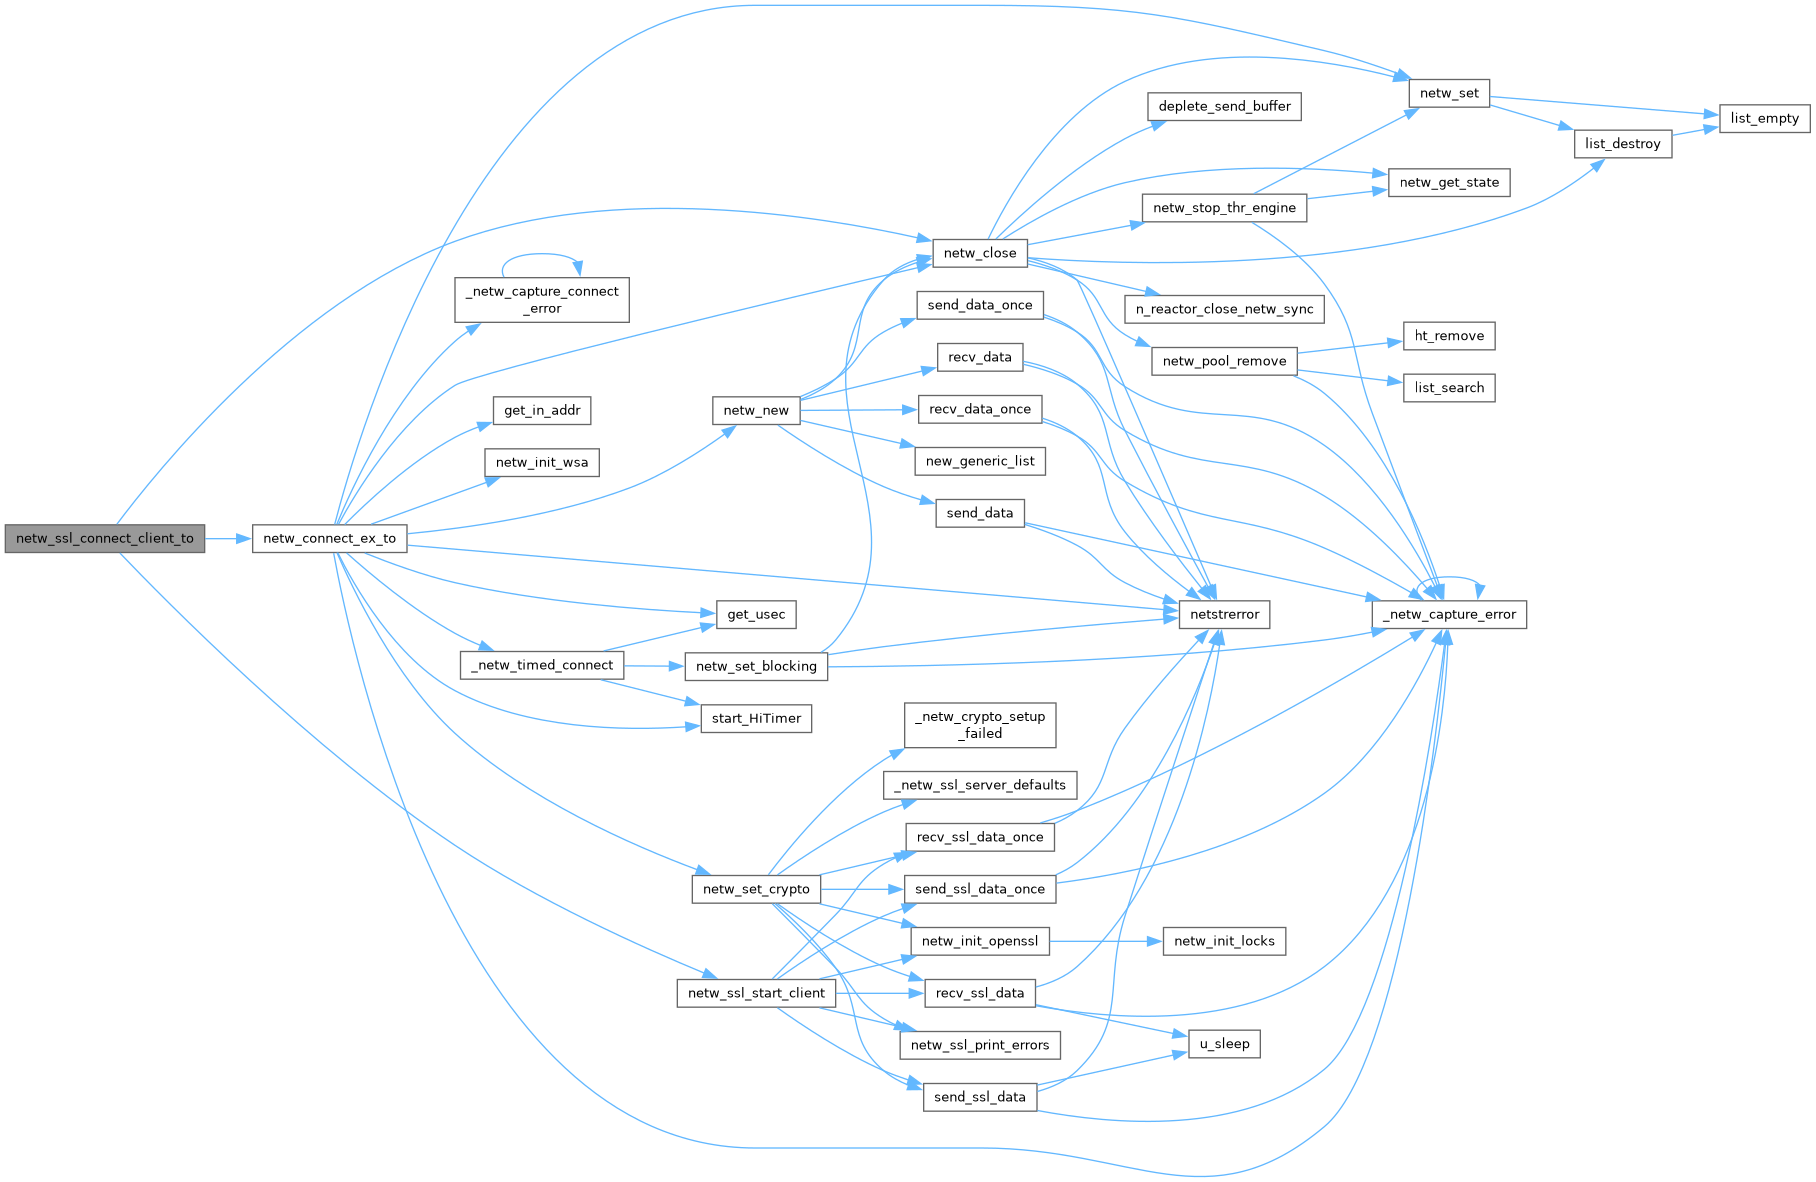
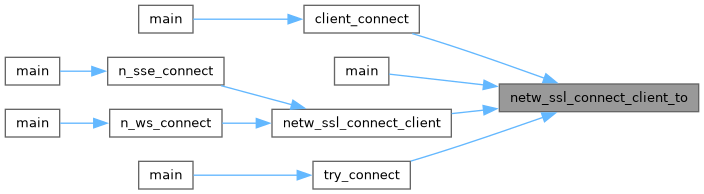
| int | netw_ssl_connect_client_to (NETWORK **netw, char *host, char *port, int ip_version, int connect_timeout_ms) |
| like netw_ssl_connect_client but bounds the TCP connect by connect_timeout_ms (0 = OS default) | |
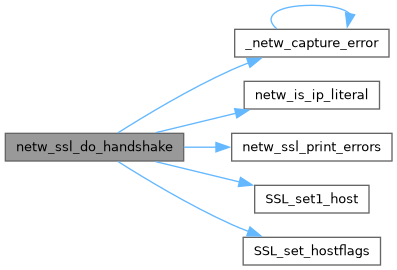
| int | netw_ssl_do_handshake (NETWORK *netw, const char *sni_hostname) |
| complete the SSL handshake on a NETWORK whose ctx was already created. | |
| int | netw_ssl_get_alpn (NETWORK *netw, char *out, size_t out_len) |
| get the ALPN protocol the completed handshake selected, on either side of the connection | |
| const char * | netw_ssl_get_sni (NETWORK *netw) |
| get the SNI server_name the peer requested in its ClientHello, or NULL | |
| int | netw_ssl_get_verify_result (NETWORK *netw, const char *expected_host, char *errbuf, size_t errsz) |
| evaluate the peer certificate (chain trust + host match) against the system trust store, independently of the connection verify mode | |
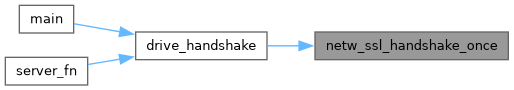
| int | netw_ssl_handshake_once (NETWORK *netw, const char *sni_hostname) |
| non-blocking (resumable) TLS client handshake: TRUE done, NETW_IO_WANT_READ/WRITE to retry, FALSE on error | |
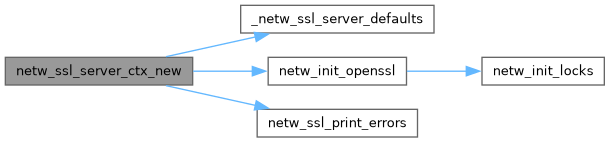
| SSL_CTX * | netw_ssl_server_ctx_new (const char *key_file, const char *cert_chain_file) |
| new standalone server SSL_CTX with the library's secure defaults (TLS 1.2+, forward-secret AEAD, no compression / renegotiation / tickets), the certificate chain and key loaded from PEM files and checked to match. | |
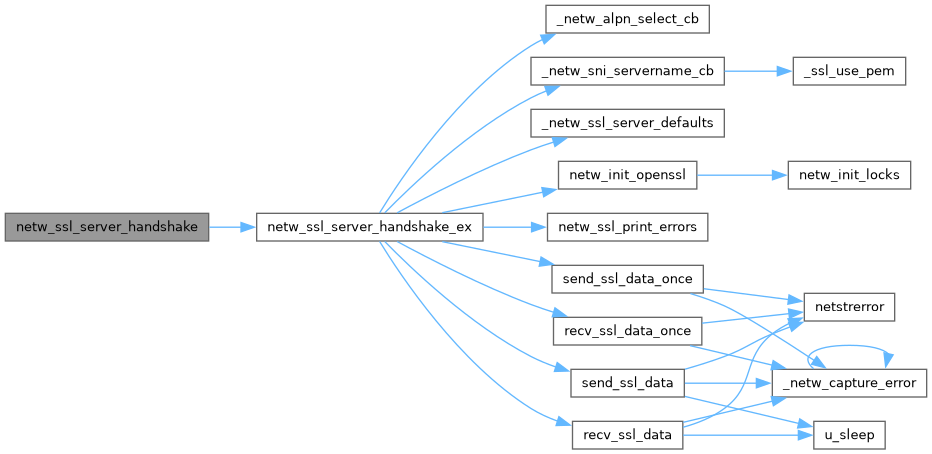
| int | netw_ssl_server_handshake (NETWORK *netw, netw_sni_pick_cb pick, void *user_data) |
| upgrade an already-accepted plaintext connection to a TLS server, selecting the cert per client SNI via pick() during the handshake (for proxy CONNECT) | |
| int | netw_ssl_server_handshake_ex (NETWORK *netw, netw_sni_pick_cb pick, void *user_data, const char *const *alpn, size_t alpn_count) |
| same, plus an ALPN offer: the first protocol of alpn the client also offered is selected (none when the two lists do not overlap) | |
| int | netw_ssl_server_handshake_once (NETWORK *netw, SSL_CTX *ctx) |
| non-blocking (resumable) TLS server handshake against a caller-owned shared ctx: TRUE done, NETW_IO_WANT_READ/WRITE to retry, FALSE on error | |
| int | netw_ssl_set_alpn (NETWORK *netw, const char *const *protos, size_t count) |
| offer an ALPN protocol list on a TLS client connection, before its handshake | |
| int | netw_ssl_set_ca (NETWORK *netw, const char *ca_file, const char *ca_path) |
| set custom CA verify path or file | |
| int | netw_ssl_set_ciphers (NETWORK *netw, const char *cipher_list, const char *ciphersuites) |
| set the TLS<=1.2 cipher list and/or the TLS1.3 ciphersuites (NULL leaves a default). | |
| int | netw_ssl_set_client_cert (NETWORK *netw, const char *cert_file, const char *key_file) |
| load client certificate and private key for mTLS | |
| int | netw_ssl_set_verify (NETWORK *netw, int enable) |
| enable or disable peer certificate verification | |
| int | netw_ssl_set_versions (NETWORK *netw, int min_version, int max_version) |
| set the minimum/maximum TLS protocol version on the connection's SSL context (0 leaves a default). | |
| int | netw_ssl_start_client (NETWORK *netw) |
| set up a client SSL_CTX on an already-connected NETWORK (no handshake yet) | |
| int | netw_start_thr_engine (NETWORK *netw) |
| Create the sending and receiving thread of a NETWORK. | |
| int | netw_stop_thr_engine (NETWORK *netw) |
| Stop a NETWORK connection sending and receiving thread. | |
| ssize_t | netw_udp_recvfrom (NETWORK *netw, char *buf, uint32_t n, struct sockaddr *src_addr, socklen_t *src_len) |
| UDP recvfrom with source address capture. | |
| ssize_t | netw_udp_sendto (NETWORK *netw, char *buf, uint32_t n, struct sockaddr *dest_addr, socklen_t dest_len) |
| UDP sendto with explicit destination. | |
| int | netw_unload_openssl (void) |
| unload ssl helper | |
| char * | netw_urldecode (const char *str) |
| URL-decode a string. | |
| char * | netw_urlencode (const char *str, size_t len) |
| URL-encode a string. | |
| int | netw_wait_close (NETWORK **netw) |
| Closing for peer. | |
| int | netw_wait_close_timed (NETWORK **netw, size_t timeout) |
| Closing for peer with timeout. | |
| N_STR * | netw_wait_msg (NETWORK *netw, unsigned int refresh, size_t timeout) |
| Wait a message from aimed NETWORK. | |
| size_t | ntohst (size_t value) |
| network to host size_t | |
| ssize_t | recv_data (void *netw, char *buf, uint32_t n) |
| Reading from a socket. | |
| ssize_t | recv_data_once (void *netw, char *buf, uint32_t n) |
| Single-attempt read (see NETWORK.recv_data_once contract). | |
| ssize_t | recv_php (SOCKET s, int *_code, char **buf) |
| receive from php | |
| ssize_t | recv_ssl_data (void *netw, char *buf, uint32_t n) |
| SSL Reading from a socket. | |
| ssize_t | recv_ssl_data_once (void *netw, char *buf, uint32_t n) |
| SSL single-attempt read (see recv_data_once contract). | |
| ssize_t | recv_udp_data (void *netw, char *buf, uint32_t n) |
| UDP recv data from socket. | |
| ssize_t | send_data (void *netw, char *buf, uint32_t n) |
| Writing to a socket. | |
| ssize_t | send_data_once (void *netw, char *buf, uint32_t n) |
| Single-attempt write (see NETWORK.send_data_once contract). | |
| ssize_t | send_php (SOCKET s, int _code, char *buf, int n) |
| sending to php | |
| ssize_t | send_ssl_data (void *netw, char *buf, uint32_t n) |
| SSL Writing to a socket. | |
| ssize_t | send_ssl_data_once (void *netw, char *buf, uint32_t n) |
| SSL single-attempt write (see send_data_once contract). | |
| ssize_t | send_udp_data (void *netw, char *buf, uint32_t n) |
| UDP send data to connected peer or specified addr. | |
| static int | SSL_set1_host (SSL *ssl, const char *host) |
| 1.0.2 stand-in for SSL_set1_host(): set the expected peer name of ssl, returning 1 on success and 0 on failure | |
| static void | SSL_set_hostflags (SSL *ssl, unsigned int flags) |
| 1.0.2 stand-in for SSL_set_hostflags(): set the X509_CHECK_FLAG_* host-check flags of ssl | |
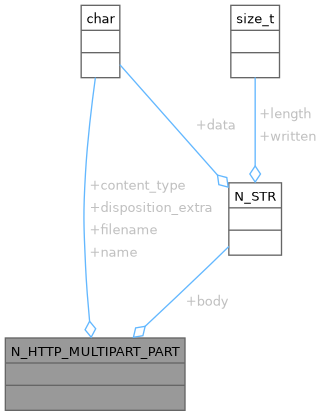
| struct N_HTTP_MULTIPART_PART |
a single part of a parsed multipart/form-data body
Definition at line 900 of file n_network.h.
| Data Fields | ||
|---|---|---|
| N_STR * | body | the part's raw body bytes (binary-safe), or NULL |
| char * | content_type | the part's Content-Type, or "" |
| char * | disposition_extra |
extra Content-Disposition parameters, appended verbatim after name (and filename) as written, without a leading separator: supply it including its own "; ". NULL or "" adds nothing. RFC 7578 leaves a receiver's handling of repeated or unknown parameters open, so this exists for a caller that must reproduce a specific header exactly (a compatibility quirk, or an authorized test of how two parsers read the same part). n_http_parse_multipart does not populate it, so a parse/build round-trip drops it. |
| char * | filename | Content-Disposition filename, or "". |
| char * | name | Content-Disposition form-field name, or "". |
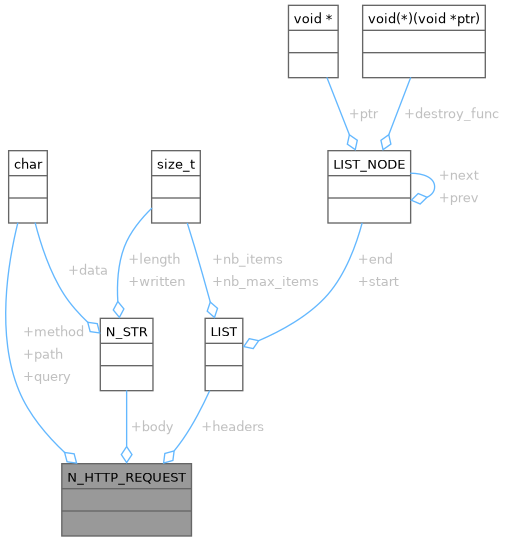
| struct N_HTTP_REQUEST |
parsed HTTP request for mock server callback
Definition at line 1162 of file n_network.h.
| Data Fields | ||
|---|---|---|
| N_STR * | body | request body (or NULL) |
| LIST * | headers | list of char* "Name: Value" strings |
| char | method[16] | HTTP method. |
| char | path[2048] | request path |
| char | query[2048] | query string (or empty) |
| struct N_HTTP_RESPONSE |
HTTP response to send from mock server callback.
Definition at line 1171 of file n_network.h.
| Data Fields | ||
|---|---|---|
| N_STR * | body | response body |
| char | content_type[128] | Content-Type header value. |
| int | status_code | HTTP status code. |
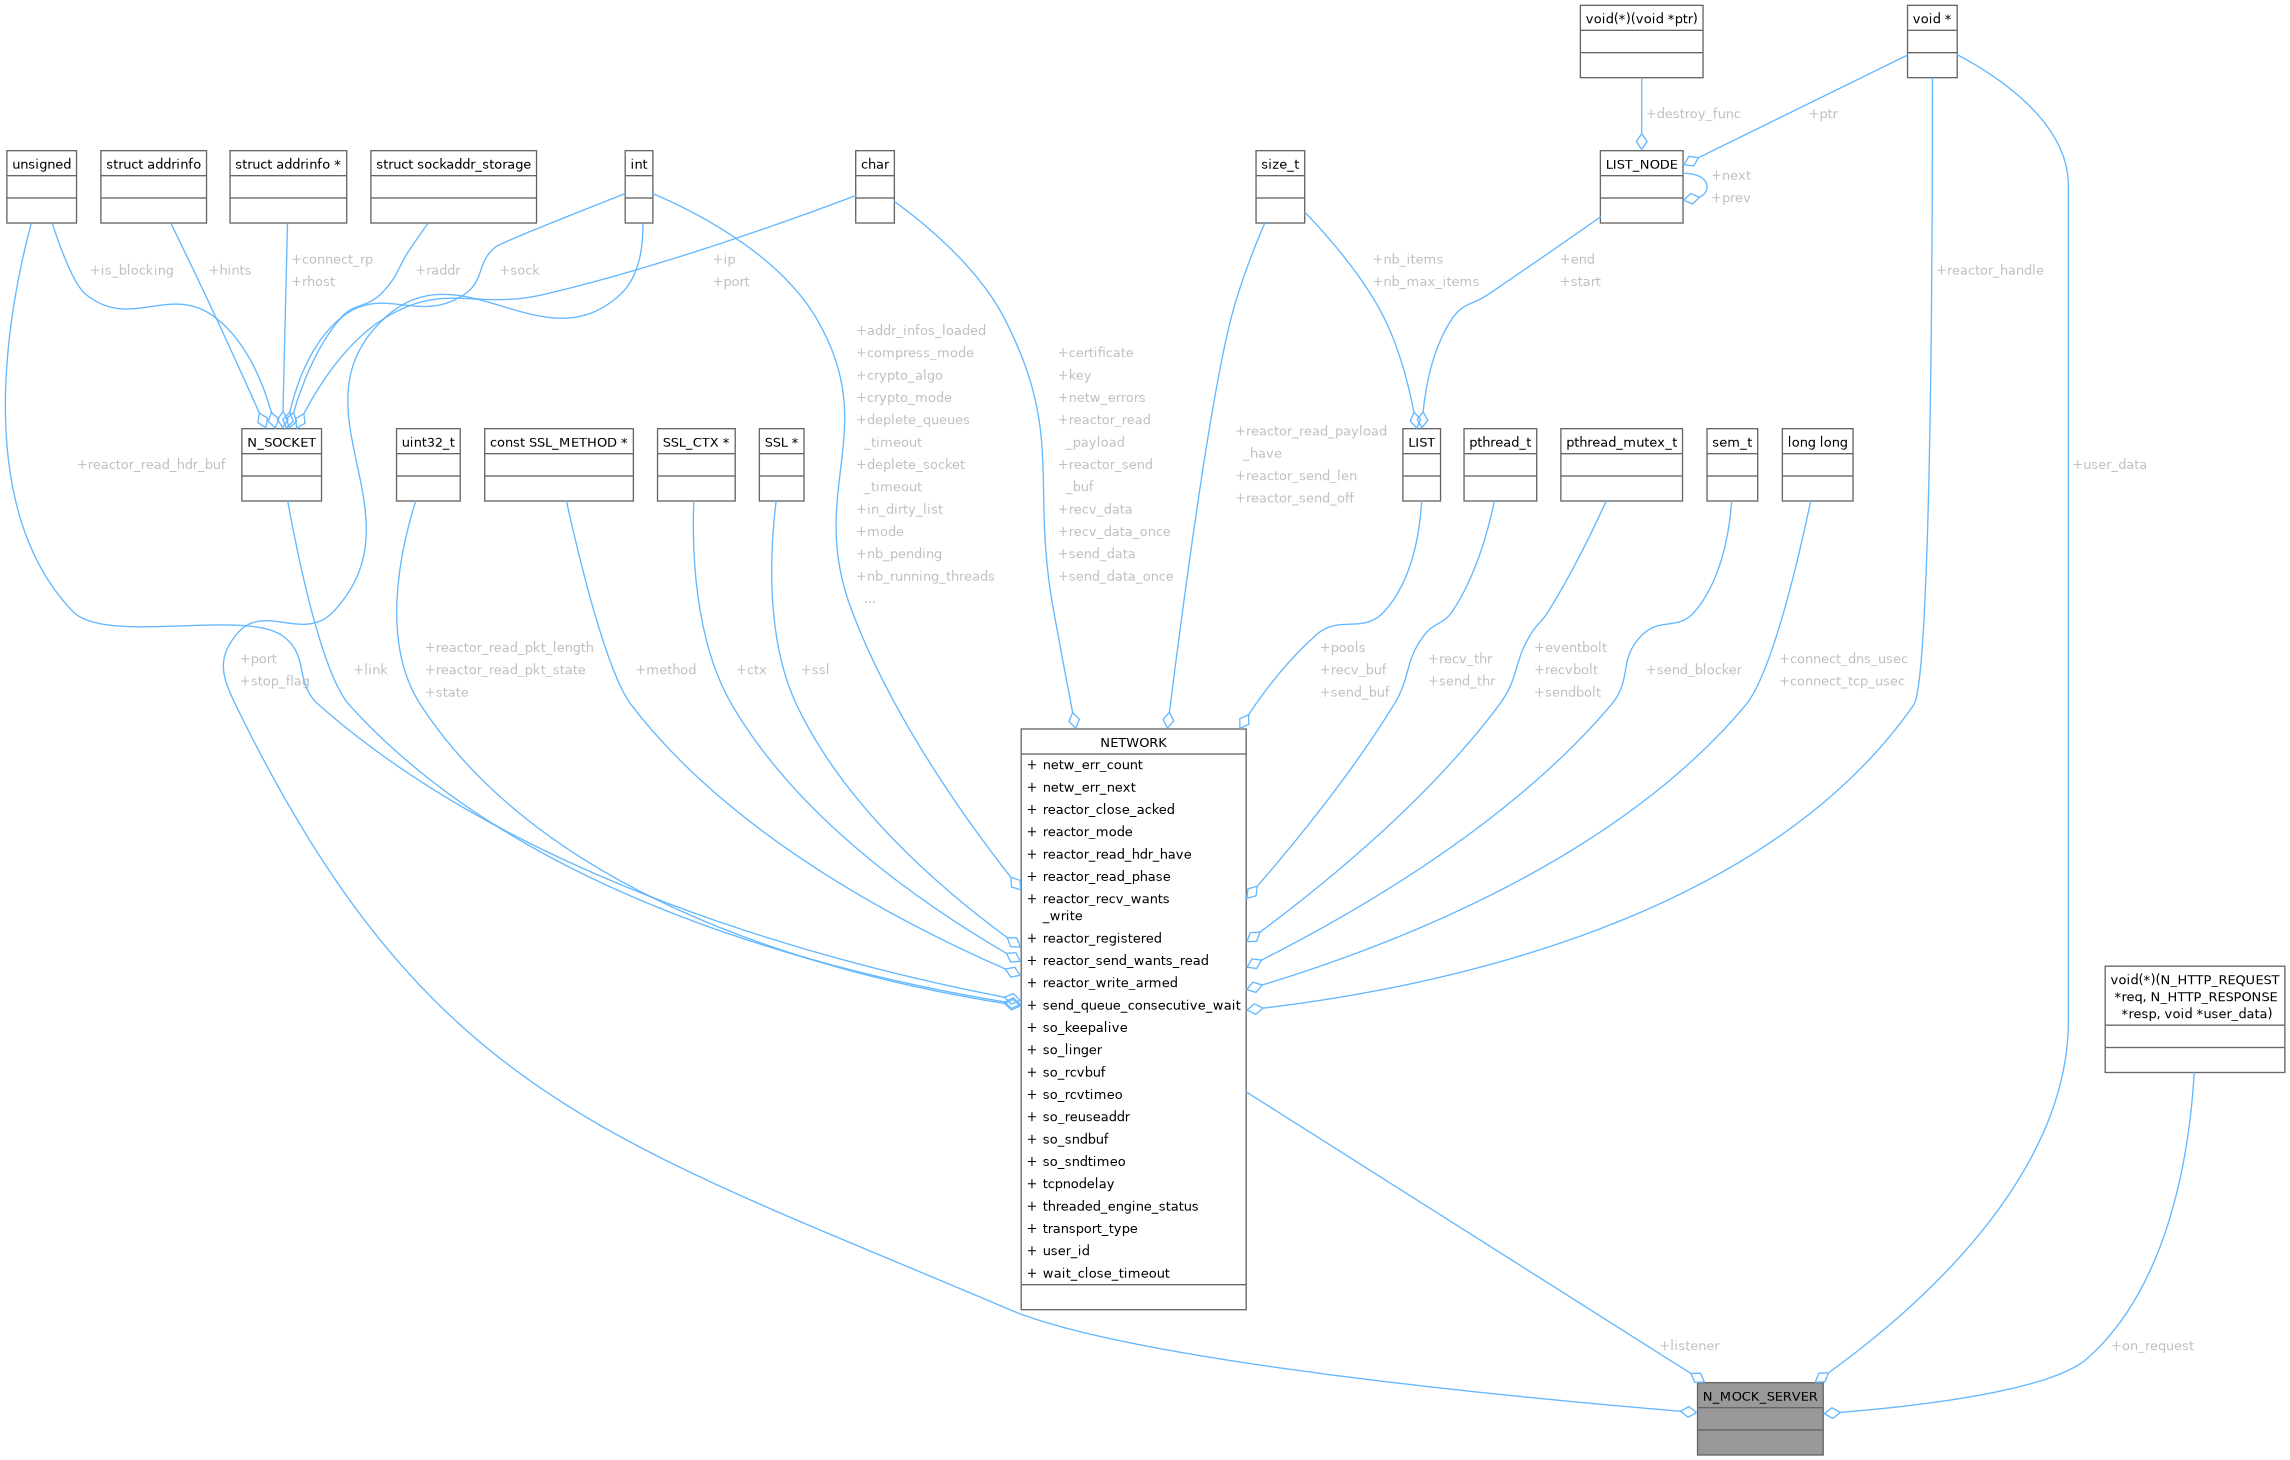
| struct N_MOCK_SERVER |
| Data Fields | ||
|---|---|---|
| NETWORK * | listener | listening network |
| void(*)(N_HTTP_REQUEST *req, N_HTTP_RESPONSE *resp, void *user_data) | on_request | request handler |
| int | port | listening port |
| volatile int | stop_flag | atomic stop flag |
| void * | user_data | user data for handler |
| struct N_PROXY_CFG |
Parsed proxy URL components.
Definition at line 932 of file n_network.h.
| Data Fields | ||
|---|---|---|
| char * | host | proxy hostname |
| char * | password | NULL if no auth. |
| int | port | proxy port |
| char * | scheme | "http", "https", or "socks5" |
| char * | username | NULL if no auth. |
| struct N_SOCKET |
Structure of a N_SOCKET.
Definition at line 352 of file n_network.h.
| Data Fields | ||
|---|---|---|
| struct addrinfo * | connect_rp | addrinfo currently being tried by a non-blocking connect (netw_connect_nonblock / netw_connect_check); NULL otherwise |
| struct addrinfo | hints | address of local machine |
| char * | ip | ip of the connected socket |
| unsigned long int | is_blocking | flag to quickly check socket mode |
| char * | port | port of socket |
| struct sockaddr_storage | raddr | connected remote addr |
| struct addrinfo * | rhost | getaddrinfo results |
| SOCKET | sock | a normal socket |
| struct N_SSE_CONN |
| Data Fields | ||
|---|---|---|
| NETWORK * | netw | underlying network connection |
| void(*)(N_SSE_EVENT *event, struct N_SSE_CONN *conn, void *user_data) | on_event | callback |
| volatile int | stop_flag | atomic stop flag |
| void * | user_data | user data for callback |
| struct N_SSE_EVENT |
SSE event received from server.
Definition at line 1127 of file n_network.h.
| Data Fields | ||
|---|---|---|
| N_STR * | data | event data |
| N_STR * | event | event type (or NULL for default) |
| N_STR * | id | last event ID (or NULL) |
| int | retry | retry interval in ms (0 if not set) |
| struct N_URL |
parsed URL components
Definition at line 1030 of file n_network.h.
| Data Fields | ||
|---|---|---|
| char * | host | hostname |
| int | nb_params | number of parsed parameters |
| N_URL_PARAM | params[64] | parsed key=value pairs |
| char * | path | path starting with "/", or "/" if empty |
| int | port | port number (0 if not specified) |
| char * | query |
raw query string without leading '? ', or NULL |
| char * | scheme | "http" or "https" |
| struct N_URL_PARAM |
a single query parameter key=value pair
Definition at line 1024 of file n_network.h.
| Data Fields | ||
|---|---|---|
| char * | key | parameter name |
| char * | value | parameter value |
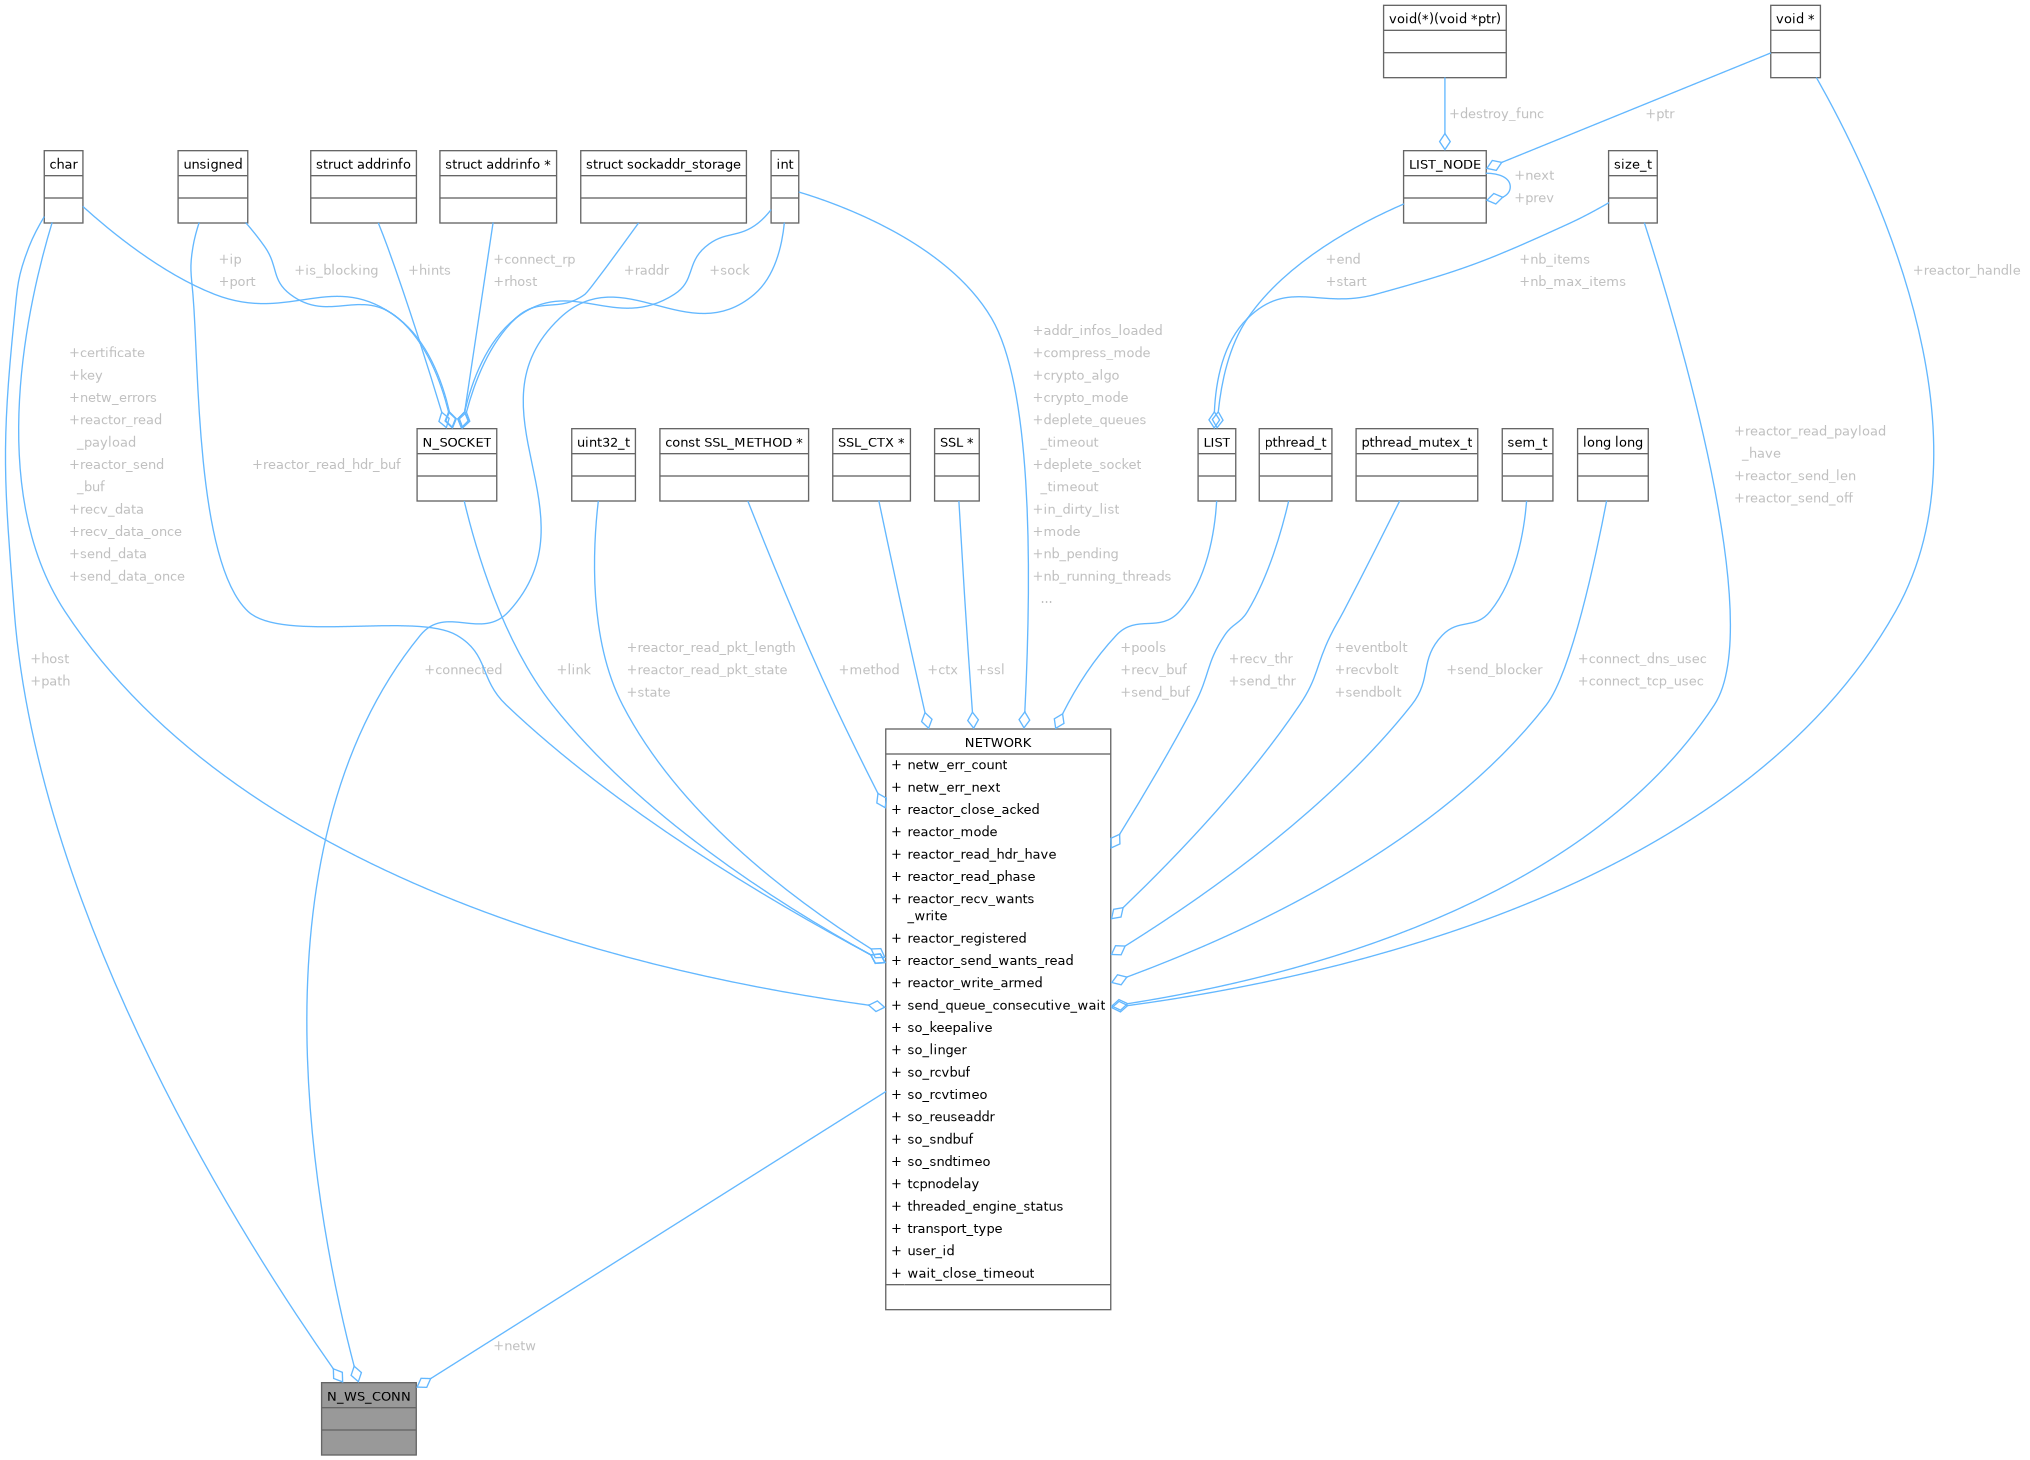
| struct N_WS_CONN |
WebSocket connection.
Definition at line 1078 of file n_network.h.
| Data Fields | ||
|---|---|---|
| int | connected | 1 if handshake completed |
| char * | host | remote hostname |
| NETWORK * | netw | underlying network connection |
| char * | path | resource path |
| struct N_WS_FRAME |
A single parsed WebSocket frame (RFC 6455).
payload points into the parsed buffer and is still masked when masked is set; use n_ws_unmask to decode it.
Definition at line 1087 of file n_network.h.
| struct N_WS_MESSAGE |
WebSocket message.
Definition at line 1071 of file n_network.h.
| Data Fields | ||
|---|---|---|
| int | masked | 1 if masked |
| int | opcode | frame opcode |
| N_STR * | payload | message payload |
| struct NETWORK |
Structure of a NETWORK.
Definition at line 375 of file n_network.h.
| Data Fields | ||
|---|---|---|
| int | addr_infos_loaded | Internal flag to know if we have to free addr infos. |
| char * | certificate | openssl certificate file |
| int | compress_mode |
Per-packet compression mode, see NETW_COMPRESS_MODE. Set via netw_set_compression_mode(); default is NETW_COMPRESS_ZLIB to preserve the behaviour from when a single unconditional compression path was the only option. Any NETW_COMPRESSED_* flag on the wire is honoured on recv regardless of this field, so two peers with different send-side picks still interop. |
| long long | connect_dns_usec |
Measured DNS resolution time of the most recent connect, in microseconds (0 if not measured). Populated by netw_connect_ex_to so callers can report a connect-phase timing breakdown. |
| long long | connect_tcp_usec |
Measured TCP connect time of the most recent connect, in microseconds (0 if not measured). Populated by netw_connect_ex_to. |
| int | crypto_algo | if encryption is on, which one (flags NETW_ENCRYPT_*) |
| int | crypto_mode | tell if the socket have to be encrypted (flags NETW_CRYPTO_*) |
| SSL_CTX * | ctx | SSL context holder. |
| int | deplete_queues_timeout | deplete network queues timeout ( 0 disabled, > 0 wait for timeout and check unset/unack datas) |
| int | deplete_socket_timeout | deplete socket send buffer timeout ( 0 disabled, > 0 wait for timeout and check unset/unack datas) |
| pthread_mutex_t | eventbolt | mutex for threaded access of state event |
| int | in_dirty_list |
Dirty-list membership flag. CAS-guards a NETWORK's membership in the reactor's dirty_pending list. Producer side (n_reactor_notify_send) attempts a 0-to-1 CAS; on success it pushes the NETWORK onto the dirty list and writes the wake-eventfd. Consumer side (n_reactor_run wake handler) clears the flag BEFORE draining so a concurrent producer can immediately re-add the NETWORK for the next pass: no message can be lost. |
| char * | key | openssl key file |
| N_SOCKET | link | networking socket |
| const SSL_METHOD * | method | SSL method container. |
| int | mode | NETWORK mode , 1 listening, 0 connecting. |
| int | nb_pending | Nb pending connection,if listening. |
| int | nb_running_threads | nb running threads, if > 0 thread engine is still running |
| int | netw_err_count | number of captured errors |
| int | netw_err_next | next write slot in ring buffer |
| char | netw_errors[8][512] | per-connection error capture ring buffer (max 8 entries, 512 chars each) |
| LIST * | pools | pointers to network pools if members of any |
| int | reactor_close_acked |
Close handshake. Game thread sets NETW_EXIT_ASKED, notifies the reactor, and waits on this flag. n_reactor_unregister publishes it with a release store as its final action, so EVERY unregister path (the EXIT_ASKED sweep, a peer EOF / EPOLLRDHUP, or a hard I/O error) releases the waiter, not just the sweep. The acquire-load on the game side observes, and is ordered after, every side effect of unregister (epoll DEL, cleared reactor_mode, freed accumulators, list removal) before it closes the socket / frees the NETWORK. Reset to 0 in n_reactor_register. Always accessed via __atomic builtins (release on the reactor side, acquire on the game side); plain volatile would give no happens-before and is a data race. |
| void * | reactor_handle |
Back-pointer to the registered reactor. Opaque void * so n_network.h doesn't need to include n_reactor.h (avoids a header-ordering dependency since n_reactor.h includes n_network.h itself). NULL when reactor_mode == 0. Same atomicity contract as reactor_mode: use netw_atomic_read_reactor_handle / netw_atomic_write_reactor_handle. |
| int | reactor_mode |
Opt-in epoll-reactor mode flag. 0 (default) = classic per-connection thread engine; 1 = registered with an n_reactor. Atomically set by n_reactor_register, cleared by n_reactor_unregister. Read concurrently from the game thread (e.g. netw_close, netw_add_msg), always access via netw_atomic_read_reactor_mode / netw_atomic_write_reactor_mode so the read/clear race during peer-driven unregister is well-defined under TSan. Always 0 on platforms where N_REACTOR_AVAILABLE == 0. |
| unsigned char | reactor_read_hdr_buf[4] | accumulator for header words |
| int | reactor_read_hdr_have | bytes accumulated in reactor_read_hdr_buf |
| char * | reactor_read_payload | malloc'd accumulator for payload bytes |
| size_t | reactor_read_payload_have | bytes accumulated into reactor_read_payload |
| int | reactor_read_phase | 0=STATE, 1=LENGTH, 2=PAYLOAD |
| uint32_t | reactor_read_pkt_length | payload length for the in-flight frame |
| uint32_t | reactor_read_pkt_state | state word for the in-flight frame |
| int | reactor_recv_wants_write |
TLS-over-reactor: recv returned NETW_IO_WANT_WRITE, the reactor re-runs the readable drain after the next writable event. Always 0 on cleartext sockets. |
| int | reactor_registered |
Reactor close-handshake latch. Set to 1 by n_reactor_register and never cleared by the reactor (unlike reactor_mode, which the reactor clears mid-unregister). netw_close keys its decision to run n_reactor_close_netw_sync on THIS flag rather than on the live reactor_mode: otherwise, if the reactor clears reactor_mode during a peer-EOF unregister in the instant before netw_close reads it, the game thread would skip the ack-wait and free the NETWORK while the reactor is still inside n_reactor_unregister (a use-after-free / data race). With the latch the game thread always waits for reactor_close_acked, which the reactor publishes as the last thing it ever does with the NETWORK. Acquire/release __atomic access, same contract as the other reactor flags. |
| char * | reactor_send_buf | malloc'd framed bytes, NULL when idle |
| size_t | reactor_send_len | total bytes in reactor_send_buf |
| size_t | reactor_send_off | bytes already sent to socket |
| int | reactor_send_wants_read |
TLS-over-reactor: the in-flight send returned NETW_IO_WANT_READ (renegotiation), the reactor retries the write drain after the next readable event instead of waiting on EPOLLOUT. Always 0 on cleartext sockets. |
| int | reactor_write_armed | 1 = EPOLLOUT currently registered |
| LIST * | recv_buf | reveicing buffer (for incomming usage) |
| netw_func | recv_data | receive func ptr |
| netw_func | recv_data_once | single-attempt recv, same contract as send_data_once. |
| pthread_t | recv_thr | receiving thread |
| pthread_mutex_t | recvbolt | mutex for threaded access of recv buf |
| sem_t | send_blocker | block sending func |
| LIST * | send_buf | sending buffer (for outgoing queuing ) |
| netw_func | send_data | send func ptr |
| netw_func | send_data_once |
single-attempt send (non-blocking / reactor use). Contract: one transport attempt; > 0 bytes written, NETW_IO_WANT_READ / NETW_IO_WANT_WRITE when the transport needs that readiness to progress, NETW_SOCKET_DISCONNECTED, or NETW_SOCKET_ERROR. Dispatches to the TLS variant when crypto is set, this is what lets the epoll reactor carry TLS connections. |
| int | send_queue_consecutive_wait | send queue consecutive pool interval, used when there are still items to send, in usec |
| pthread_t | send_thr | sending thread |
| pthread_mutex_t | sendbolt | mutex for threaded access of send_buf |
| int | so_keepalive | so keepalive state |
| int | so_linger | close lingering value (-1 disabled, 0 force close, >0 linger ) |
| int | so_rcvbuf | size of the socket recv buffer, 0 untouched, else size in bytes |
| int | so_rcvtimeo | send timeout value |
| int | so_reuseaddr | so reuseaddr state |
| int | so_sndbuf | size of the socket send buffer, 0 untouched, else size in bytes |
| int | so_sndtimeo | send timeout value |
| SSL * | ssl | SSL handle. |
| uint32_t | state | state of the connection , NETW_RUN, NETW_QUIT, NETW_STOP , NETW_ERR |
| int | tcpnodelay | state of naggle algorythm, 0 untouched, 1 forcibly disabled |
| int | threaded_engine_status |
Threaded network engine state for this network. NETW_THR_ENGINE_STARTED or NETW_THR_ENGINE_STOPPED |
| int | transport_type | transport type: NETWORK_TCP (0) or NETWORK_UDP (1) |
| int | user_id | if part of a user property, id of the user |
| int | wait_close_timeout | network wait close timeout value ( < 1 disabled, >= 1 timeout sec ) |
| struct NETWORK_HTTP_INFO |
structure for splitting HTTP requests
Definition at line 635 of file n_network.h.
| Data Fields | ||
|---|---|---|
| char * | body | Pointer to the body data. |
| size_t | content_length | Store content length. |
| char | content_type[256] | Store content type. |
| char * | type | Type of request. |
| struct NETWORK_POOL |
| Data Fields | ||
|---|---|---|
| HASH_TABLE * | pool | table of clients |
| pthread_rwlock_t | rwlock | thread safety |
| #define _OPEN_SYS_SOCK_IPV6 1 |
Definition at line 235 of file n_network.h.
| #define HEAD_CODE 3 |
Code of a HEAD message.
Definition at line 68 of file n_network.h.
Referenced by recv_php(), and send_php().
| #define HEAD_SIZE 10 |
Size of a HEAD message.
Definition at line 66 of file n_network.h.
Referenced by recv_php(), and send_php().
| #define N_ENUM_netw_code_type | ( | _ | ) |
Network codes definition.
Definition at line 296 of file n_network.h.
| #define N_URL_MAX_PARAMS 64 |
maximum number of parsed query parameters
Definition at line 1021 of file n_network.h.
Referenced by _n_parse_query_params().
| #define N_WS_MAX_PAYLOAD (64 * 1024 * 1024) |
Largest WebSocket payload n_ws_recv() will accept from a peer, in bytes.
A frame header declares its payload length in up to 64 bits, so an unvalidated length both invites a peer to ask for an unbounded allocation and, near SIZE_MAX, makes the terminator arithmetic wrap. Anything larger is rejected as a protocol error.
Definition at line 1068 of file n_network.h.
Referenced by main(), and n_ws_recv().
| #define N_WS_OP_BINARY 0x02 |
Definition at line 1059 of file n_network.h.
Referenced by test_frame_codec().
| #define N_WS_OP_CLOSE 0x08 |
Definition at line 1060 of file n_network.h.
Referenced by n_ws_close().
| #define N_WS_OP_PING 0x09 |
Definition at line 1061 of file n_network.h.
Referenced by test_frame_codec().
| #define N_WS_OP_PONG 0x0A |
Definition at line 1062 of file n_network.h.
| #define N_WS_OP_TEXT 0x01 |
WebSocket opcodes per RFC 6455.
Definition at line 1058 of file n_network.h.
Referenced by main(), and test_frame_codec().
| #define netw_atomic_read_reactor_handle | ( | netw | ) |
Same contract for the back-pointer to the reactor.
NULL after unregister. Reads in netw_add_msg / n_reactor_close_netw_sync pair with the write inside n_reactor_unregister.
Definition at line 621 of file n_network.h.
Referenced by netw_add_msg().
| #define netw_atomic_read_reactor_mode | ( | netw | ) |
Lock-free atomic read of the reactor_mode flag.
The reactor thread clears this flag inside n_reactor_unregister (peer EOF, EXIT_ASKED sweep, or game-thread close handshake), while the game thread reads it from netw_close and netw_add_msg to decide which dispatch path to take. Both outcomes are correct (the close handshake is designed to be idempotent), but TSan still requires synchronised access to the read/write pair.
Definition at line 616 of file n_network.h.
Referenced by netw_add_msg().
| #define netw_atomic_read_state | ( | netw | ) |
Lock-free atomic read of the network state field.
Uses GCC __atomic builtins (supported on Linux gcc, Solaris gcc, Windows mingw gcc). Provides acquire semantics so subsequent reads see up-to-date values. For use in send/recv thread hot loops to avoid mutex overhead.
Definition at line 602 of file n_network.h.
Referenced by netw_get_state(), netw_recv_func(), and netw_send_func().
| #define netw_atomic_write_reactor_handle | ( | netw, | |
| val ) |
Definition at line 622 of file n_network.h.
| #define netw_atomic_write_reactor_mode | ( | netw, | |
| val ) |
Definition at line 617 of file n_network.h.
| #define netw_atomic_write_state | ( | netw, | |
| val ) |
Lock-free atomic write of the network state field.
Uses GCC __atomic builtins with release semantics so prior writes are visible to threads performing an acquire load.
Definition at line 607 of file n_network.h.
Referenced by netw_new(), and netw_set().
| #define NETW_COMPRESS_MIN_RATIO 10u |
Definition at line 343 of file n_network.h.
Referenced by netw_send_func().
| #define NETW_COMPRESS_THRESHOLD 256u |
Opportunistic compression policy.
Outbound payloads shorter than NETW_COMPRESS_THRESHOLD bytes skip the codec entirely; longer payloads are compressed only if the result is at least NETW_COMPRESS_MIN_RATIO percent smaller than the original (otherwise the original is shipped uncompressed). The reactor's send path (n_reactor_drain_writes) shares these knobs with the thread engine's netw_send_func.
Definition at line 342 of file n_network.h.
Referenced by netw_send_func().
| #define NETW_COMPRESSED NETW_COMPRESSED_ZLIB |
Legacy alias, the first compression commit shipped a single NETW_COMPRESSED flag before LZ4 was added.
Keep the name for any downstream consumer that referenced it before this split.
Definition at line 318 of file n_network.h.
| #define NETW_HAVE_TLS13 N_OSSL_HAVE_TLS13 |
1 when the linked TLS library can negotiate TLS 1.3, 0 otherwise.
TLS 1.3 (and with it TLS1_3_VERSION and the SSL_CTX_set_ciphersuites() knob) arrived in OpenSSL 1.1.1 and LibreSSL 3.5; the OpenSSL 1.0.2 this library still supports tops out at TLS 1.2. The test is N_OSSL_HAVE_TLS13 rather than a bare OPENSSL_VERSION_NUMBER comparison because that number is a fixed compatibility value under LibreSSL, see n_openssl_compat.h.
Definition at line 257 of file n_network.h.
| #define NETW_IO_WANT_READ -10 |
single-attempt I/O (send_data_once / recv_data_once): the operation cannot progress until the socket is READABLE.
Raw recv maps EAGAIN here; TLS maps SSL_ERROR_WANT_READ, note a TLS send can also return this mid-renegotiation.
Definition at line 77 of file n_network.h.
Referenced by _netw_ssl_handshake_step(), drive_handshake(), io_full(), main(), recv_data_once(), recv_ssl_data_once(), and send_ssl_data_once().
| #define NETW_IO_WANT_WRITE -11 |
single-attempt I/O: the operation cannot progress until the socket is WRITABLE.
Raw send maps EAGAIN here; TLS maps SSL_ERROR_WANT_WRITE, a TLS recv can also return this.
Definition at line 81 of file n_network.h.
Referenced by _netw_ssl_handshake_step(), drive_connect(), drive_handshake(), io_full(), netw_connect_check(), recv_ssl_data_once(), send_data_once(), and send_ssl_data_once().
| #define NETW_MAX_RETRIES 8 |
Send or recv max number of retries.
Definition at line 83 of file n_network.h.
Referenced by recv_data(), and send_data().
| #define NETW_MSG_MAX_FRAME_SIZE (1024UL * 1024UL * 1024UL) |
Maximum accepted size, in bytes, of a single received message frame payload.
The on-wire length prefix is an untrusted 32-bit value; any frame claiming more than this is rejected before allocation. This both bounds a hostile peer's memory demand and keeps length + 1 from wrapping a uint32_t. Override at build time if a legitimate deployment needs larger frames. Default: 1 GiB.
Definition at line 93 of file n_network.h.
Referenced by netw_recv_func().
| #define NETW_RETRY_DELAY 1000 |
Send or recv delay between retries in usec.
Definition at line 85 of file n_network.h.
| #define NETW_SOCKET_DISCONNECTED -2 |
Code for a disconnected recv.
Definition at line 72 of file n_network.h.
Referenced by netw_recv_func(), netw_send_func(), recv_data(), recv_data_once(), recv_ssl_data(), recv_ssl_data_once(), send_data(), send_data_once(), send_ssl_data(), send_ssl_data_once(), and send_udp_data().
| #define NETW_SOCKET_ERROR -1 |
code for a socket error
Definition at line 70 of file n_network.h.
Referenced by netw_udp_recvfrom(), netw_udp_sendto(), recv_data(), recv_data_once(), recv_ssl_data(), recv_ssl_data_once(), recv_udp_data(), send_data(), send_data_once(), send_ssl_data(), send_ssl_data_once(), and send_udp_data().
| #define NETW_THR_EXIT_ERROR 666 |
Internal DONE value indicating a send/recv thread observed NETW_ERROR without an in-flight local shutdown.
Definition at line 98 of file n_network.h.
Referenced by netw_recv_func(), and netw_send_func().
| #define NETW_THR_EXIT_OK 100 |
Internal DONE value indicating a send/recv thread reached end-of-life cleanly (peer QUIT or local NETW_EXIT_ASKED ack'd).
Definition at line 96 of file n_network.h.
Referenced by netw_recv_func(), and netw_send_func().
| #define NETW_TLS_MAX_VERSION TLS1_2_VERSION |
highest TLS version the linked TLS library can negotiate, as a TLS*_VERSION constant.
Use it instead of naming TLS1_3_VERSION directly: that constant does not exist below OpenSSL 1.1.1 / LibreSSL 3.5, so a literal mention does not compile there.
Definition at line 266 of file n_network.h.
Referenced by main(), and make_server_ctx().
| #define NETWORK_CONSECUTIVE_SEND_WAIT 2048 |
Flag to set consecutive send waiting timeout.
Definition at line 62 of file n_network.h.
Referenced by netw_setsockopt().
| #define NETWORK_DEPLETE_QUEUES_TIMEOUT 1024 |
Flag to set network queues depletion timeout.
Definition at line 60 of file n_network.h.
Referenced by netw_setsockopt().
| #define NETWORK_DEPLETE_SOCKET_TIMEOUT 512 |
Flag to set send buffer depletion timeout.
Definition at line 58 of file n_network.h.
Referenced by netw_setsockopt().
| #define NETWORK_DISABLE_ZERO_LENGTH_RECV FALSE |
Enable/disable recv of length 0.
Warning: only enable if you know what you are doing ! (TRUE or FALSE)
Definition at line 46 of file n_network.h.
| #define NETWORK_IPALL 0 |
Flag for auto detection by OS of ip version to use.
Definition at line 48 of file n_network.h.
Referenced by bind_free(), bind_free(), bind_free(), cl_connect(), client_connect(), client_worker_echo(), client_worker_fast(), main(), n_http_server_new(), n_mock_server_start(), n_sse_connect(), n_ws_connect(), run_client(), run_client(), run_server(), and run_server().
| #define NETWORK_IPV4 1 |
Flag to force IPV4.
Definition at line 50 of file n_network.h.
Referenced by check_exclusive(), check_refused(), main(), netw_bind_udp(), netw_connect_ex_to(), netw_connect_nonblock(), netw_connect_udp(), netw_make_listening(), process_args(), process_args(), server_thread(), and try_connect().
| #define NETWORK_IPV6 2 |
Flag to force IPV6.
Definition at line 52 of file n_network.h.
Referenced by netw_bind_udp(), netw_connect_ex_to(), netw_connect_nonblock(), netw_connect_udp(), netw_make_listening(), process_args(), and process_args().
| #define NETWORK_TCP 0 |
Flag for TCP transport (default).
Definition at line 54 of file n_network.h.
Referenced by netw_new().
| #define NETWORK_UDP 1 |
Flag for UDP transport.
Definition at line 56 of file n_network.h.
Referenced by netw_bind_udp(), and netw_connect_udp().
| #define NETWORK_WAIT_CLOSE_TIMEOUT 4096 |
Flag to set network closing wait timeout.
Definition at line 64 of file n_network.h.
Referenced by main(), and netw_setsockopt().
| #define SOCKET_SIZE_FORMAT "%d" |
socket associated printf style
Definition at line 113 of file n_network.h.
Referenced by handle_request(), netw_accept_from_ex(), netw_close(), netw_connect_check(), netw_pool_add(), netw_pool_netw_close(), netw_pool_remove(), netw_recv_func(), netw_send_func(), netw_setsockopt(), netw_stop_thr_engine(), netw_udp_recvfrom(), netw_udp_sendto(), netw_wait_msg(), recv_data(), recv_data_once(), recv_php(), recv_udp_data(), send_data(), send_data_once(), send_php(), and send_udp_data().
| #define SSL_get1_peer_certificate | ( | ssl | ) |
Definition at line 247 of file n_network.h.
Referenced by main(), and netw_ssl_get_verify_result().
| typedef ssize_t(* netw_func) (void *, char *, uint32_t) |
send/recv func ptr type
Definition at line 349 of file n_network.h.
| typedef int(* netw_sni_pick_cb) (const char *sni, N_STR **cert_pem, N_STR **key_pem, void *user_data) |
SNI cert-pick callback for netw_accept_ssl_with_sni_cb: given the client SNI host (may be NULL), fill *cert_pem and *key_pem with a server certificate and key (newly allocated; n_network frees them).
Return 0 to proceed with the handshake, non-zero to fail it.
Definition at line 683 of file n_network.h.
| typedef int SOCKET |
default socket declaration
socket type for POSIX systems
Definition at line 111 of file n_network.h.
| enum __netw_code_type |
Network codes declaration.
Definition at line 346 of file n_network.h.
| enum NETW_COMPRESS_MODE |
Compression mode selector for NETWORK.compress_mode.
The per-packet state word on the wire carries NETW_COMPRESSED_ZLIB or NETW_COMPRESSED_LZ4 so a receiver in NETW_COMPRESS_AUTO (the default) can decode whichever algorithm the sender chose, while a receiver pinned to a specific algorithm will decode only that flag and pass anything else through uncompressed.
Definition at line 326 of file n_network.h.
| int deplete_send_buffer | ( | int | fd, |
| int | timeout ) |
wait for send buffer to be empty
wait for send buffer to be empty
Not as reliable as expected.
| fd | socket descriptor |
| timeout | timeout value in msec , value <= 0 : disabled |
Definition at line 3336 of file n_network.c.
References LOG_ERR, and n_log.
Referenced by netw_close().
| size_t htonst | ( | size_t | value | ) |
host to network size_t
| value | the size_t value to convert to network order |
Definition at line 145 of file n_network.c.
References htonst().
Referenced by htonst().
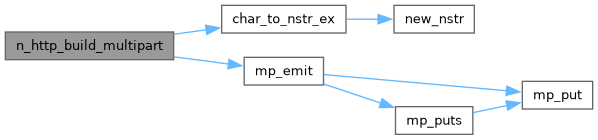
build a multipart/form-data body from a LIST of N_HTTP_MULTIPART_PART* using boundary (without "--"); returns a new N_STR (free with free_nstr) or NULL.
Definition at line 6836 of file n_network.c.
References char_to_nstr_ex(), Malloc, and mp_emit().
Referenced by main().
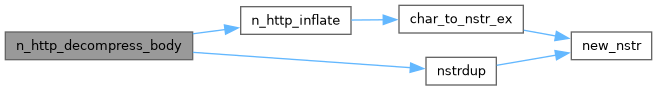
decompress an HTTP body per its Content-Encoding ("gzip"/"deflate"; identity/NULL/unknown copies through).
Sets *out to a new N_STR (free with free_nstr). Returns 0 on success, -1 on error.
Definition at line 6535 of file n_network.c.
References N_STR::data, n_http_inflate(), nstrdup(), and N_STR::written.
Referenced by main().
| int n_http_multipart_boundary | ( | const char * | content_type, |
| char * | out, | ||
| size_t | outsz ) |
copy the boundary token from a Content-Type value into out (without the leading "--").
Returns 0 on success, -1 when absent.
Definition at line 6595 of file n_network.c.
Referenced by main().
| void n_http_multipart_free | ( | LIST ** | parts | ) |
free a LIST returned by n_http_parse_multipart and NULL the pointer
Definition at line 6635 of file n_network.c.
References list_destroy().
Referenced by main().
parse a multipart body (boundary given without "--") into a LIST of N_HTTP_MULTIPART_PART*; free with n_http_multipart_free.
Returns NULL on a bad argument.
Definition at line 6695 of file n_network.c.
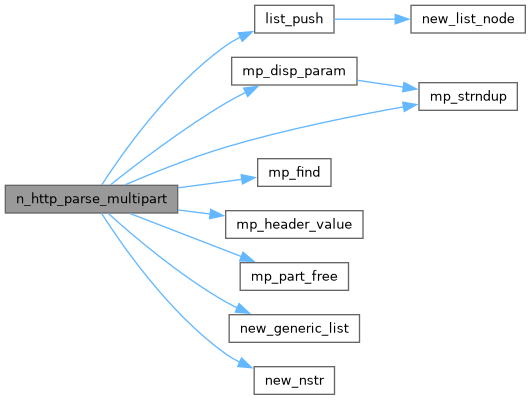
References N_HTTP_MULTIPART_PART::body, N_HTTP_MULTIPART_PART::content_type, N_STR::data, N_HTTP_MULTIPART_PART::filename, list_push(), Malloc, mp_disp_param(), mp_find(), mp_header_value(), mp_part_free(), mp_strndup(), N_HTTP_MULTIPART_PART::name, new_generic_list(), new_nstr(), and N_STR::written.
Referenced by main().
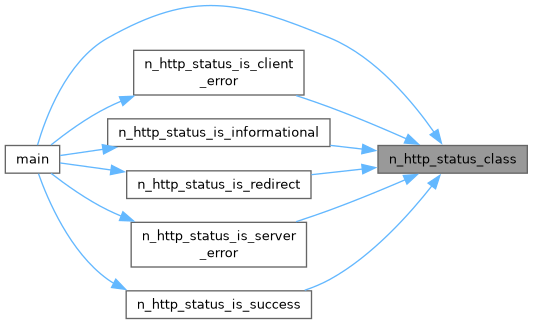
| int n_http_status_class | ( | int | status_code | ) |
leading digit of an HTTP status code (1..5), or 0 when outside 100..599
Definition at line 6452 of file n_network.c.
Referenced by main(), n_http_status_is_client_error(), n_http_status_is_informational(), n_http_status_is_redirect(), n_http_status_is_server_error(), and n_http_status_is_success().
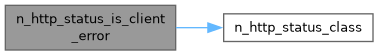
| int n_http_status_is_client_error | ( | int | status_code | ) |
1 when status_code is a client error (4xx), else 0
Definition at line 6470 of file n_network.c.
References n_http_status_class().
Referenced by main().
| int n_http_status_is_informational | ( | int | status_code | ) |
1 when status_code is informational (1xx), else 0
Definition at line 6458 of file n_network.c.
References n_http_status_class().
Referenced by main().
| int n_http_status_is_redirect | ( | int | status_code | ) |
1 when status_code is a redirect (3xx), else 0
Definition at line 6466 of file n_network.c.
References n_http_status_class().
Referenced by main().
| int n_http_status_is_server_error | ( | int | status_code | ) |
1 when status_code is a server error (5xx), else 0
Definition at line 6474 of file n_network.c.
References n_http_status_class().
Referenced by main().
| int n_http_status_is_success | ( | int | status_code | ) |
1 when status_code is success (2xx), else 0
Definition at line 6462 of file n_network.c.
References n_http_status_class().
Referenced by main().
| void n_mock_server_free | ( | N_MOCK_SERVER ** | server | ) |
free a mock server and close the listening socket
free a mock server and close the listening socket
| server | pointer to pointer, set to NULL |
Definition at line 8021 of file n_network.c.
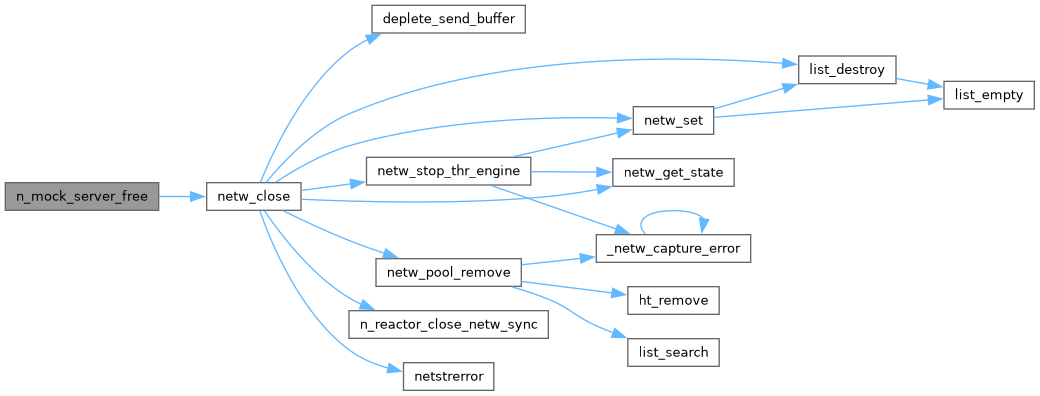
References __n_assert, FreeNoLog, netw_close(), and server.
Referenced by main().
| void n_mock_server_run | ( | N_MOCK_SERVER * | server | ) |
run the mock server accept loop (blocks until stop_flag is set)
run the mock server accept loop (blocks until stop_flag is set)
Blocks until stop_flag is set.
| server | mock server handle |
Definition at line 7927 of file n_network.c.
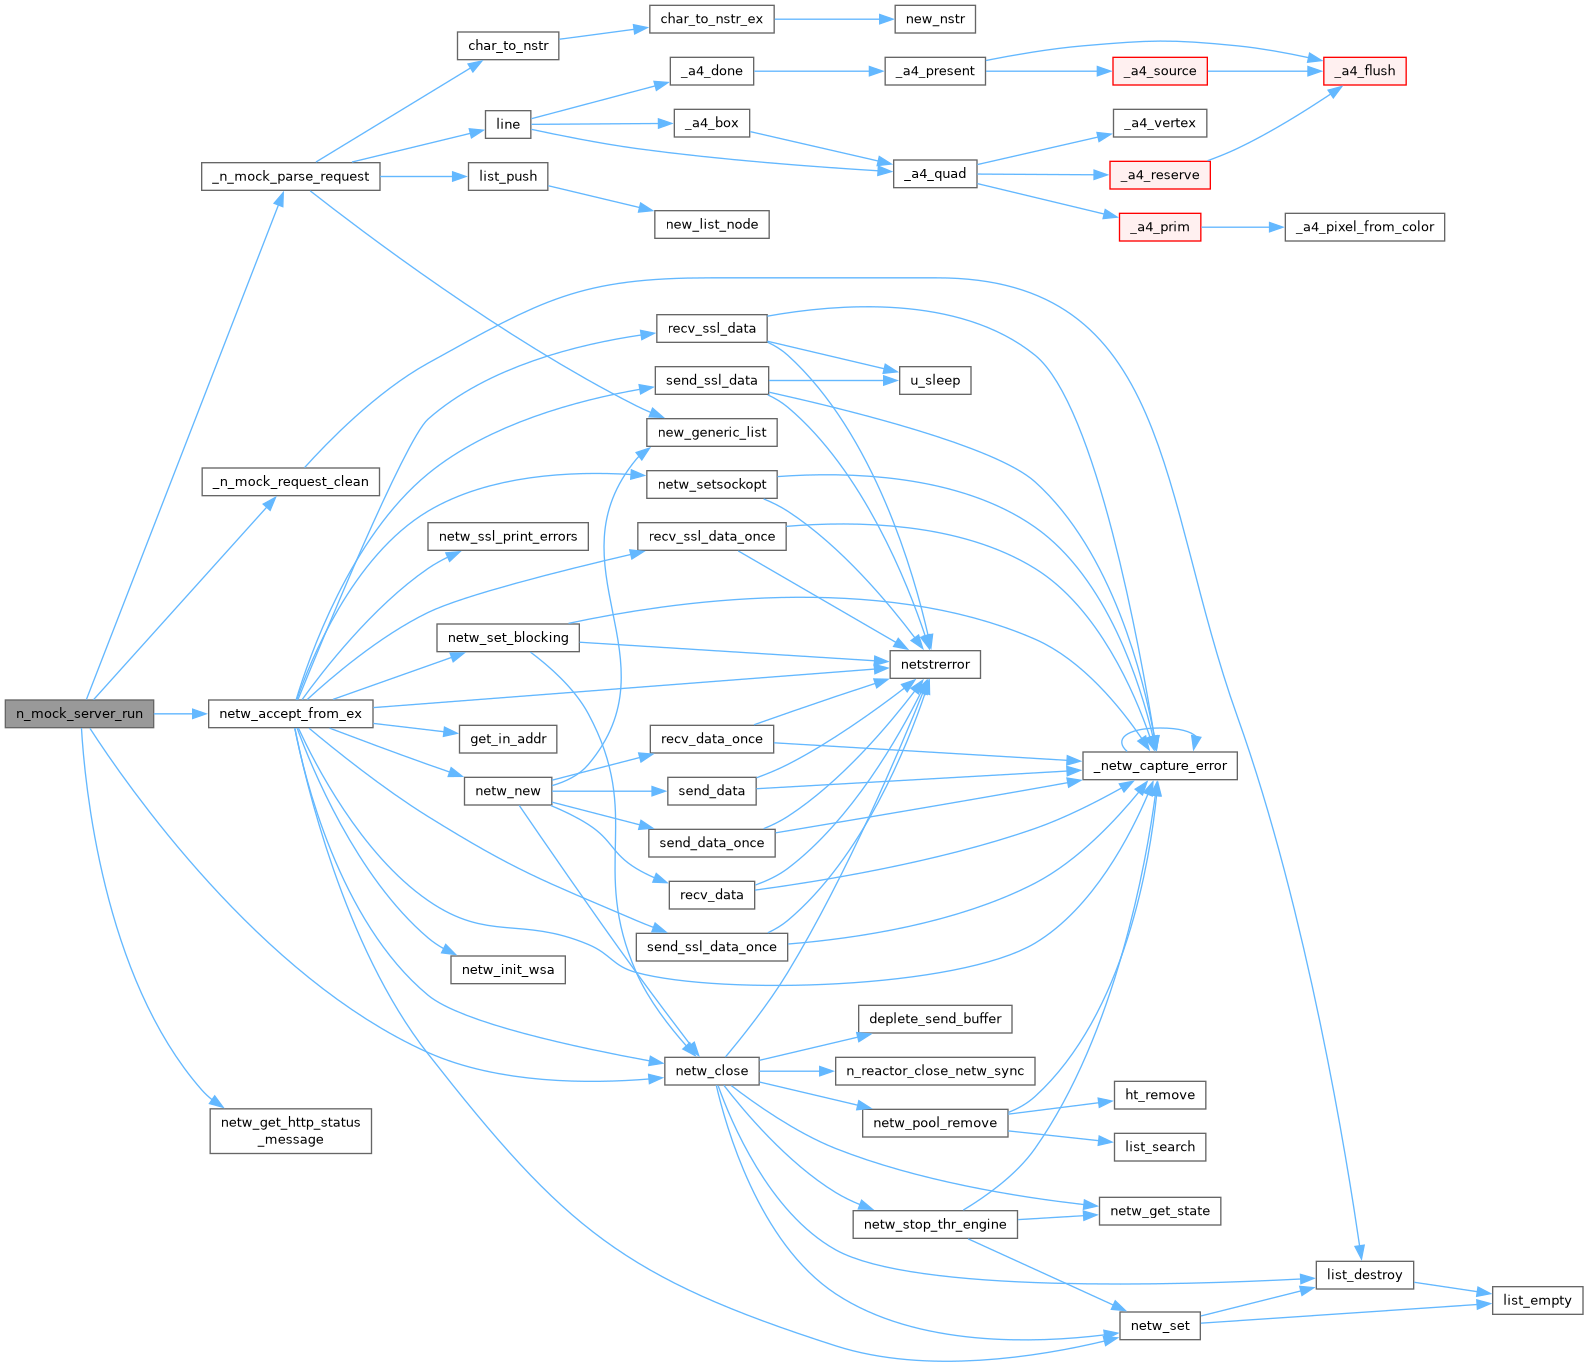
References __n_assert, _n_mock_parse_request(), _n_mock_request_clean(), N_HTTP_RESPONSE::body, N_HTTP_RESPONSE::content_type, N_STR::data, free_nstr, LOG_INFO, n_log, netw_accept_from_ex(), netw_close(), netw_get_http_status_message(), server, N_HTTP_RESPONSE::status_code, and N_STR::written.
Referenced by server_thread().
| N_MOCK_SERVER * n_mock_server_start | ( | int | port, |
| void(* | on_request )(N_HTTP_REQUEST *, N_HTTP_RESPONSE *, void *), | ||
| void * | user_data ) |
start a mock HTTP server on localhost:port (returns immediately)
start a mock HTTP server on localhost:port (returns immediately)
| port | port number to listen on |
| on_request | callback for each received HTTP request |
| user_data | arbitrary pointer passed to callback |
Definition at line 7893 of file n_network.c.
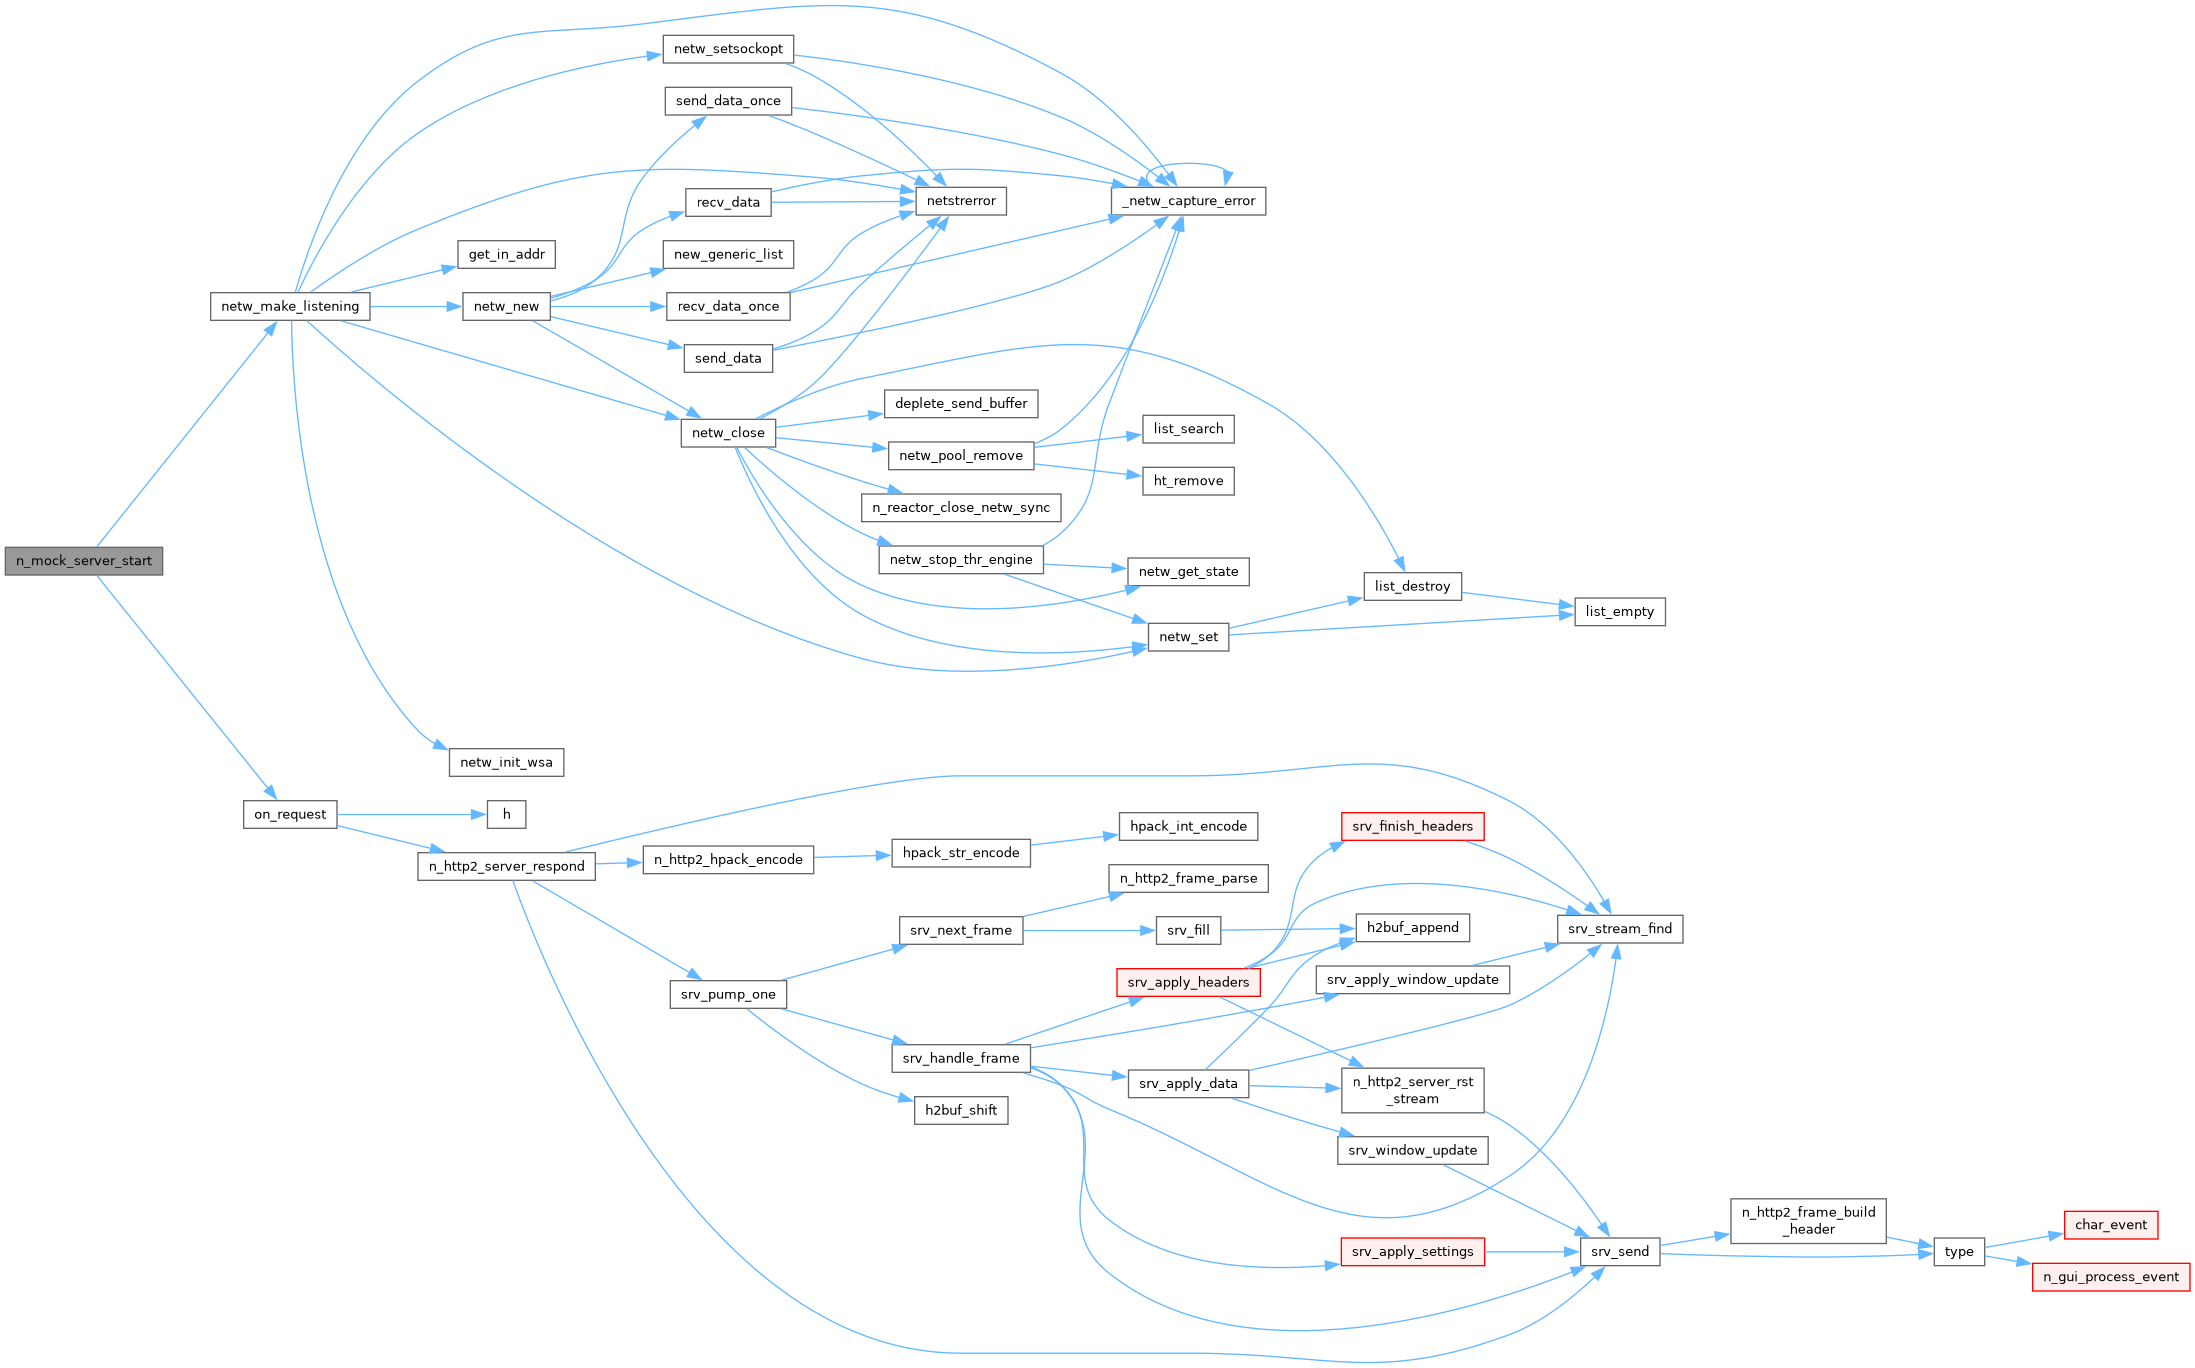
References __n_assert, FreeNoLog, LOG_ERR, LOG_INFO, Malloc, n_log, netw_make_listening(), NETWORK_IPALL, on_request(), port, port_str, and server.
Referenced by main().
| void n_mock_server_stop | ( | N_MOCK_SERVER * | server | ) |
signal the mock server to stop accepting connections
signal the mock server to stop accepting connections
| server | mock server handle |
Definition at line 8012 of file n_network.c.
References __n_assert, and server.
Referenced by main().
| void n_netw_clear_connect_errors | ( | void | ) |
Clear pre-connection errors on this thread.
Definition at line 132 of file n_network.c.
References s_connect_err_count, and s_connect_err_next.
| void n_netw_clear_errors | ( | NETWORK * | netw | ) |
Clear captured errors on a NETWORK handle.
Definition at line 116 of file n_network.c.
References netw.
| const char * n_netw_get_connect_error | ( | int | index | ) |
Get pre-connection error message by index.
Returns NULL if out of range
Definition at line 126 of file n_network.c.
References s_connect_err_count, s_connect_err_next, and s_connect_errors.
| int n_netw_get_connect_error_count | ( | void | ) |
Get number of pre-connection errors captured on this thread.
Definition at line 122 of file n_network.c.
References s_connect_err_count.
| const char * n_netw_get_error | ( | const NETWORK * | netw, |
| int | index ) |
Get captured error message by index (0 = oldest).
Returns NULL if out of range
Definition at line 110 of file n_network.c.
References netw.
| int n_netw_get_error_count | ( | const NETWORK * | netw | ) |
Get number of captured errors on a NETWORK handle.
Definition at line 106 of file n_network.c.
References netw.
| void n_proxy_cfg_free | ( | N_PROXY_CFG ** | cfg | ) |
Free an N_PROXY_CFG created by n_proxy_cfg_parse().
| cfg | Pointer to pointer; set to NULL on return. |
Definition at line 8492 of file n_network.c.
References FreeNoLog, N_PROXY_CFG::host, N_PROXY_CFG::password, N_PROXY_CFG::scheme, and N_PROXY_CFG::username.
Referenced by main().
| N_PROXY_CFG * n_proxy_cfg_parse | ( | const char * | url | ) |
Parse a proxy URL string into an N_PROXY_CFG struct.
Accepted formats: http://host:port http://user:pass@host:port https://host:port https://user:pass@host:port socks5://host:port socks5://user:pass@host:port
| url | Proxy URL string. Must not be NULL. |
Definition at line 8397 of file n_network.c.
References FreeNoLog, N_PROXY_CFG::host, LOG_ERR, Malloc, n_log, N_PROXY_CFG::password, N_PROXY_CFG::port, port, N_PROXY_CFG::scheme, and N_PROXY_CFG::username.
Referenced by main().
| int n_proxy_connect_socks5 | ( | const N_PROXY_CFG * | proxy, |
| const char * | target_host, | ||
| int | target_port ) |
Open a TCP connection through a SOCKS5 proxy.
Performs the SOCKS5 handshake (no-auth or user/pass auth), requests connection to target_host:target_port. Returns the raw socket fd ready for use.
| proxy | Parsed proxy configuration. Must not be NULL. |
| target_host | Destination hostname. |
| target_port | Destination port. |
Definition at line 8702 of file n_network.c.
References _proxy_tcp_connect(), N_PROXY_CFG::host, LOG_DEBUG, LOG_ERR, n_log, N_PROXY_CFG::password, N_PROXY_CFG::port, and N_PROXY_CFG::username.
| int n_proxy_connect_tunnel | ( | const N_PROXY_CFG * | proxy, |
| const char * | target_host, | ||
| int | target_port ) |
Open a TCP connection through an HTTP proxy using CONNECT tunneling.
Connects to the proxy, issues: CONNECT target_host:target_port HTTP/1.1 Host: target_host:target_port Proxy-Authorization: Basic base64(user:pass) (if credentials present)
Verifies the proxy responds with 200 Connection established. Returns the raw socket file descriptor ready for a TLS handshake or plain HTTP use over the tunnel.
| proxy | Parsed proxy configuration. Must not be NULL. |
| target_host | Destination hostname. |
| target_port | Destination port. |
Definition at line 8503 of file n_network.c.
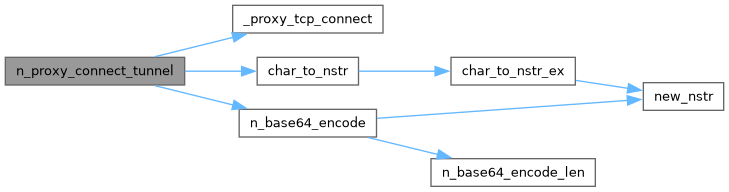
References _proxy_tcp_connect(), char_to_nstr(), N_STR::data, free_nstr, N_PROXY_CFG::host, LOG_DEBUG, LOG_ERR, n_base64_encode(), n_log, N_PROXY_CFG::password, N_PROXY_CFG::port, and N_PROXY_CFG::username.
| int n_proxy_connect_tunnel_ssl | ( | const N_PROXY_CFG * | proxy, |
| const char * | target_host, | ||
| int | target_port ) |
Open a TCP connection through an HTTPS proxy using CONNECT tunneling.
Like n_proxy_connect_tunnel(), but connects to the proxy over TLS first. The CONNECT request and response are exchanged over the encrypted channel. After the tunnel is established, the proxy TLS session is torn down and the raw socket fd is returned, ready for a second TLS handshake to the target or plain HTTP use.
| proxy | Parsed proxy configuration (scheme must be "https"). |
| target_host | Destination hostname. |
| target_port | Destination port. |
Definition at line 8576 of file n_network.c.
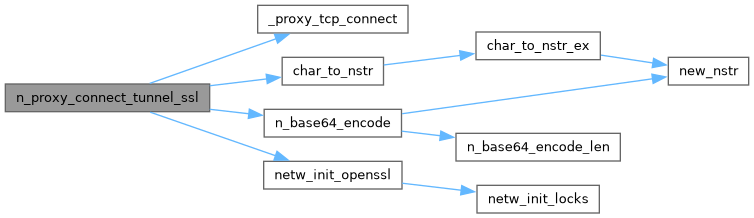
References _proxy_tcp_connect(), char_to_nstr(), N_STR::data, free_nstr, N_PROXY_CFG::host, LOG_DEBUG, LOG_ERR, n_base64_encode(), n_log, netw_init_openssl(), N_PROXY_CFG::password, N_PROXY_CFG::port, and N_PROXY_CFG::username.
| void n_sse_conn_free | ( | N_SSE_CONN ** | conn | ) |
free an SSE connection
free an SSE connection
| conn | pointer to pointer, set to NULL |
Definition at line 7423 of file n_network.c.
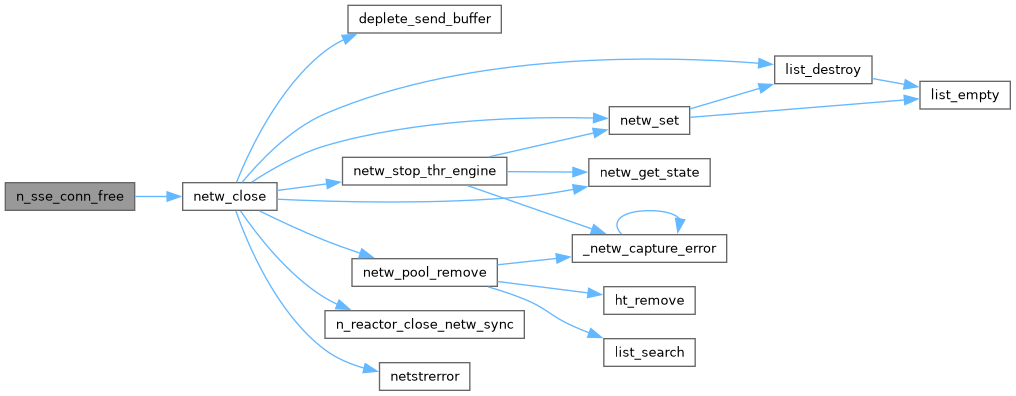
References __n_assert, FreeNoLog, N_SSE_CONN::netw, and netw_close().
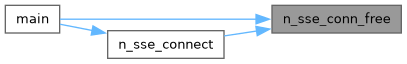
Referenced by main(), and n_sse_connect().
| N_SSE_CONN * n_sse_connect | ( | const char * | host, |
| const char * | port, | ||
| const char * | path, | ||
| int | use_ssl, | ||
| const char * | user_agent, | ||
| void(* | on_event )(N_SSE_EVENT *, N_SSE_CONN *, void *), | ||
| void * | user_data ) |
connect to an SSE endpoint and start reading events (blocks until stopped).
| user_agent | optional User-Agent header value. NULL emits no User-Agent header; some servers (e.g. Wikimedia) reject anonymous clients with 403. |
connect to an SSE endpoint and start reading events (blocks until stopped).
Blocks until stopped or connection closes. Calls on_event for each complete SSE event received.
| host | hostname |
| port | port string |
| path | resource path |
| use_ssl | 1 for https, 0 for http |
| on_event | callback for each received event |
| user_data | passed to callback |
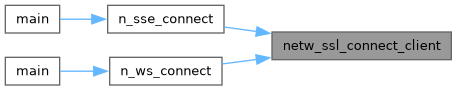
Definition at line 7508 of file n_network.c.
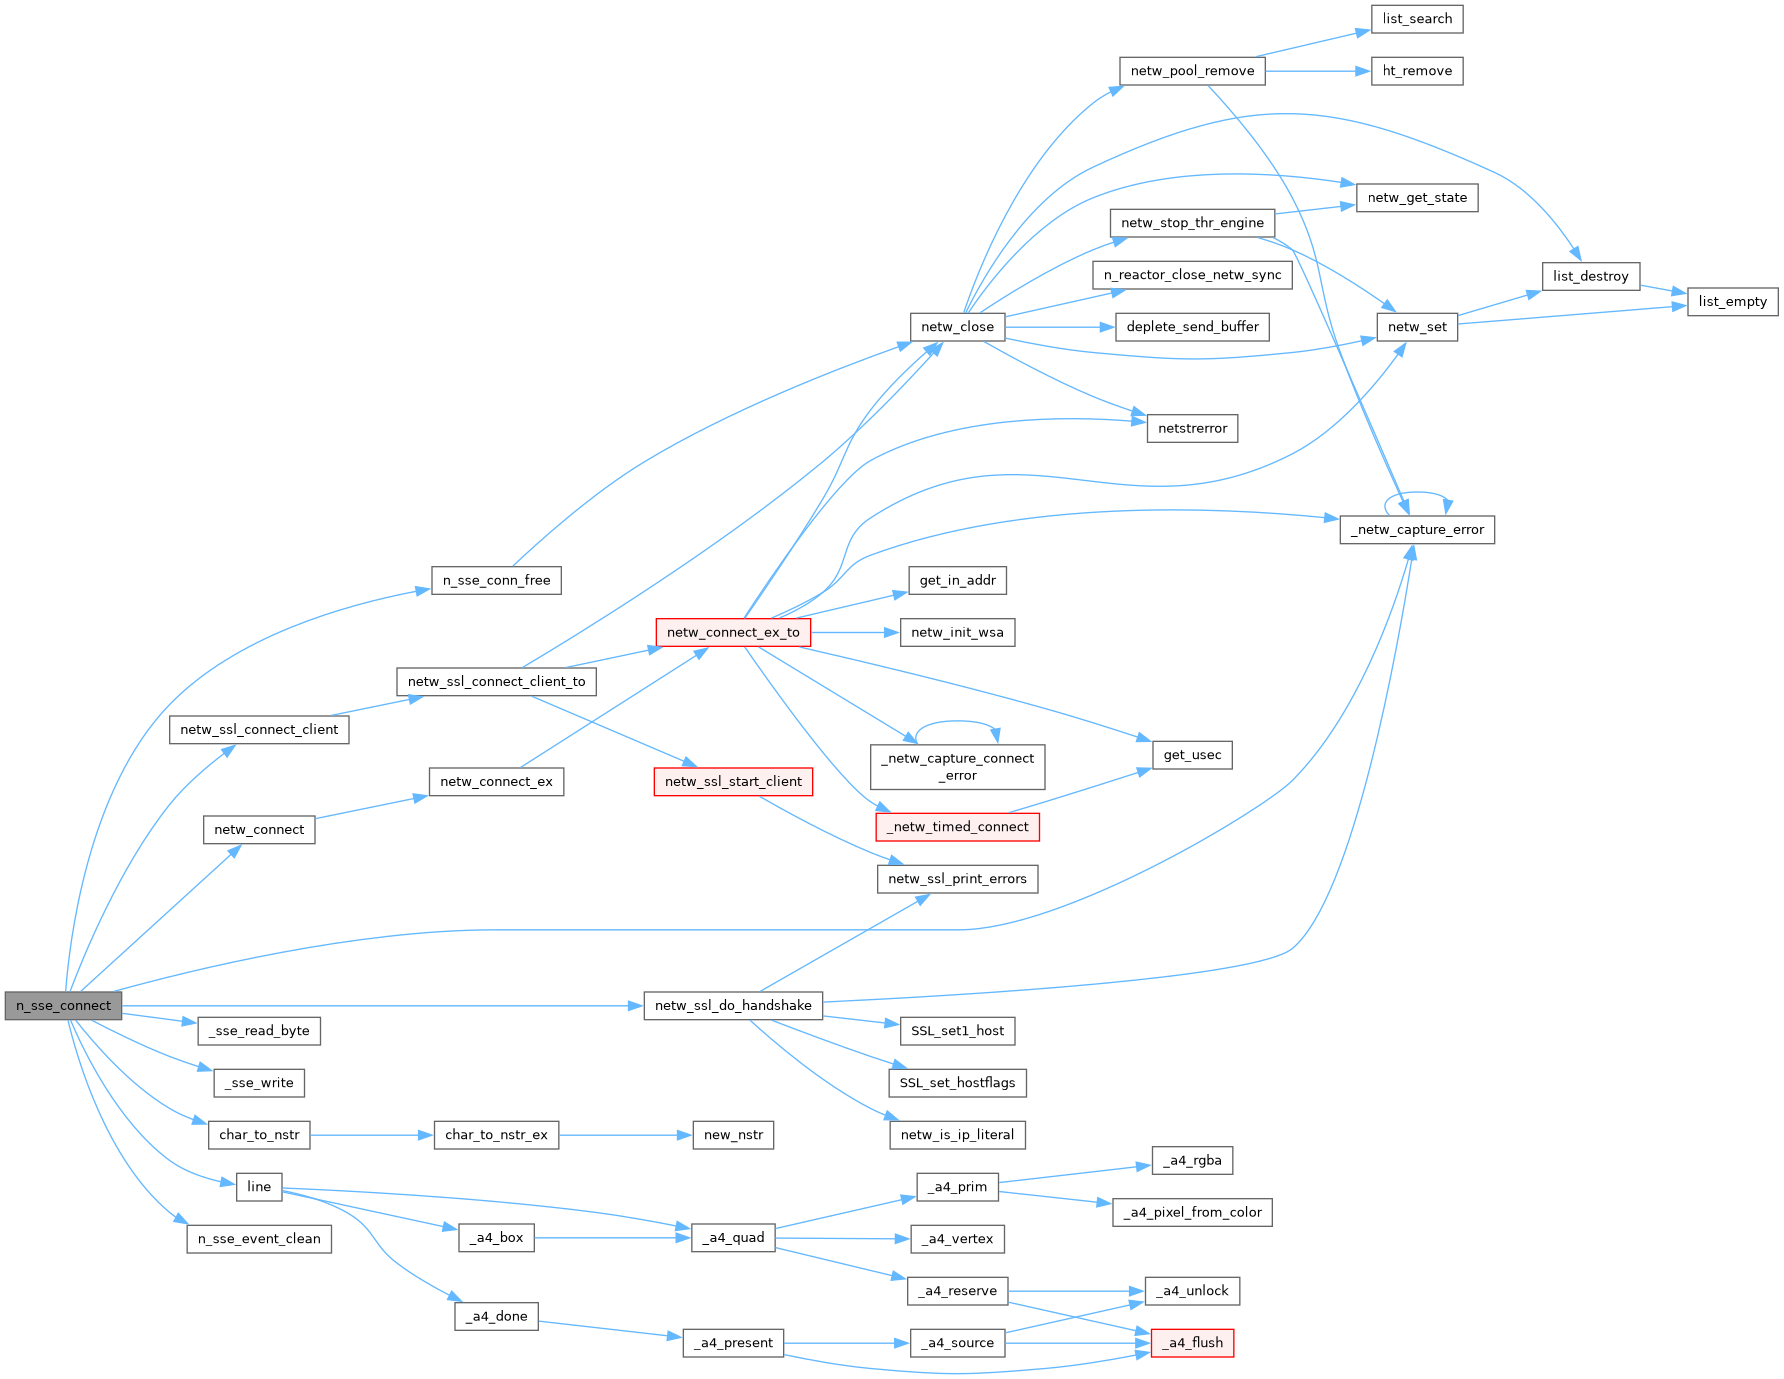
References __n_assert, _netw_capture_error(), _sse_read_byte(), _sse_write(), char_to_nstr(), N_SSE_EVENT::data, N_SSE_EVENT::event, free_nstr, N_SSE_EVENT::id, line(), LOG_DEBUG, LOG_ERR, LOG_INFO, Malloc, n_log, n_sse_conn_free(), n_sse_event_clean(), N_SSE_CONN::netw, netw_connect(), netw_ssl_connect_client(), netw_ssl_do_handshake(), NETWORK_IPALL, nstrprintf_cat, N_SSE_CONN::on_event, port, N_SSE_EVENT::retry, N_SSE_CONN::stop_flag, and N_SSE_CONN::user_data.
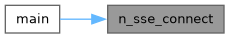
Referenced by main().
| void n_sse_event_clean | ( | N_SSE_EVENT * | event | ) |
free an SSE event's contents (does not free the event struct itself)
free an SSE event's contents (does not free the event struct itself)
| event | the event to clean |
Definition at line 7402 of file n_network.c.
References N_SSE_EVENT::data, N_SSE_EVENT::event, free_nstr, and N_SSE_EVENT::id.
Referenced by n_sse_connect().
| void n_sse_stop | ( | N_SSE_CONN * | conn | ) |
signal the SSE connection to stop reading
signal the SSE connection to stop reading
| conn | SSE connection |
Definition at line 7414 of file n_network.c.
References __n_assert, and N_SSE_CONN::stop_flag.
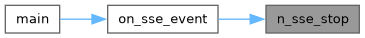
Referenced by on_sse_event().
build a URL string from parsed components
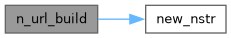
Definition at line 8094 of file n_network.c.
References N_URL::host, new_nstr(), nstrprintf, nstrprintf_cat, N_URL::path, N_URL::port, N_URL::query, and N_URL::scheme.
produce a canonical URL string for dedup (lowercase scheme/host, drop default port, remove .
/ and ../ segments, keep query)
produce a canonical URL string for dedup (lowercase scheme/host, drop default port, remove .
Lowercases the scheme and host, drops the default port (80 for http, 443 for https), removes "." and ".." path segments, and keeps the query verbatim.
| u | a parsed URL |
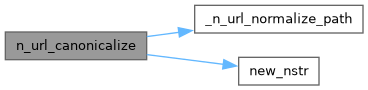
Definition at line 8166 of file n_network.c.
References _n_url_normalize_path(), N_URL::host, new_nstr(), nstrprintf, nstrprintf_cat, N_URL::path, N_URL::port, N_URL::query, and N_URL::scheme.
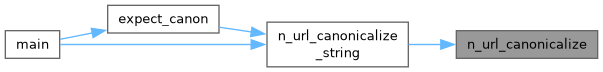
Referenced by n_url_canonicalize_string().
| N_STR * n_url_canonicalize_string | ( | const char * | url | ) |
parse and canonicalize a URL string in one call
| url | the URL string |
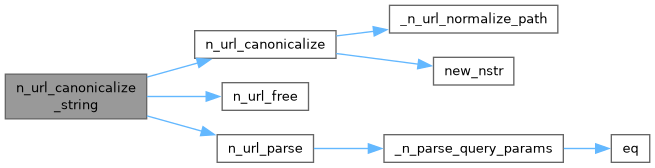
Definition at line 8195 of file n_network.c.
References n_url_canonicalize(), n_url_free(), and n_url_parse().
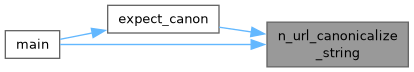
Referenced by expect_canon(), and main().
| N_STR * n_url_decode | ( | const char * | str | ) |
decode a percent-encoded string (returns N_STR)
Definition at line 8321 of file n_network.c.
References new_nstr(), and nstrprintf_cat.
| N_STR * n_url_encode | ( | const char * | str | ) |
percent-encode a string for use in URLs (delegates to n_str_url_encode())
Definition at line 8317 of file n_network.c.
References n_str_url_encode().
| void n_url_free | ( | N_URL ** | u | ) |
free a N_URL and all its members
Definition at line 8342 of file n_network.c.
References FreeNoLog, N_URL::host, N_URL_PARAM::key, N_URL::nb_params, N_URL::params, N_URL::path, N_URL::query, N_URL::scheme, and N_URL_PARAM::value.
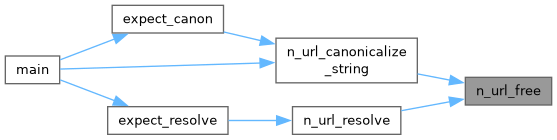
Referenced by n_url_canonicalize_string(), and n_url_resolve().
| N_URL * n_url_parse | ( | const char * | url | ) |
parse a URL string into components
Definition at line 8055 of file n_network.c.
References _n_parse_query_params(), N_URL::host, Malloc, N_URL::path, N_URL::port, N_URL::query, and N_URL::scheme.
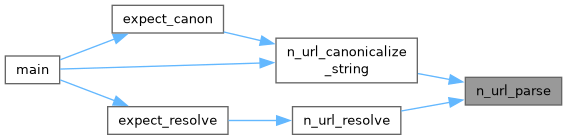
Referenced by n_url_canonicalize_string(), and n_url_resolve().
| N_STR * n_url_resolve | ( | const char * | base, |
| const char * | ref ) |
resolve a (possibly relative) reference against an absolute base URL (RFC 3986 section 5)
resolve a (possibly relative) reference against an absolute base URL (RFC 3986 section 5)
Implements RFC 3986 section 5 reference resolution: a base URL plus a reference found in a document (an href, src, or action) produce an absolute URL. Handles absolute references (returned verbatim), scheme-relative ("//host/path"), absolute-path ("/path"), query-only ("?q"), fragment-only (resolves to the base resource), and relative-path references (merged against the base path). The fragment is dropped (it is not part of the resource identity for crawling) and "." / ".." path segments are removed. The result is not lowercased or otherwise canonicalized; pass it through n_url_canonicalize_string for a dedup key.
| base | an absolute base URL (scheme://host/...). NULL returns NULL. |
| ref | the reference to resolve. NULL is treated as the empty string. |
Definition at line 8233 of file n_network.c.
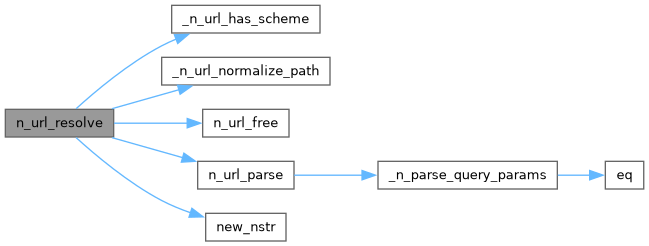
References _n_url_has_scheme(), _n_url_normalize_path(), N_URL::host, n_url_free(), n_url_parse(), new_nstr(), nstrprintf, nstrprintf_cat, N_URL::path, N_URL::port, N_URL::query, and N_URL::scheme.
Referenced by expect_resolve().
| void n_ws_close | ( | N_WS_CONN * | conn | ) |
send close frame and close the connection
send close frame and close the connection
Sends a close frame (opcode 0x08), attempts to read a close response, then closes the underlying NETWORK.
| conn | WebSocket connection |
Definition at line 7348 of file n_network.c.
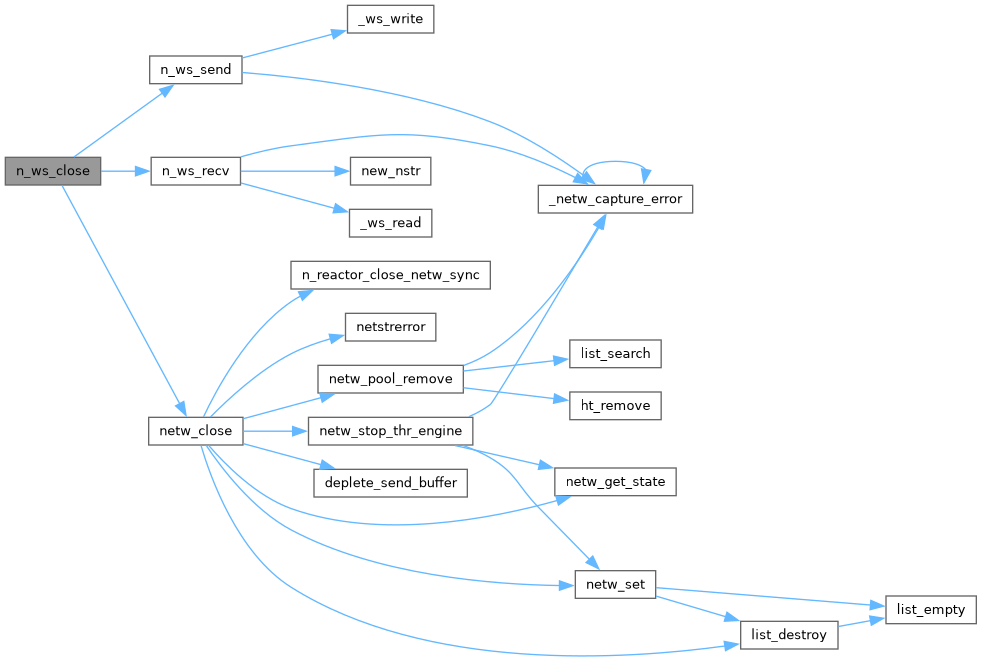
References __n_assert, N_WS_CONN::connected, free_nstr, N_WS_OP_CLOSE, n_ws_recv(), n_ws_send(), N_WS_CONN::netw, netw_close(), and N_WS_MESSAGE::payload.
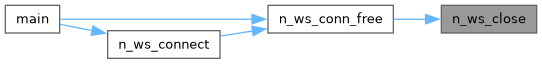
Referenced by n_ws_conn_free().
| void n_ws_conn_free | ( | N_WS_CONN ** | conn | ) |
free a WebSocket connection structure
free a WebSocket connection structure
Closes the connection if still open, then frees all members.
| conn | pointer to pointer, set to NULL |
Definition at line 7378 of file n_network.c.
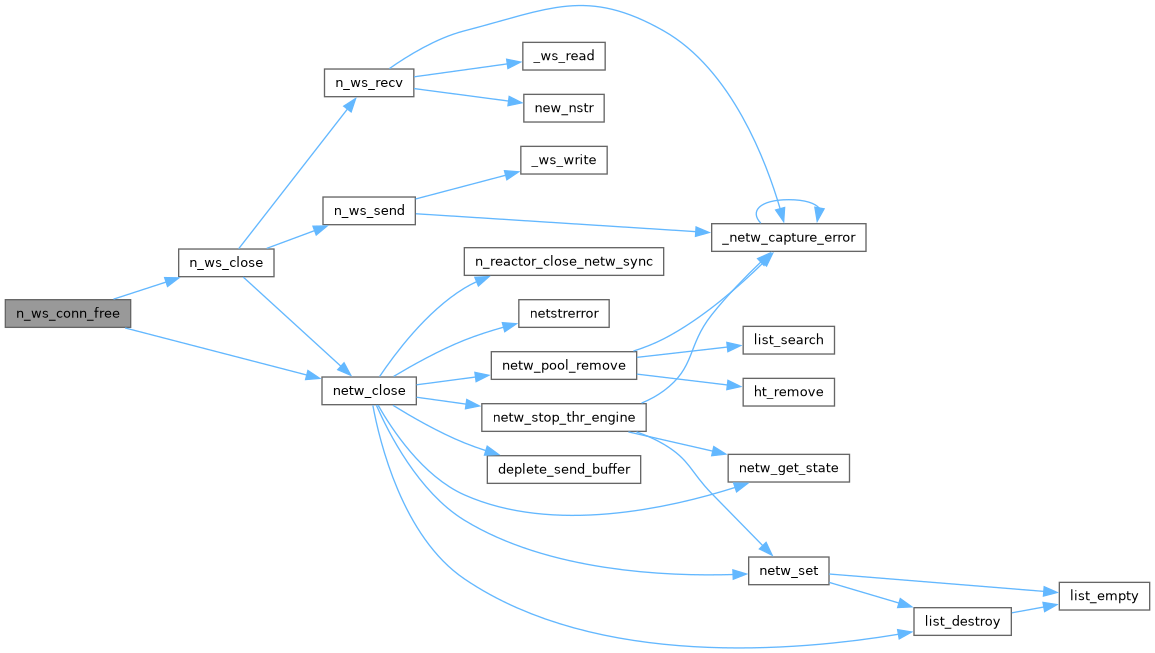
References __n_assert, N_WS_CONN::connected, FreeNoLog, N_WS_CONN::host, n_ws_close(), N_WS_CONN::netw, netw_close(), and N_WS_CONN::path.
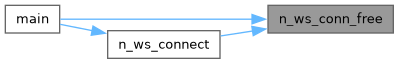
Referenced by main(), and n_ws_connect().
| N_WS_CONN * n_ws_connect | ( | const char * | host, |
| const char * | port, | ||
| const char * | path, | ||
| int | use_ssl ) |
connect to a WebSocket server (ws:// or wss://) and perform the HTTP/1.1 upgrade handshake
connect to a WebSocket server (ws:// or wss://) and perform the HTTP/1.1 upgrade handshake
Performs the HTTP/1.1 upgrade handshake per RFC 6455.
| host | hostname to connect to |
| port | port string (e.g. "443") |
| path | resource path (e.g. "/") |
| use_ssl | 1 for wss://, 0 for ws:// |
Definition at line 6995 of file n_network.c.
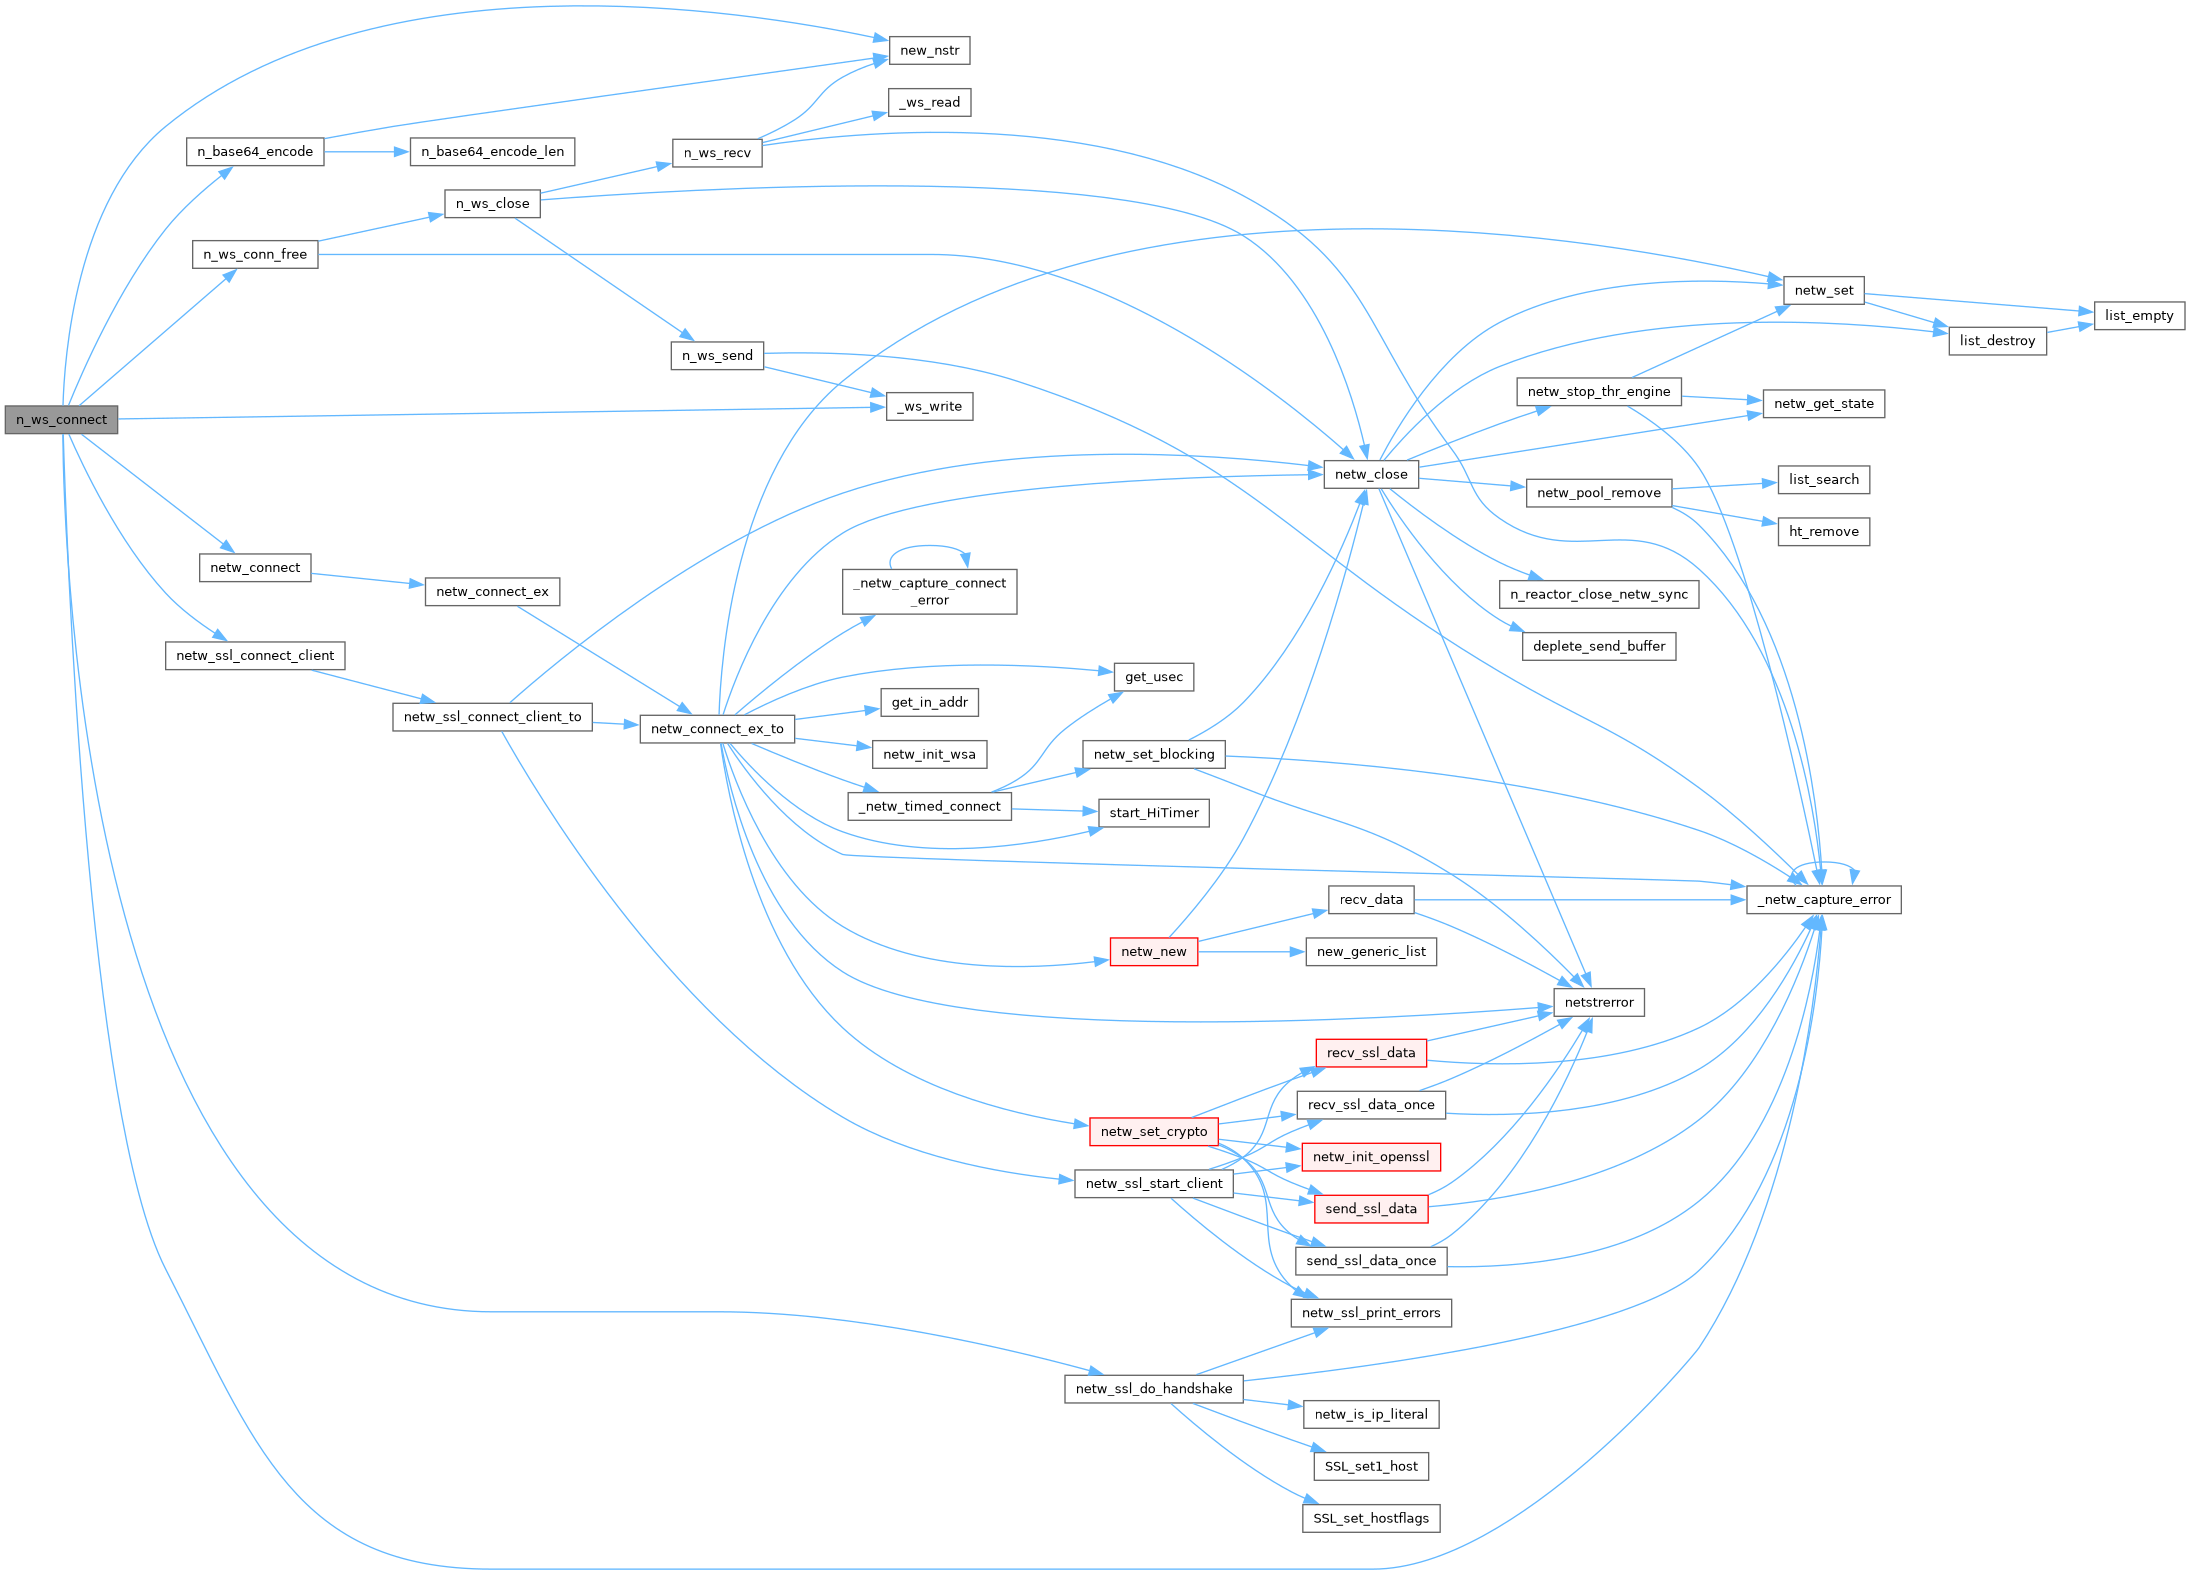
References __n_assert, _netw_capture_error(), _ws_write(), N_WS_CONN::connected, NETWORK::crypto_algo, N_STR::data, free_nstr, N_WS_CONN::host, NETWORK::link, LOG_DEBUG, LOG_ERR, LOG_INFO, Malloc, n_base64_encode(), n_log, n_ws_conn_free(), N_WS_CONN::netw, netw_connect(), NETW_ENCRYPT_OPENSSL, netw_ssl_connect_client(), netw_ssl_do_handshake(), NETWORK_IPALL, new_nstr(), N_WS_CONN::path, port, N_SOCKET::sock, NETWORK::ssl, and N_STR::written.
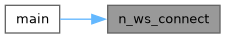
Referenced by main().
| size_t n_ws_frame_build | ( | int | fin, |
| int | opcode, | ||
| int | do_mask, | ||
| const unsigned char * | payload, | ||
| size_t | len, | ||
| const unsigned char | mask_key[4], | ||
| unsigned char * | out, | ||
| size_t | out_cap ) |
build a WebSocket frame into out (optionally masking the payload).
Returns the number of bytes written, or 0 when out_cap is too small.
Definition at line 7757 of file n_network.c.
Referenced by test_frame_codec().
| int n_ws_frame_parse | ( | const unsigned char * | buf, |
| size_t | len, | ||
| N_WS_FRAME * | frame, | ||
| size_t * | consumed ) |
parse one WebSocket frame from a byte buffer (stateless).
Returns 1 and fills frame + *consumed (total frame bytes) on a complete frame, 0 when more bytes are needed, -1 on a malformed or over-large frame. payload aliases buf.
parse one WebSocket frame from a byte buffer (stateless).
| buf | The input bytes (one or more frames, possibly partial). |
| len | Number of readable bytes in buf. |
| frame | Receives the parsed header and a payload pointer aliasing buf. |
| consumed | Receives the total frame size in bytes on a complete frame. |
Definition at line 7702 of file n_network.c.
References N_WS_FRAME::fin, N_WS_FRAME::mask, N_WS_FRAME::masked, N_WS_FRAME_MAX_PAYLOAD, N_WS_FRAME::opcode, N_WS_FRAME::payload, N_WS_FRAME::payload_len, and N_WS_FRAME::rsv.
Referenced by test_frame_codec().
| int n_ws_recv | ( | N_WS_CONN * | conn, |
| N_WS_MESSAGE * | msg_out ) |
receive one WebSocket frame
receive one WebSocket frame
Reads the frame header, extended length, optional mask, and payload.
| conn | WebSocket connection |
| msg_out | output: populated message. Caller must free payload with free_nstr. |
Definition at line 7266 of file n_network.c.
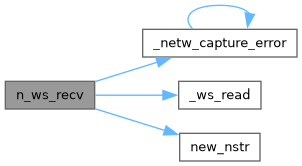
References __n_assert, _netw_capture_error(), _ws_read(), N_STR::data, free_nstr, LOG_ERR, N_WS_MESSAGE::masked, n_log, N_WS_MAX_PAYLOAD, N_WS_CONN::netw, new_nstr(), N_WS_MESSAGE::opcode, N_WS_MESSAGE::payload, and N_STR::written.
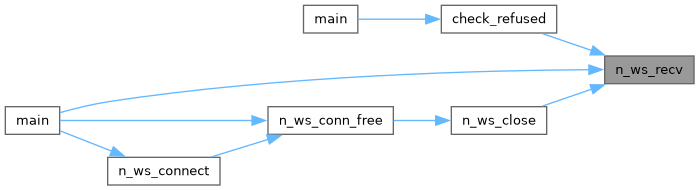
Referenced by check_refused(), main(), and n_ws_close().
| int n_ws_send | ( | N_WS_CONN * | conn, |
| const char * | payload, | ||
| size_t | len, | ||
| int | opcode ) |
send a WebSocket frame (client always masks)
send a WebSocket frame (client always masks)
Builds a masked WebSocket frame per RFC 6455 and sends it.
| conn | WebSocket connection |
| payload | data to send |
| len | payload length |
| opcode | frame opcode (N_WS_OP_TEXT, etc.) |
Definition at line 7199 of file n_network.c.
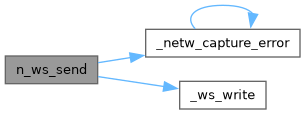
References __n_assert, _netw_capture_error(), _ws_write(), FreeNoLog, LOG_ERR, Malloc, n_log, and N_WS_CONN::netw.
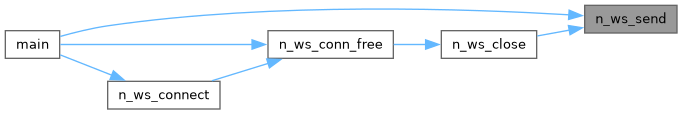
Referenced by main(), and n_ws_close().
| void n_ws_unmask | ( | unsigned char * | dst, |
| const unsigned char * | src, | ||
| size_t | len, | ||
| const unsigned char | mask[4] ) |
XOR-unmask len bytes of src into dst using a 4-byte WebSocket mask key.
Definition at line 7749 of file n_network.c.
Referenced by test_frame_codec().
Accepting routine.
Accepting routine.
Network 'from' must be allocated with netw_make_listening.
| from | The network from which to obtaion the connection |
Definition at line 4287 of file n_network.c.
References MAX_LIST_ITEMS, and netw_accept_from_ex().
Referenced by check_refused(), main(), netw_accept_ssl_with_sni_cb(), and server_fn().
| NETWORK * netw_accept_from_ex | ( | NETWORK * | from, |
| size_t | send_list_limit, | ||
| size_t | recv_list_limit, | ||
| int | blocking, | ||
| int * | retval ) |
Accepting routine extended.
Accepting routine extended.
Network 'from' must be allocated with netw_make_listening.
| from | the network from where we accept |
| send_list_limit | Internal sending list maximum number of item. 0 for unrestricted |
| recv_list_limit | Internal receiving list maximum number of item. 0 for unrestricted |
| blocking | set to -1 to make it non blocking, to 0 for blocking, else it's the select timeout value in msecs. |
| retval | EAGAIN ou EWOULDBLOCK or neterrno (use netstrerr( retval) to obtain a string describing the code ) |
Definition at line 4101 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, NETWORK::crypto_algo, NETWORK::ctx, endif, FreeNoLog, get_in_addr(), N_SOCKET::is_blocking, NETWORK::link, LOG_DEBUG, LOG_ERR, Malloc, n_log, neterrno, netstrerror(), netw, netw_close(), NETW_ENCRYPT_OPENSSL, netw_init_wsa(), netw_new(), NETW_RUN, NETW_SERVER, netw_set(), netw_set_blocking(), netw_setsockopt(), netw_ssl_print_errors(), NETW_THR_ENGINE_STOPPED, N_SOCKET::port, recv_ssl_data(), recv_ssl_data_once(), send_ssl_data(), send_ssl_data_once(), N_SOCKET::sock, and SOCKET_SIZE_FORMAT.
Referenced by main(), main(), n_http_server_run(), n_mock_server_run(), netw_accept_from(), netw_accept_nonblock_from(), and netw_accept_pool_thread_func().
Accepting routine.
Accepting routine.
Network 'from' must be allocated with netw_make_listening.
| from | The network from which to obtaion the connection |
| blocking | set to -1 to make it non blocking, to 0 for blocking, else it's the select timeout value in mseconds. |
Definition at line 4297 of file n_network.c.
References MAX_LIST_ITEMS, and netw_accept_from_ex().
Referenced by server_fn().
| NETWORK * netw_accept_ssl_with_sni_cb | ( | NETWORK * | listen, |
| netw_sni_pick_cb | pick, | ||
| void * | user_data ) |
accept a TLS connection, selecting the server certificate per client SNI via pick() during the handshake
accept a TLS connection, selecting the server certificate per client SNI via pick() during the handshake
Accepts a plaintext connection from listen, then upgrades it to a TLS server via netw_ssl_server_handshake(), so the pick callback supplies a leaf matching the client's requested host during the handshake.
| listen | the listening NETWORK from netw_make_listening |
| pick | callback that supplies a cert/key for a given SNI host |
| user_data | opaque pointer passed to pick |
Definition at line 2116 of file n_network.c.
References __n_assert, netw_accept_from(), netw_close(), and netw_ssl_server_handshake().
Referenced by server_fn(), and server_thread().
Add a message to send in aimed NETWORK.
Definition at line 4313 of file n_network.c.
References __n_assert, _netw_capture_error(), N_STR::data, free_nstr_ptr(), g_netw_bytes_sent, N_STR::length, list_push(), LOG_ERR, n_log, n_reactor_notify_send(), netw, netw_atomic_read_reactor_handle, netw_atomic_read_reactor_mode, and N_STR::written.
Referenced by client_worker_echo(), handle_client(), netw_pool_broadcast(), netw_send_ident(), netw_send_ping(), netw_send_position(), netw_send_quit(), netw_send_string_to(), netw_send_string_to_all(), on_send_click(), run_client(), run_server(), send_net_datas(), userlist_add_msg_to_ex(), userlist_send_waiting_msgs(), and userlist_user_send_waiting_msgs().
| int netw_add_msg_ex | ( | NETWORK * | netw, |
| char * | str, | ||
| unsigned int | length ) |
Add a char message to send in the aimed NETWORK.
Add a char message to send in the aimed NETWORK.
| netw | NETWORK where add the message |
| str | the message to add |
| length | the size of the message to add |
Definition at line 4379 of file n_network.c.
References __n_assert, N_STR::data, free_nstr_ptr(), N_STR::length, list_push(), Malloc, netw, and N_STR::written.
adopt an already-connected socket fd into a fresh client NETWORK (plain send/recv)
adopt an already-connected socket fd into a fresh client NETWORK (plain send/recv)
Wraps a connected socket file descriptor (for example one returned by n_proxy_connect_tunnel / n_proxy_connect_socks5) in a newly allocated client NETWORK so the blocking send/recv helpers (send_data / netw_read_all / ...) can run over it. The NETWORK is created with the plain (non-SSL) send/recv vtable; promote it with netw_ssl_start_client + netw_ssl_do_handshake to speak TLS over the adopted socket. On success the NETWORK owns fd and closes it in netw_close; on failure fd is left open for the caller to close.
| netw | output: receives the new NETWORK. Must point to NULL on entry. |
| fd | a connected socket descriptor (must not be INVALID_SOCKET). |
| host | hostname recorded for logging, or NULL. |
| port | port string recorded for logging, or NULL. |
Definition at line 8840 of file n_network.c.
References __n_assert, LOG_DEBUG, LOG_ERR, MAX_LIST_ITEMS, n_log, netw, NETW_CLIENT, netw_close(), netw_init_wsa(), netw_new(), NETW_RUN, netw_set(), NETW_THR_ENGINE_STOPPED, and port.
Referenced by main().
| int netw_bind_udp | ( | NETWORK ** | netw, |
| char * | addr, | ||
| char * | port, | ||
| int | ip_version ) |
Create a UDP bound socket.
Exclusive on every platform, on the same terms as netw_make_listening: SO_REUSEADDR is POSIX-only because on Windows it permits binding over a port another process already holds.
Create a UDP bound socket.
| netw | A NETWORK **network to bind |
| addr | Address to bind, NULL for wildcard |
| port | Port to bind to |
| ip_version | NETWORK_IPALL for both ipv4 and ipv6 , NETWORK_IPV4 or NETWORK_IPV6 |
Definition at line 3735 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, addr, FreeNoLog, get_in_addr(), ip_version, LOG_DEBUG, LOG_ERR, Malloc, MAX_LIST_ITEMS, n_log, neterrno, netstrerror(), netw, netw_close(), netw_init_wsa(), netw_new(), NETW_RUN, NETW_SERVER, netw_set(), netw_setsockopt(), NETW_THR_ENGINE_STOPPED, NETWORK_IPV4, NETWORK_IPV6, NETWORK_UDP, port, recv_udp_data(), and send_udp_data().
Referenced by check_exclusive(), main(), and run_server().
| int netw_build_http_response | ( | N_STR ** | http_response, |
| int | status_code, | ||
| const char * | server_name, | ||
| const char * | content_type, | ||
| char * | additional_headers, | ||
| N_STR * | body ) |
build HTTP response
build HTTP response
| http_response | pointer to a N_STR *response. Will be set to the response, or NULL |
| status_code | response http status code |
| server_name | response 'Server' in headers |
| content_type | response 'Content-Type' in headers |
| additional_headers | additional response headers, can be "" if no additional headers, else 'backslash r backslash n' separated key: values |
| body | response 'Server' in headers |
Definition at line 6897 of file n_network.c.
References __n_assert, LOG_DEBUG, n_log, netw_get_http_date(), netw_get_http_status_message(), nstrcat, nstrprintf, and N_STR::written.
Referenced by build_secure_response(), and handle_request().
| size_t netw_calculate_urlencoded_size | ( | const char * | str, |
| size_t | len ) |
calculate URL-encoded size
calculate URL-encoded size
| str | clear string from which we want to know the urlencoded size |
| len | length of the input string |
Definition at line 6075 of file n_network.c.
References __n_assert.
Referenced by netw_urlencode().
| int netw_close | ( | NETWORK ** | netw | ) |
Closing.
Closing.
| netw | A NETWORK *network to close |
Definition at line 3367 of file n_network.c.
References __n_assert, _str, deplete_send_buffer(), endif, Free, FreeNoLog, list_destroy(), list_foreach, LOG_DEBUG, LOG_ERR, LOG_WARNING, N_ENUM_ENTRY, n_log, n_reactor_close_netw_sync(), neterrno, netstrerror(), netw, NETW_DESTROY_RECVBUF, NETW_DESTROY_SENDBUF, NETW_ENCRYPT_OPENSSL, netw_get_state(), netw_pool_remove(), NETW_SERVER, netw_set(), netw_stop_thr_engine(), NETW_THR_ENGINE_STARTED, pool, and SOCKET_SIZE_FORMAT.
Referenced by _worker(), bind_free(), bind_free(), bind_free(), check_exclusive(), check_refused(), cl_close(), client_connect(), client_worker_echo(), client_worker_fast(), dispatch_to_pool(), handle_client(), handle_inline_and_count(), main(), main(), main(), manage_client(), n_http_server_free(), n_http_server_run(), n_mock_server_free(), n_mock_server_run(), n_sse_conn_free(), n_ws_close(), n_ws_conn_free(), netw_accept_from_ex(), netw_accept_pool_thread_func(), netw_accept_ssl_with_sni_cb(), netw_adopt_client_fd(), netw_bind_udp(), netw_connect_ex_to(), netw_connect_nonblock(), netw_connect_udp(), netw_make_listening(), netw_new(), netw_set_blocking(), netw_ssl_connect_client_to(), on_accept_pooled(), run_client(), run_client(), run_server(), run_server(), server_fn(), server_fn(), server_fn(), server_thread(), ssl_network_thread(), and try_connect().
| int netw_connect | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| int | ip_version ) |
Connecting.
Connecting.
| netw | a NETWORK *object |
| host | Host or IP to connect to |
| port | Port to use to connect |
| ip_version | NETWORK_IPALL for both ipv4 and ipv6 , NETWORK_IPV4 or NETWORK_IPV6 |
Definition at line 2898 of file n_network.c.
References _str, ip_version, LOG_INFO, MAX_LIST_ITEMS, n_log, netw, netw_connect_ex(), and port.
Referenced by cl_connect(), client_worker_echo(), client_worker_fast(), main(), n_sse_connect(), n_ws_connect(), and run_client().
| int netw_connect_check | ( | NETWORK * | netw | ) |
advance a non-blocking connect: TRUE connected, NETW_IO_WANT_WRITE keep polling for writability, FALSE all addresses failed
advance a non-blocking connect: TRUE connected, NETW_IO_WANT_WRITE keep polling for writability, FALSE all addresses failed
Self-contained: it tests the socket for writability (connect completion) without blocking, consults SO_ERROR, and on a failed address transparently moves on to the next resolved address. Call it whenever the socket becomes writable (or on a poll timeout); it never blocks.
| netw | a NETWORK from netw_connect_nonblock() |
Definition at line 2822 of file n_network.c.
References __n_assert, _netw_start_nonblock_connect(), _str, FreeNoLog, get_in_addr(), LOG_ERR, LOG_INFO, n_log, neterrno, netstrerror(), netw, NETW_CLIENT, NETW_IO_WANT_WRITE, NETW_RUN, netw_set(), NETW_THR_ENGINE_STOPPED, and SOCKET_SIZE_FORMAT.
Referenced by drive_connect().
| int netw_connect_ex | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| size_t | send_list_limit, | ||
| size_t | recv_list_limit, | ||
| int | ip_version, | ||
| char * | ssl_key_file, | ||
| char * | ssl_cert_file ) |
Connecting, extended.
Connecting, extended.
| netw | a NETWORK *object |
| host | Host or IP to connect to |
| port | Port to use to connect |
| send_list_limit | Internal sending list maximum number of item. From UNLIMITED_LIST_ITEMS (0) to MAX_LIST_ITEMS (SIZE_MAX). |
| recv_list_limit | Internal receiving list maximum number of item. From UNLIMITED_LIST_ITEMS (0) to MAX_LIST_ITEMS (SIZE_MAX). |
| ip_version | NETWORK_IPALL for both ipv4 and ipv6 , NETWORK_IPV4 or NETWORK_IPV6 |
| ssl_key_file | NULL or the path to the SSL key file to use. If set, a ssl_cert_file must also be provided |
| ssl_cert_file | NULL or the path to the SSL certificate file to use. If set, a ssl_key_file must also be provided |
Definition at line 2886 of file n_network.c.
References ip_version, netw, netw_connect_ex_to(), and port.
Referenced by netw_connect(), and netw_ssl_connect().
| int netw_connect_ex_to | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| size_t | send_list_limit, | ||
| size_t | recv_list_limit, | ||
| int | ip_version, | ||
| char * | ssl_key_file, | ||
| char * | ssl_cert_file, | ||
| int | connect_timeout_ms ) |
Connecting, extended, with a bounded connection-establishment time (connect_timeout_ms, 0 = OS default).
Connecting, extended, with a bounded connection-establishment time (connect_timeout_ms, 0 = OS default).
| netw | a NETWORK *object |
| host | Host or IP to connect to |
| port | Port to use to connect |
| send_list_limit | Internal sending list maximum number of item. From UNLIMITED_LIST_ITEMS (0) to MAX_LIST_ITEMS (SIZE_MAX). |
| recv_list_limit | Internal receiving list maximum number of item. From UNLIMITED_LIST_ITEMS (0) to MAX_LIST_ITEMS (SIZE_MAX). |
| ip_version | NETWORK_IPALL for both ipv4 and ipv6 , NETWORK_IPV4 or NETWORK_IPV6 |
| ssl_key_file | NULL or the path to the SSL key file to use. If set, a ssl_cert_file must also be provided |
| ssl_cert_file | NULL or the path to the SSL certificate file to use. If set, a ssl_key_file must also be provided |
| connect_timeout_ms | connect timeout in milliseconds, 0 = OS default |
Definition at line 2557 of file n_network.c.
References __n_assert, _netw_capture_connect_error(), _netw_capture_error(), _netw_timed_connect(), _str, FreeNoLog, get_in_addr(), get_usec(), ip_version, LOG_DEBUG, LOG_ERR, LOG_INFO, Malloc, n_log, neterrno, netstrerror(), netw, NETW_CLIENT, netw_close(), netw_init_wsa(), netw_new(), NETW_RUN, netw_set(), netw_set_crypto(), NETW_THR_ENGINE_STOPPED, NETWORK_IPV4, NETWORK_IPV6, port, and start_HiTimer().
Referenced by netw_connect_ex(), netw_connect_to(), and netw_ssl_connect_client_to().
| int netw_connect_nonblock | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| int | ip_version ) |
begin a non-blocking TCP connect: resolve and initiate connect() without waiting; drive to completion with netw_connect_check()
begin a non-blocking TCP connect: resolve and initiate connect() without waiting; drive to completion with netw_connect_check()
Resolves host : port, creates a non-blocking socket and initiates connect() on the first address, then returns immediately. Drive the connect to completion from a poll()/select() loop with netw_connect_check(); once it returns TRUE, promote the connection with netw_ssl_start_client() + netw_ssl_handshake_once() for TLS, or use it directly for plaintext. This is the non-blocking counterpart of netw_connect_to for callers that must not block a shared thread on a slow or unreachable host.
| netw | address of an empty (NULL) NETWORK* to fill |
| host | host or IP to connect to |
| port | port or service to connect to |
| ip_version | NETWORK_IPALL / NETWORK_IPV4 / NETWORK_IPV6 |
Definition at line 2760 of file n_network.c.
References __n_assert, _netw_capture_error(), _netw_start_nonblock_connect(), ip_version, LOG_ERR, Malloc, MAX_LIST_ITEMS, n_log, netw, netw_close(), netw_init_wsa(), netw_new(), NETWORK_IPV4, NETWORK_IPV6, and port.
Referenced by main().
| int netw_connect_to | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| int | ip_version, | ||
| int | connect_timeout_ms ) |
Connecting, with a bounded connection-establishment time (connect_timeout_ms, 0 = OS default).
Connecting, with a bounded connection-establishment time (connect_timeout_ms, 0 = OS default).
| netw | a NETWORK *object |
| host | Host or IP to connect to |
| port | Port to use to connect |
| ip_version | NETWORK_IPALL for both ipv4 and ipv6 , NETWORK_IPV4 or NETWORK_IPV6 |
| connect_timeout_ms | connect timeout in milliseconds, 0 = OS default |
Definition at line 2912 of file n_network.c.
References _str, ip_version, LOG_INFO, MAX_LIST_ITEMS, n_log, netw, netw_connect_ex_to(), and port.
Referenced by check_refused(), and main().
| int netw_connect_udp | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| int | ip_version ) |
Connect a UDP socket to a remote host.
| netw | A NETWORK **network to connect |
| host | Host or IP to connect to |
| port | Port to connect to |
| ip_version | NETWORK_IPALL, NETWORK_IPV4 or NETWORK_IPV6 |
Definition at line 3856 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, FreeNoLog, get_in_addr(), ip_version, LOG_DEBUG, LOG_ERR, LOG_INFO, Malloc, MAX_LIST_ITEMS, n_log, neterrno, netstrerror(), netw, NETW_CLIENT, netw_close(), netw_init_wsa(), netw_new(), NETW_RUN, netw_set(), NETW_THR_ENGINE_STOPPED, NETWORK_IPV4, NETWORK_IPV6, NETWORK_UDP, port, recv_udp_data(), and send_udp_data().
Referenced by main(), and run_client().
| int netw_destroy_pool | ( | NETWORK_POOL ** | netw_pool | ) |
destroy pool
destroy pool
| netw_pool | the address of a NETWORK_POOL *pointer to free |
Definition at line 5786 of file n_network.c.
References __n_assert, destroy_ht(), Free, rw_lock_destroy, unlock, and write_lock.
| NETWORK_HTTP_INFO netw_extract_http_info | ( | char * | request | ) |
extract HTTP info from request
extract HTTP info from request
| request | the raw http request string |
Definition at line 6164 of file n_network.c.
References __n_assert, NETWORK_HTTP_INFO::body, NETWORK_HTTP_INFO::content_length, NETWORK_HTTP_INFO::content_type, LOG_ERR, n_log, netw_extract_http_request_type(), start(), and NETWORK_HTTP_INFO::type.
Referenced by handle_request().
| char * netw_extract_http_request_type | ( | const char * | request | ) |
extract HTTP request type
extract HTTP request type
| request | the raw http request |
Definition at line 6131 of file n_network.c.
References __n_assert.
Referenced by netw_extract_http_info().
| int netw_get_http_date | ( | char * | buffer, |
| size_t | buffer_size ) |
get current HTTP date string
get current HTTP date string
| buffer | the target buffer, must be big enough to hold the date |
| buffer_size | the size of the target buffer |
Definition at line 6865 of file n_network.c.
References __n_assert, LOG_ERR, and n_log.
Referenced by netw_build_http_response().
| const char * netw_get_http_status_message | ( | int | status_code | ) |
get HTTP status message string
get HTTP status message string
| status_code | the code to convert into a human-readable message |
Definition at line 6434 of file n_network.c.
Referenced by n_mock_server_run(), and netw_build_http_response().
Get a message from aimed NETWORK.
Instant return to NULL if no MSG
| netw | NETWORK where get the msg |
Definition at line 4410 of file n_network.c.
References __n_assert, g_netw_bytes_recv, list_shift, netw, and N_STR::written.
Referenced by manage_client(), netw_wait_msg(), poll_network_msgs(), and run_server().
| int netw_get_queue_status | ( | NETWORK * | netw, |
| size_t * | nb_to_send, | ||
| size_t * | nb_to_read ) |
get queue status
get queue status
| netw | NETWORK object |
| nb_to_send | Number of messages still in send buffer (not yet submitted to kernel) |
| nb_to_read | Number of message already read by the kernel, waiting in the local message list |
Definition at line 5748 of file n_network.c.
References __n_assert, and netw.
| int netw_get_state | ( | NETWORK * | netw, |
| uint32_t * | state, | ||
| int * | thr_engine_status ) |
Get flags from network.
Get flags from network.
| netw | The NETWORK *connection to query |
| state | pointer to network status storage , NETW_RUN , NETW_EXIT_ASKED , NETW_EXITED |
| thr_engine_status | pointer to network thread engine status storage ,NETW_THR_ENGINE_STARTED , NETW_THR_ENGINE_STOPPED |
Definition at line 3237 of file n_network.c.
References LOG_ERR, n_log, netw, and netw_atomic_read_state.
Referenced by main(), manage_client(), netw_close(), netw_stop_thr_engine(), and netw_wait_msg().
| int netw_get_url_from_http_request | ( | const char * | request, |
| char * | url, | ||
| size_t | size ) |
get URL from HTTP request
get URL from HTTP request
| request | raw http request to decode |
| url | pointer to an allocated char *holder |
| size | the size of the url holder |
Definition at line 6250 of file n_network.c.
References __n_assert.
Referenced by handle_request().
| const char * netw_guess_http_content_type | ( | const char * | url | ) |
guess HTTP content type from URL
guess HTTP content type from URL
| url | the url from which we want to guess the content type |
Definition at line 6370 of file n_network.c.
References __n_assert.
Referenced by handle_request().
| int netw_info_destroy | ( | NETWORK_HTTP_INFO | http_request | ) |
destroy HTTP info structure
destroy HTTP info structure
| http_request | the parsed NETWORK_HTTP_INFO request |
Definition at line 6237 of file n_network.c.
References NETWORK_HTTP_INFO::body, FreeNoLog, and NETWORK_HTTP_INFO::type.
Referenced by handle_request().
| int netw_init_openssl | ( | void | ) |
init ssl helper
init ssl helper
Initialize openssl
Definition at line 1335 of file n_network.c.
References netw_init_locks(), and OPENSSL_IS_INITIALIZED.
Referenced by main(), n_proxy_connect_tunnel_ssl(), netw_set_crypto(), netw_set_crypto_pem(), netw_ssl_server_ctx_new(), netw_ssl_server_handshake_ex(), and netw_ssl_start_client().
| int netw_init_wsa | ( | int | mode, |
| int | v1, | ||
| int | v2 ) |
Used by Init & Close network.
Used by Init & Close network.
Initialize winsock dll loading on windows if needed.
| mode | 1 for opening 0 for close 2 for status |
| v1 | First digit of version requested |
| v2 | Second digit of version requested |
Definition at line 841 of file n_network.c.
References mode.
Referenced by netw_accept_from_ex(), netw_adopt_client_fd(), netw_bind_udp(), netw_connect_ex_to(), netw_connect_nonblock(), netw_connect_udp(), and netw_make_listening().
| int netw_make_listening | ( | NETWORK ** | netw, |
| char * | addr, | ||
| char * | port, | ||
| int | nbpending, | ||
| int | ip_version ) |
Listening network.
The bind is EXCLUSIVE on every platform: a port another socket already holds is refused, never silently shared. SO_REUSEADDR (so a restarted listener can re-take the port it just released) is set on POSIX only, because on Windows that same option lets an unrelated process bind over a socket already holding the port and leaves which one receives a given connection undefined. Windows refuses the second bind by default, which is the wanted behaviour, so the option is not set there.
Listening network.
| netw | A NETWORK **network to make listening |
| addr | Address to bind, NULL for automatic address filling |
| port | For choosing a PORT to listen to |
| nbpending | Number of pending connection when listening |
| ip_version | NETWORK_IPALL for both ipv4 and ipv6 , NETWORK_IPV4 or NETWORK_IPV6 |
Definition at line 3602 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, addr, FreeNoLog, get_in_addr(), ip_version, LOG_ERR, Malloc, MAX_LIST_ITEMS, n_log, neterrno, netstrerror(), netw, netw_close(), netw_init_wsa(), netw_new(), NETW_RUN, NETW_SERVER, netw_set(), netw_setsockopt(), NETW_THR_ENGINE_STOPPED, NETWORK_IPV4, NETWORK_IPV6, and port.
Referenced by bind_free(), bind_free(), bind_free(), check_exclusive(), check_refused(), main(), main(), n_http_server_new(), n_mock_server_start(), run_server(), and server_thread().
| NETWORK_POOL * netw_new_pool | ( | size_t | nb_min_element | ) |
init pools
init pools
| nb_min_element | size of internal hash table for network pool |
Definition at line 5767 of file n_network.c.
References __n_assert, Free, init_lock, Malloc, new_ht(), NETWORK_POOL::pool, and NETWORK_POOL::rwlock.
Referenced by main().
| HASH_TABLE * netw_parse_post_data | ( | const char * | post_data | ) |
parse POST data into hash table
parse POST data into hash table
| post_data | the post data to parse |
Definition at line 6324 of file n_network.c.
References __n_assert, ht_put_string(), key, netw_urldecode(), and new_ht().
Referenced by handle_request().
| int netw_pool_add | ( | NETWORK_POOL * | netw_pool, |
| NETWORK * | netw ) |
add network to pool
add network to pool
| netw_pool | targeted network pool |
| netw | network to add |
Definition at line 5818 of file n_network.c.
References __n_assert, _netw_capture_error(), _nstr, free_nstr, ht_get_ptr(), ht_put_ptr(), key, list_push(), LOG_DEBUG, LOG_ERR, n_log, netw, netw_pool_netw_close(), nstrprintf, NETWORK_POOL::pool, NETWORK_POOL::rwlock, SOCKET_SIZE_FORMAT, unlock, and write_lock.
Referenced by main().
| int netw_pool_broadcast | ( | NETWORK_POOL * | netw_pool, |
| const NETWORK * | from, | ||
| N_STR * | net_msg ) |
broadcast message to pool
broadcast message to pool
| netw_pool | targeted network pool |
| from | source network |
| net_msg | mesage to broadcast |
Definition at line 5901 of file n_network.c.
References __n_assert, hash_val, ht_foreach, NETWORK::link, netw, netw_add_msg(), nstrdup(), NETWORK_POOL::pool, read_lock, NETWORK_POOL::rwlock, N_SOCKET::sock, and unlock.
Referenced by on_send_click(), and poll_network_msgs().
| size_t netw_pool_nbclients | ( | NETWORK_POOL * | netw_pool | ) |
get nb clients
get nb clients
| netw_pool | targeted network pool |
Definition at line 5925 of file n_network.c.
References __n_assert, HASH_TABLE::nb_keys, NETWORK_POOL::pool, read_lock, NETWORK_POOL::rwlock, and unlock.
Referenced by main().
| void netw_pool_netw_close | ( | void * | netw_ptr | ) |
close pool
close pool
| netw_ptr | NETWORK *network pointer |
Definition at line 5805 of file n_network.c.
References __n_assert, LOG_DEBUG, n_log, netw, and SOCKET_SIZE_FORMAT.
Referenced by netw_pool_add().
| int netw_pool_remove | ( | NETWORK_POOL * | netw_pool, |
| NETWORK * | netw ) |
remove network from pool
remove network from pool
| netw_pool | targeted network pool |
| netw | network to remove |
Definition at line 5864 of file n_network.c.
References __n_assert, _netw_capture_error(), _nstr, free_nstr, ht_remove(), key, list_search(), LOG_DEBUG, LOG_ERR, n_log, netw, nstrprintf, NETWORK_POOL::pool, remove_list_node, NETWORK_POOL::rwlock, SOCKET_SIZE_FORMAT, unlock, and write_lock.
Referenced by main(), and netw_close().
| void * netw_recv_func | ( | void * | NET | ) |
Thread Receiving management function.
Thread Receiving management function.
| NET | the NETWORK connection to use |
Definition at line 4716 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, N_STR::data, DONE, free_nstr, free_nstr_ptr(), N_STR::length, list_push(), LOG_DEBUG, LOG_ERR, Malloc, n_log, netw, netw_atomic_read_state, NETW_COMPRESSED_LZ4, NETW_COMPRESSED_ZLIB, NETW_ERROR, NETW_EXIT_ASKED, NETW_EXITED, NETW_MSG_MAX_FRAME_SIZE, netw_set(), NETW_SOCKET_DISCONNECTED, NETW_THR_EXIT_ERROR, NETW_THR_EXIT_OK, SOCKET_SIZE_FORMAT, unzip4_nstr(), unzip_nstr(), and N_STR::written.
Referenced by netw_start_thr_engine().
| void * netw_send_func | ( | void * | NET | ) |
Thread Sending management function.
Thread Sending management function.
| NET | the NETWORK connection to use, casted into (void*) |
Definition at line 4533 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, N_STR::data, DONE, Free, free_nstr, N_STR::length, list_shift, LOG_DEBUG, LOG_ERR, Malloc, n_log, netw, netw_atomic_read_state, NETW_COMPRESS_LZ4, NETW_COMPRESS_MIN_RATIO, NETW_COMPRESS_NONE, NETW_COMPRESS_THRESHOLD, NETW_COMPRESSED_LZ4, NETW_COMPRESSED_ZLIB, NETW_ERROR, NETW_EXIT_ASKED, NETW_EXITED, netw_set(), NETW_SOCKET_DISCONNECTED, NETW_THR_EXIT_ERROR, NETW_THR_EXIT_OK, SOCKET_SIZE_FORMAT, u_sleep(), N_STR::written, zip4_nstr(), and zip_nstr().
Referenced by netw_start_thr_engine().
send ident message
send ident message
| netw | The aimed NETWORK where we want to add something to send |
| type | type of identification ( NETW_IDENT_REQUEST , NETW_IDENT_NEW ) |
| id | The ID of the sending client |
| name | Username |
| passwd | Password |
Definition at line 5976 of file n_network.c.
References __n_assert, netmsg_make_ident(), netw, netw_add_msg(), and type().
| int netw_send_ping | ( | NETWORK * | netw, |
| int | type, | ||
| int | id_from, | ||
| int | id_to, | ||
| int | time ) |
send ping message
send ping message
| netw | The aimed NETWORK where we want to add something to send |
| id_from | Identifiant of the sender |
| id_to | Identifiant of the destination, -1 if the serveur itslef is targetted |
| time | The time it was when the ping was sended |
| type | NETW_PING_REQUEST or NETW_PING_REPLY |
Definition at line 5957 of file n_network.c.
References __n_assert, netmsg_make_ping(), netw, netw_add_msg(), and type().
| int netw_send_position | ( | NETWORK * | netw, |
| int | id, | ||
| double | X, | ||
| double | Y, | ||
| double | vx, | ||
| double | vy, | ||
| double | acc_x, | ||
| double | acc_y, | ||
| int | time_stamp ) |
send position message
send position message
| netw | The aimed NETWORK where we want to add something to send |
| id | The ID of the sending client |
| X | X position inside a big grid |
| Y | Y position inside a big grid |
| vx | X speed |
| vy | Y speed |
| acc_x | Y acceleration |
| acc_y | X acceleration |
| time_stamp | Current Time when sending (for some delta we would want to compute ) |
Definition at line 6000 of file n_network.c.
References __n_assert, netmsg_make_position_msg(), netw, and netw_add_msg().
| int netw_send_quit | ( | NETWORK * | netw | ) |
send quit message
send quit message
| netw | The aimed NETWORK |
Definition at line 6058 of file n_network.c.
References __n_assert, netmsg_make_quit_msg(), netw, and netw_add_msg().
| int netw_send_string_to | ( | NETWORK * | netw, |
| int | id_to, | ||
| N_STR * | name, | ||
| N_STR * | chan, | ||
| N_STR * | txt, | ||
| int | color ) |
send string to a specific target
send string to a specific target
| netw | The aimed NETWORK where we want to add something to send |
| id_to | The ID of the targetted client |
| name | Sender Name |
| chan | channel to use |
| txt | Sender text |
| color | Sender text color |
Definition at line 6022 of file n_network.c.
References __n_assert, netmsg_make_string_msg(), netw, and netw_add_msg().
send string to all targets
send string to all targets
| netw | The aimed NETWORK where we want to add something to send |
| name | Name of user |
| chan | Target Channel, if any. Pass "ALL" to target the default channel |
| txt | The text to send |
| color | The color of the text |
Definition at line 6042 of file n_network.c.
References __n_assert, netmsg_make_string_msg(), netw, and netw_add_msg().
| int netw_set | ( | NETWORK * | netw, |
| int | flag ) |
Set flags on network.
Set flags on network.
| netw | The NETWORK *connection to modify |
| flag | NETW_EMPTY_SENDBUF, NETW_EMPTY_RECVBUF, NETW_RUN , NETW_EXIT_ASKED , NETW_EXITED |
Definition at line 3259 of file n_network.c.
References __n_assert, list_destroy(), list_empty(), netw, netw_atomic_write_state, NETW_CLIENT, NETW_DESTROY_RECVBUF, NETW_DESTROY_SENDBUF, NETW_EMPTY_RECVBUF, NETW_EMPTY_SENDBUF, NETW_ERROR, NETW_EXIT_ASKED, NETW_EXITED, NETW_RUN, NETW_SERVER, NETW_THR_ENGINE_STARTED, and NETW_THR_ENGINE_STOPPED.
Referenced by netw_accept_from_ex(), netw_adopt_client_fd(), netw_bind_udp(), netw_close(), netw_connect_check(), netw_connect_ex_to(), netw_connect_udp(), netw_make_listening(), netw_recv_func(), netw_send_func(), netw_start_thr_engine(), and netw_stop_thr_engine().
| int netw_set_blocking | ( | NETWORK * | netw, |
| unsigned long int | is_blocking ) |
set blocking mode
set blocking mode
| netw | The network to configure |
| is_blocking | 0 NON BLOCk , 1 BLOCK |
Definition at line 911 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, and netw_close().
Referenced by _netw_start_nonblock_connect(), _netw_timed_connect(), _worker(), main(), netw_accept_from_ex(), netw_ssl_handshake_once(), and netw_ssl_server_handshake_once().
| int netw_set_compression_mode | ( | NETWORK * | netw, |
| int | mode ) |
Pick send-side compression algorithm for this NETWORK: NETW_COMPRESS_NONE, _ZLIB, _LZ4.
Independent of the inbound decode path, which always honours whichever flag the sender set.
Pick send-side compression algorithm for this NETWORK: NETW_COMPRESS_NONE, _ZLIB, _LZ4.
| netw | The network to configure (must be non-NULL). |
| mode | One of NETW_COMPRESS_NONE / NETW_COMPRESS_ZLIB / NETW_COMPRESS_LZ4. Invalid values are rejected. |
Affects outbound packets only. The recv path honours whichever NETW_COMPRESSED_* flag the sender set, so two peers running different modes still interoperate.
Definition at line 893 of file n_network.c.
References __n_assert, LOG_ERR, mode, n_log, netw, NETW_COMPRESS_LZ4, NETW_COMPRESS_NONE, and NETW_COMPRESS_ZLIB.
| void netw_set_connect_abort_cb | ( | int(* | cb )(void *ctx), |
| void * | ctx ) |
register a process-wide callback polled during connect; non-zero aborts the in-progress connect (NULL removes)
register a process-wide callback polled during connect; non-zero aborts the in-progress connect (NULL removes)
When set, netw_connect_ex_to (and every _to / SSL connect variant built on it) wakes every NETW_CONNECT_ABORT_POLL_MS during the connect wait and calls cb; if it returns non-zero the connect is abandoned at once (the connect call returns FALSE) instead of blocking until connect_timeout_ms. This lets an application interrupt a connect to an unresponsive host (a dropped SYN) the way shutdown() already interrupts a blocking read on a connected socket. The callback must be quick and non-blocking. Pass cb = NULL to remove it. The pointer is a single process-global; set it once at startup before concurrent connects (it is read without a lock).
| cb | Callback returning non-zero to abort the in-progress connect, or NULL. |
| ctx | Opaque pointer handed back to cb on each poll. |
Definition at line 2539 of file n_network.c.
References _netw_connect_abort_cb, and _netw_connect_abort_ctx.
Referenced by main().
| int netw_set_crypto | ( | NETWORK * | netw, |
| char * | key, | ||
| char * | certificate ) |
set SSL
set SSL
| netw | the NETWORK instance to configure |
| key | path to the key file |
| certificate | path to the certificate file |
Definition at line 1489 of file n_network.c.
References __n_assert, _netw_crypto_setup_failed(), _netw_ssl_server_defaults(), FreeNoLog, key, LOG_ERR, n_log, netw, NETW_ENCRYPT_OPENSSL, netw_init_openssl(), netw_ssl_print_errors(), recv_ssl_data(), recv_ssl_data_once(), send_ssl_data(), and send_ssl_data_once().
Referenced by main(), netw_connect_ex_to(), and netw_set_crypto_chain().
| int netw_set_crypto_chain | ( | NETWORK * | netw, |
| char * | key, | ||
| char * | certificate, | ||
| char * | ca_file ) |
set SSL certificate chain from PEM file
set SSL certificate chain from PEM file
| netw | the NETWORK to configure |
| key | path to the key file |
| certificate | path to the certificate file |
| ca_file | path to the CA certificate file for chain verification |
Definition at line 1704 of file n_network.c.
References __n_assert, ca_file, key, LOG_ERR, n_log, netw, netw_set_crypto(), and netw_ssl_print_errors().
Referenced by main().
| int netw_set_crypto_chain_pem | ( | NETWORK * | netw, |
| const char * | key_pem, | ||
| const char * | cert_pem, | ||
| const char * | ca_pem ) |
set SSL certificate chain from PEM strings in memory
set SSL certificate chain from PEM strings in memory
| netw | the NETWORK to configure |
| key_pem | PEM-formatted private key string |
| cert_pem | PEM-formatted certificate string |
| ca_pem | PEM-formatted CA certificate string for verification |
Definition at line 1739 of file n_network.c.
References __n_assert, LOG_ERR, n_log, netw, and netw_set_crypto_pem().
| int netw_set_crypto_pem | ( | NETWORK * | netw, |
| const char * | key_pem, | ||
| const char * | cert_pem ) |
set SSL from PEM strings in memory
set SSL from PEM strings in memory
| netw | the NETWORK to configure |
| key_pem | PEM-formatted private key string |
| cert_pem | PEM-formatted certificate string |
Definition at line 1597 of file n_network.c.
References __n_assert, _netw_crypto_setup_failed(), _netw_ssl_server_defaults(), cert, LOG_ERR, n_log, netw, NETW_ENCRYPT_OPENSSL, netw_init_openssl(), netw_ssl_print_errors(), recv_ssl_data(), recv_ssl_data_once(), send_ssl_data(), and send_ssl_data_once().
Referenced by netw_set_crypto_chain_pem().
install an in-memory cert/key on THIS connection's SSL only (per-connection, unlike the context-wide netw_set_crypto_pem)
install an in-memory cert/key on THIS connection's SSL only (per-connection, unlike the context-wide netw_set_crypto_pem)
| netw | the accepted NETWORK (must already hold an SSL handle) |
| key_pem | the private key PEM |
| cert_pem | the certificate PEM |
Definition at line 1853 of file n_network.c.
References __n_assert, _ssl_use_pem(), N_STR::data, netw, and netw_ssl_print_errors().
| int netw_set_user_id | ( | NETWORK * | netw, |
| int | id ) |
set user id on a netw
set user id on a netw
| netw | targeted network |
| id | id we want to associated with |
Definition at line 5942 of file n_network.c.
References __n_assert, and netw.
| int netw_setsockopt | ( | NETWORK * | netw, |
| int | optname, | ||
| int | value ) |
Set common socket options (disable naggle, send/recv buf, reuse addr).
Set common socket options (disable naggle, send/recv buf, reuse addr).
| netw | The socket to configure |
| optname | NETWORK_DEPLETE_SOCKET_TIMEOUT,NETWORK_DEPLETE_QUEUES_TIMEOUT,NETWORK_WAIT_CLOSE_TIMEOUT,NETWORK_CONSECUTIVE_SEND_WAIT ,SO_REUSEADDR,SO_REUSEPORT,SO_KEEPALIVE,TCP_NODELAY,SO_SNDBUF,SO_RCVBUF,SO_LINGER,SO_RCVTIMEO,SO_SNDTIMEO,TCP_USER_TIMEOUT. Please refer to man setsockopt for details |
| value | The value of the socket parameter |
Definition at line 969 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, FreeNoLog, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETWORK_CONSECUTIVE_SEND_WAIT, NETWORK_DEPLETE_QUEUES_TIMEOUT, NETWORK_DEPLETE_SOCKET_TIMEOUT, NETWORK_WAIT_CLOSE_TIMEOUT, and SOCKET_SIZE_FORMAT.
Referenced by cl_connect(), main(), netw_accept_from_ex(), netw_bind_udp(), and netw_make_listening().
| int netw_ssl_connect | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| int | ip_version, | ||
| char * | ssl_key_file, | ||
| char * | ssl_cert_file ) |
connect ssl helper
connect ssl helper
| netw | a NETWORK *object |
| host | Host or IP to connect to |
| port | Port to use to connect |
| ip_version | NETWORK_IPALL for both ipv4 and ipv6 , NETWORK_IPV4 or NETWORK_IPV6 |
| ssl_key_file | NULL or the path to the SSL key file to use. If set, a ssl_cert_file must also be provided |
| ssl_cert_file | NULL or the path to the SSL certificate file to use. If set, a ssl_key_file must also be provided |
Definition at line 2928 of file n_network.c.
References _str, ip_version, LOG_INFO, MAX_LIST_ITEMS, n_log, netw, netw_connect_ex(), and port.
| int netw_ssl_connect_client | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| int | ip_version ) |
connect as SSL client without client certificate (TCP + SSL_CTX, no handshake yet)
connect as SSL client without client certificate (TCP + SSL_CTX, no handshake yet)
Equivalent to netw_ssl_connect_client_to with no connect timeout (the OS decides when the TCP connect gives up). See netw_ssl_connect_client_to.
| netw | output: new NETWORK (must be NULL on entry) |
| host | hostname to connect to |
| port | port string |
| ip_version | NETWORK_IPALL, NETWORK_IPV4, or NETWORK_IPV6 |
Definition at line 3020 of file n_network.c.
References ip_version, netw, netw_ssl_connect_client_to(), and port.
Referenced by n_sse_connect(), and n_ws_connect().
| int netw_ssl_connect_client_to | ( | NETWORK ** | netw, |
| char * | host, | ||
| char * | port, | ||
| int | ip_version, | ||
| int | connect_timeout_ms ) |
like netw_ssl_connect_client but bounds the TCP connect by connect_timeout_ms (0 = OS default)
like netw_ssl_connect_client but bounds the TCP connect by connect_timeout_ms (0 = OS default)
Performs TCP connect, creates an SSL_CTX with TLS_client_method and loads default system verify paths. Does NOT perform the SSL handshake. Call netw_ssl_set_ca / netw_ssl_set_verify to configure verification, then netw_ssl_do_handshake to complete the connection.
| netw | output: new NETWORK (must be NULL on entry) |
| host | hostname to connect to |
| port | port string |
| ip_version | NETWORK_IPALL, NETWORK_IPV4, or NETWORK_IPV6 |
| connect_timeout_ms | connect timeout in milliseconds, 0 = OS default |
Definition at line 2948 of file n_network.c.
References __n_assert, ip_version, MAX_LIST_ITEMS, netw, netw_close(), netw_connect_ex_to(), netw_ssl_start_client(), and port.
Referenced by client_connect(), main(), netw_ssl_connect_client(), and try_connect().
| int netw_ssl_do_handshake | ( | NETWORK * | netw, |
| const char * | sni_hostname ) |
complete the SSL handshake on a NETWORK whose ctx was already created.
sni_hostname is used for BOTH halves of the identity: it is sent as SNI (so the server picks the right certificate) and set as the name the peer certificate must carry. Without the second half, SSL_VERIFY_PEER checks the chain and nothing else, so any certificate chaining to a trusted root is accepted for any host. An IP literal is matched against the certificate's IP entries, a name against its subjectAltName / CN, and a partial wildcard (w*.example.com) is refused.
With verification on (netw_ssl_set_verify), a mismatch fails the handshake. With it off, the handshake completes and the mismatch is reported by netw_ssl_get_verify_result(), so a caller that deliberately does not verify keeps its previous behaviour. Pass NULL to skip both halves.
complete the SSL handshake on a NETWORK whose ctx was already created.
The NETWORK must have a valid SSL_CTX (from netw_ssl_connect_client or netw_set_crypto). Optionally sets the SNI hostname for virtual hosting support.
| netw | connected NETWORK with ctx set |
| sni_hostname | hostname for SNI extension, or NULL to skip |
Definition at line 3057 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, LOG_DEBUG, LOG_ERR, n_log, netw, netw_is_ip_literal(), netw_ssl_print_errors(), SSL_set1_host(), and SSL_set_hostflags().
Referenced by client_connect(), main(), n_sse_connect(), n_ws_connect(), and try_connect().
| int netw_ssl_get_alpn | ( | NETWORK * | netw, |
| char * | out, | ||
| size_t | out_len ) |
get the ALPN protocol the completed handshake selected, on either side of the connection
get the ALPN protocol the completed handshake selected, on either side of the connection
Works on either side of the connection: the client reads what the server chose from its offer, the server reads what it answered.
| netw | the handshaked NETWORK |
| out | buffer receiving the NUL-terminated protocol name |
| out_len | capacity of out |
Definition at line 1964 of file n_network.c.
References __n_assert, and netw.
Referenced by client_connect(), main(), and server_fn().
| const char * netw_ssl_get_sni | ( | NETWORK * | netw | ) |
get the SNI server_name the peer requested in its ClientHello, or NULL
get the SNI server_name the peer requested in its ClientHello, or NULL
| netw | the accepted NETWORK |
Definition at line 1839 of file n_network.c.
References __n_assert, and netw.
| int netw_ssl_get_verify_result | ( | NETWORK * | netw, |
| const char * | expected_host, | ||
| char * | errbuf, | ||
| size_t | errsz ) |
evaluate the peer certificate (chain trust + host match) against the system trust store, independently of the connection verify mode
evaluate the peer certificate (chain trust + host match) against the system trust store, independently of the connection verify mode
Verifies the peer certificate chain against the system default trust store and checks that expected_host matches the certificate, independently of the verify mode the handshake ran with. This lets a connection complete with verification disabled (for example an intercepting proxy that must see the traffic regardless) while still reporting whether the real peer certificate would have been trusted.
| netw | a NETWORK with a completed client handshake (netw->ssl set) |
| expected_host | hostname to match against the certificate, or NULL to skip |
| errbuf | optional buffer that receives a short reason on failure |
| errsz | size of errbuf |
Definition at line 2288 of file n_network.c.
References __n_assert, cert, netw, and SSL_get1_peer_certificate.
Referenced by main(), and try_connect().
| int netw_ssl_handshake_once | ( | NETWORK * | netw, |
| const char * | sni_hostname ) |
non-blocking (resumable) TLS client handshake: TRUE done, NETW_IO_WANT_READ/WRITE to retry, FALSE on error
non-blocking (resumable) TLS client handshake: TRUE done, NETW_IO_WANT_READ/WRITE to retry, FALSE on error
The single-attempt counterpart of netw_ssl_do_handshake, for a caller that drives its own poll()/select() loop instead of the thread engine. Requires a client SSL context already set up on netw (e.g. by netw_ssl_start_client, plus any netw_ssl_set_verify / netw_ssl_set_versions). On the first call it creates the SSL object in connect state, binds the socket, applies SNI, and switches the socket to non-blocking; every call then advances the handshake one step.
| netw | a connected NETWORK carrying a client SSL context (netw->ctx) |
| sni_hostname | optional SNI server name, or NULL |
Definition at line 3159 of file n_network.c.
References __n_assert, _netw_capture_error(), _netw_ssl_handshake_step(), LOG_ERR, n_log, netw, netw_set_blocking(), and netw_ssl_print_errors().
Referenced by drive_handshake().
| SSL_CTX * netw_ssl_server_ctx_new | ( | const char * | key_file, |
| const char * | cert_chain_file ) |
new standalone server SSL_CTX with the library's secure defaults (TLS 1.2+, forward-secret AEAD, no compression / renegotiation / tickets), the certificate chain and key loaded from PEM files and checked to match.
For a server that runs its own handshakes (n_http_server); free with SSL_CTX_free().
new standalone server SSL_CTX with the library's secure defaults (TLS 1.2+, forward-secret AEAD, no compression / renegotiation / tickets), the certificate chain and key loaded from PEM files and checked to match.
The certificate file may hold the whole chain (leaf first). The key must match the certificate. For a server that runs its own (non-blocking) handshakes on accepted sockets instead of netw_accept_from_ex().
| key_file | path to the PEM private key |
| cert_chain_file | path to the PEM certificate chain |
Definition at line 1449 of file n_network.c.
References __n_assert, _netw_ssl_server_defaults(), LOG_ERR, n_log, netw_init_openssl(), and netw_ssl_print_errors().
Referenced by n_http_server_new().
| int netw_ssl_server_handshake | ( | NETWORK * | netw, |
| netw_sni_pick_cb | pick, | ||
| void * | user_data ) |
upgrade an already-accepted plaintext connection to a TLS server, selecting the cert per client SNI via pick() during the handshake (for proxy CONNECT)
upgrade an already-accepted plaintext connection to a TLS server, selecting the cert per client SNI via pick() during the handshake (for proxy CONNECT)
Sets up a per-connection SSL server context with no default certificate plus an OpenSSL servername callback, then performs SSL_accept on the socket. The callback runs synchronously inside SSL_accept and asks pick() for a certificate matching the requested host, so the handshake completes with a host-specific leaf. Use this when the socket was accepted in the clear first (for example after a proxy CONNECT) and must then become a TLS server.
| netw | an already-accepted plaintext NETWORK |
| pick | callback that supplies a cert/key for a given SNI host |
| user_data | opaque pointer passed to pick |
Definition at line 2023 of file n_network.c.
References netw, and netw_ssl_server_handshake_ex().
Referenced by netw_accept_ssl_with_sni_cb().
| int netw_ssl_server_handshake_ex | ( | NETWORK * | netw, |
| netw_sni_pick_cb | pick, | ||
| void * | user_data, | ||
| const char *const * | alpn, | ||
| size_t | alpn_count ) |
same, plus an ALPN offer: the first protocol of alpn the client also offered is selected (none when the two lists do not overlap)
same, plus an ALPN offer: the first protocol of alpn the client also offered is selected (none when the two lists do not overlap)
Same as netw_ssl_server_handshake(), plus an ALPN offer: the first protocol of alpn that the client also offered is selected, and no ALPN is answered when the two lists do not overlap (the handshake still succeeds, and the peer falls back to whatever it does without ALPN). Read the outcome with netw_ssl_get_alpn(). An intercepting proxy needs this on its client leg: with no ALPN offered, a browser that would have spoken HTTP/2 to the origin speaks HTTP/1.1 to the proxy instead, and the proxy never sees the requests only HTTP/2 can express.
| netw | an already-accepted plaintext NETWORK |
| pick | callback that supplies a cert/key for a given SNI host |
| user_data | opaque pointer passed to pick |
| alpn | the protocols we accept in server preference order, or NULL for none |
| alpn_count | how many protocols, 0 for none |
Definition at line 2047 of file n_network.c.
References __n_assert, _netw_alpn_select_cb(), _netw_sni_servername_cb(), _netw_ssl_server_defaults(), NETW_SNI_ARG::alpn, NETW_SNI_ARG::alpn_count, netw, NETW_ENCRYPT_OPENSSL, netw_init_openssl(), netw_ssl_print_errors(), NETW_SNI_ARG::pick, recv_ssl_data(), recv_ssl_data_once(), send_ssl_data(), send_ssl_data_once(), and NETW_SNI_ARG::user_data.
Referenced by main(), netw_ssl_server_handshake(), and server_fn().
| int netw_ssl_server_handshake_once | ( | NETWORK * | netw, |
| SSL_CTX * | ctx ) |
non-blocking (resumable) TLS server handshake against a caller-owned shared ctx: TRUE done, NETW_IO_WANT_READ/WRITE to retry, FALSE on error
non-blocking (resumable) TLS server handshake against a caller-owned shared ctx: TRUE done, NETW_IO_WANT_READ/WRITE to retry, FALSE on error
The single-attempt counterpart of netw_ssl_server_handshake, for a single-cert server that drives its own poll()/select() loop. Unlike netw_ssl_server_handshake_ex it does NOT create an SSL_CTX or require an SNI pick callback: the caller owns ctx (certificate/key, TLS versions, ...) once and passes it for every accepted connection, typically a NETWORK returned by netw_accept_nonblock_from. On the first call it creates the SSL object from ctx in accept state, binds the socket, installs the SSL send/recv movers, and switches the socket to non-blocking; every call then advances the handshake one step.
The accepted NETWORK keeps netw->ctx == NULL (it borrows ctx, per the accepted-connection convention), so netw_close() frees the SSL object but never the shared context – the caller frees ctx once, after the last connection.
| netw | an accepted NETWORK (e.g. from netw_accept_nonblock_from) |
| ctx | the caller-owned server SSL context, shared across connections |
Definition at line 3202 of file n_network.c.
References __n_assert, _netw_capture_error(), _netw_ssl_handshake_step(), LOG_ERR, n_log, netw, NETW_ENCRYPT_OPENSSL, netw_set_blocking(), netw_ssl_print_errors(), recv_ssl_data(), recv_ssl_data_once(), send_ssl_data(), and send_ssl_data_once().
Referenced by drive_handshake().
| int netw_ssl_set_alpn | ( | NETWORK * | netw, |
| const char *const * | protos, | ||
| size_t | count ) |
offer an ALPN protocol list on a TLS client connection, before its handshake
A client that advertises no ALPN is answered with HTTP/1.1 by every modern server, so a proxy or a fetcher that never offers it silently downgrades every connection it makes.
| netw | the NETWORK, with its client SSL_CTX started and its handshake not yet done |
| protos | the protocol names in client preference order, for example "h2" then "http/1.1" |
| count | how many protocols |
Definition at line 1934 of file n_network.c.
References __n_assert, _netw_alpn_encode(), LOG_ERR, n_log, and netw.
Referenced by client_connect(), and main().
| int netw_ssl_set_ca | ( | NETWORK * | netw, |
| const char * | ca_file, | ||
| const char * | ca_path ) |
set custom CA verify path or file
set custom CA verify path or file
| netw | the NETWORK to configure |
| ca_file | path to a CA certificate file, or NULL |
| ca_path | path to a directory of CA certificates, or NULL |
Definition at line 2137 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, ca_file, LOG_ERR, n_log, netw, and netw_ssl_print_errors().
Referenced by try_connect().
| int netw_ssl_set_ciphers | ( | NETWORK * | netw, |
| const char * | cipher_list, | ||
| const char * | ciphersuites ) |
set the TLS<=1.2 cipher list and/or the TLS1.3 ciphersuites (NULL leaves a default).
The ciphersuites are ignored when NETW_HAVE_TLS13 is 0
set the TLS<=1.2 cipher list and/or the TLS1.3 ciphersuites (NULL leaves a default).
The two are separate knobs in OpenSSL and setting only one silently leaves the other at its default, which is how "I restricted the ciphers" turns into a handshake that used something else entirely. Both are exposed here so a caller can be explicit.
Below OpenSSL 1.1.1 there is no TLS 1.3 to configure, so ciphersuites is logged and ignored while cipher_list still applies; NETW_HAVE_TLS13 tells a caller which of the two it got.
| netw | the network whose SSL context to configure |
| cipher_list | OpenSSL cipher-list string for TLS <= 1.2, or NULL to leave the default |
| ciphersuites | OpenSSL ciphersuite string for TLS 1.3, or NULL to leave the default |
Definition at line 2244 of file n_network.c.
References __n_assert, LOG_DEBUG, LOG_ERR, n_log, and netw.
Referenced by main().
| int netw_ssl_set_client_cert | ( | NETWORK * | netw, |
| const char * | cert_file, | ||
| const char * | key_file ) |
load client certificate and private key for mTLS
load client certificate and private key for mTLS
| netw | the NETWORK to configure |
| cert_file | path to the client certificate file (PEM) |
| key_file | path to the client private key file (PEM), or NULL to use cert_file |
Definition at line 2355 of file n_network.c.
References __n_assert, _netw_capture_error(), LOG_ERR, n_log, netw, and netw_ssl_print_errors().
| int netw_ssl_set_verify | ( | NETWORK * | netw, |
| int | enable ) |
enable or disable peer certificate verification
enable or disable peer certificate verification
| netw | the NETWORK to configure |
| enable | 1 to enable verification, 0 to disable |
Definition at line 2162 of file n_network.c.
References __n_assert, LOG_ERR, n_log, and netw.
Referenced by client_connect(), main(), main(), and try_connect().
| int netw_ssl_set_versions | ( | NETWORK * | netw, |
| int | min_version, | ||
| int | max_version ) |
set the minimum/maximum TLS protocol version on the connection's SSL context (0 leaves a default).
Pass NETW_TLS_MAX_VERSION rather than TLS1_3_VERSION to stay buildable on OpenSSL 1.0.2
set the minimum/maximum TLS protocol version on the connection's SSL context (0 leaves a default).
A security tool has to be able to say which TLS versions it will speak. Testing whether a host still accepts TLS 1.0, or forcing 1.2 to reproduce a finding, is not possible when the library always negotiates whatever OpenSSL's defaults allow. Call before the handshake; after it, the versions are already agreed and this has no effect.
Below OpenSSL 1.1.0 there is no version-flexible context to bound: the ctx is pinned to TLS 1.2, so a range containing TLS 1.2 is accepted and any other range is refused. Use NETW_TLS_MAX_VERSION rather than naming TLS1_3_VERSION, which does not exist below OpenSSL 1.1.1.
| netw | the network whose SSL context to configure |
| min_version | minimum version as an OpenSSL TLS*_VERSION constant, or 0 to leave the default |
| max_version | maximum version likewise, or 0 to leave the default |
Definition at line 2194 of file n_network.c.
References __n_assert, LOG_ERR, n_log, and netw.
Referenced by main().
| int netw_ssl_start_client | ( | NETWORK * | netw | ) |
set up a client SSL_CTX on an already-connected NETWORK (no handshake yet)
set up a client SSL_CTX on an already-connected NETWORK (no handshake yet)
Performs the SSL-context half of netw_ssl_connect_client_to on a NETWORK whose TCP connection is already established (for example one returned by netw_adopt_client_fd after an HTTP CONNECT proxy tunnel): it creates an SSL_CTX with TLS_client_method, loads the default system verify paths, and switches the NETWORK send/recv vtable to the SSL variants. It does NOT perform the handshake. Call netw_ssl_set_ca / netw_ssl_set_verify to configure verification, then netw_ssl_do_handshake to complete the connection. On failure the NETWORK is left untouched (the caller owns it and is responsible for netw_close).
| netw | connected NETWORK to promote to SSL. Must not be NULL. |
Definition at line 2977 of file n_network.c.
References __n_assert, netw, NETW_ENCRYPT_OPENSSL, netw_init_openssl(), netw_ssl_print_errors(), recv_ssl_data(), recv_ssl_data_once(), send_ssl_data(), and send_ssl_data_once().
Referenced by main(), and netw_ssl_connect_client_to().
| int netw_start_thr_engine | ( | NETWORK * | netw | ) |
Create the sending and receiving thread of a NETWORK.
Create the sending and receiving thread of a NETWORK.
Create a sending & receiving thread.
| netw | The aimed NETWORK connection to start receiving data |
Definition at line 4484 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, LOG_ERR, n_log, netw, NETW_EXIT_ASKED, netw_recv_func(), netw_send_func(), netw_set(), and NETW_THR_ENGINE_STARTED.
Referenced by client_worker_echo(), handle_client(), main(), manage_client(), and run_client().
| int netw_stop_thr_engine | ( | NETWORK * | netw | ) |
Stop a NETWORK connection sending and receiving thread.
Stop a NETWORK connection sending and receiving thread.
| netw | The aimed NETWORK conection to stop |
Definition at line 4893 of file n_network.c.
References __n_assert, _netw_capture_error(), LOG_DEBUG, LOG_ERR, n_log, netw, NETW_EXIT_ASKED, NETW_EXITED, netw_get_state(), netw_set(), NETW_THR_ENGINE_STARTED, NETW_THR_ENGINE_STOPPED, and SOCKET_SIZE_FORMAT.
Referenced by netw_close().
| ssize_t netw_udp_recvfrom | ( | NETWORK * | netw, |
| char * | buf, | ||
| uint32_t | n, | ||
| struct sockaddr * | src_addr, | ||
| socklen_t * | src_len ) |
UDP recvfrom with source address capture.
UDP recvfrom with source address capture.
| netw | NETWORK to use for receiving |
| buf | pointer to buffer |
| n | max number of bytes to receive |
| src_addr | pointer to store source address (can be NULL) |
| src_len | pointer to length of src_addr (can be NULL) |
Definition at line 4070 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, FreeNoLog, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_SOCKET_ERROR, and SOCKET_SIZE_FORMAT.
Referenced by main(), and run_server().
| ssize_t netw_udp_sendto | ( | NETWORK * | netw, |
| char * | buf, | ||
| uint32_t | n, | ||
| struct sockaddr * | dest_addr, | ||
| socklen_t | dest_len ) |
UDP sendto with explicit destination.
UDP sendto with explicit destination.
| netw | NETWORK to use for sending |
| buf | pointer to buffer |
| n | number of bytes to send |
| dest_addr | destination sockaddr |
| dest_len | length of dest_addr |
Definition at line 4038 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, FreeNoLog, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_SOCKET_ERROR, and SOCKET_SIZE_FORMAT.
Referenced by main(), and run_server().
| int netw_unload_openssl | ( | void | ) |
unload ssl helper
unload ssl helper
Initialize openssl
Definition at line 1368 of file n_network.c.
References netw_kill_locks(), and OPENSSL_IS_INITIALIZED.
Referenced by main(), and main().
| char * netw_urldecode | ( | const char * | str | ) |
URL-decode a string.
URL-decode a string.
| str | input string to decode |
Definition at line 6287 of file n_network.c.
References __n_assert, Free, LOG_ERR, and n_log.
Referenced by netw_parse_post_data().
| char * netw_urlencode | ( | const char * | str, |
| size_t | len ) |
URL-encode a string.
URL-encode a string.
| str | input string |
| len | input string length |
Definition at line 6098 of file n_network.c.
References __n_assert, and netw_calculate_urlencoded_size().
| int netw_wait_close_timed | ( | NETWORK ** | netw, |
| size_t | timeout ) |
Closing for peer with timeout.
References addr, ip_version, netw, port, and type().
Wait a message from aimed NETWORK.
Recheck each 'refresh' usec until 'timeout' usec
Recheck each usec until a valid
| netw | The link on which we wait a message |
| refresh | The time in usec between each check until there is a message |
| timeout | in usecs , maximum amount of time to wait before return. 0 to disable. |
Definition at line 4432 of file n_network.c.
References __n_assert, _netw_capture_error(), LOG_DEBUG, LOG_ERR, N_ENUM_ENTRY, n_log, netw, NETW_ERROR, NETW_EXITED, netw_get_msg(), netw_get_state(), NETW_RUN, SOCKET_SIZE_FORMAT, and u_sleep().
Referenced by client_worker_echo(), handle_client(), main(), and run_client().
| size_t ntohst | ( | size_t | value | ) |
network to host size_t
| value | the size_t value to convert to host order |
Definition at line 162 of file n_network.c.
| ssize_t recv_data | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
Reading from a socket.
Reading from a socket.
| netw | connected NETWORK |
| buf | pointer to buffer |
| n | number of characters we want |
Definition at line 4994 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_CALL_RETRY, NETW_MAX_RETRIES, NETW_SOCKET_DISCONNECTED, NETW_SOCKET_ERROR, and SOCKET_SIZE_FORMAT.
Referenced by netw_new().
| ssize_t recv_data_once | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
Single-attempt read (see NETWORK.recv_data_once contract).
Single-attempt read (see NETWORK.recv_data_once contract).
| netw | the NETWORK to use |
| buf | pointer to buffer |
| n | max number of bytes to read (> 0) |
Definition at line 5117 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_IO_WANT_READ, NETW_SOCKET_DISCONNECTED, NETW_SOCKET_ERROR, and SOCKET_SIZE_FORMAT.
Referenced by netw_new().
| ssize_t recv_php | ( | SOCKET | s, |
| int * | _code, | ||
| char ** | buf ) |
receive from php
receive from php
| s | connected socket |
| _code | pointer to store the code |
| buf | pointer to buffer |
Definition at line 5643 of file n_network.c.
References _str, Free, FreeNoLog, HEAD_CODE, HEAD_SIZE, LOG_ERR, Malloc, n_log, neterrno, netstrerror(), and SOCKET_SIZE_FORMAT.
| ssize_t recv_ssl_data | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
SSL Reading from a socket.
SSL Reading from a socket.
| netw | connected NETWORK |
| buf | pointer to buffer |
| n | number of characters we want |
Definition at line 5270 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_SOCKET_DISCONNECTED, NETW_SOCKET_ERROR, and u_sleep().
Referenced by main(), netw_accept_from_ex(), netw_set_crypto(), netw_set_crypto_pem(), netw_ssl_server_handshake_ex(), netw_ssl_server_handshake_once(), netw_ssl_start_client(), and server_fn().
| ssize_t recv_ssl_data_once | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
SSL single-attempt read (see recv_data_once contract).
SSL single-attempt read (see recv_data_once contract).
The caller must loop until NETW_IO_WANT_READ, SSL_read drains its internal plaintext buffer before reporting WANT_READ, so loop-until-WANT_READ also covers the SSL_pending() case that otherwise stalls TLS over edge-triggered epoll.
| netw | the NETWORK to use (crypto must be active) |
| buf | pointer to buffer |
| n | max number of bytes to read (> 0) |
Definition at line 5476 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_IO_WANT_READ, NETW_IO_WANT_WRITE, NETW_SOCKET_DISCONNECTED, and NETW_SOCKET_ERROR.
Referenced by io_full(), main(), netw_accept_from_ex(), netw_set_crypto(), netw_set_crypto_pem(), netw_ssl_server_handshake_ex(), netw_ssl_server_handshake_once(), and netw_ssl_start_client().
| ssize_t recv_udp_data | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
UDP recv data from socket.
UDP recv data from socket.
| netw | connected NETWORK |
| buf | pointer to buffer |
| n | max number of bytes to receive |
Definition at line 4002 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_SOCKET_ERROR, and SOCKET_SIZE_FORMAT.
Referenced by main(), netw_bind_udp(), netw_connect_udp(), and run_client().
| ssize_t send_data | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
Writing to a socket.
Writing to a socket.
| netw | connected NETWORK |
| buf | pointer to buffer |
| n | number of characters we want to send |
Definition at line 4933 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_CALL_RETRY, NETW_MAX_RETRIES, NETW_SOCKET_DISCONNECTED, NETW_SOCKET_ERROR, and SOCKET_SIZE_FORMAT.
Referenced by netw_new(), and send_hostile_header().
| ssize_t send_data_once | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
Single-attempt write (see NETWORK.send_data_once contract).
Single-attempt write (see NETWORK.send_data_once contract).
One transport attempt, no loop-until-complete, no retry storm: partial writes are the caller's state machine to handle.
| netw | the NETWORK to use |
| buf | pointer to buffer |
| n | number of bytes to try to send (> 0) |
Definition at line 5061 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_IO_WANT_WRITE, NETW_SOCKET_DISCONNECTED, NETW_SOCKET_ERROR, and SOCKET_SIZE_FORMAT.
Referenced by netw_new().
| ssize_t send_php | ( | SOCKET | s, |
| int | _code, | ||
| char * | buf, | ||
| int | n ) |
sending to php
sending to php
| s | connected socket |
| buf | pointer to buffer |
| n | number of characters we want to send |
| _code | Code for php decoding rule |
Definition at line 5561 of file n_network.c.
References _str, FreeNoLog, HEAD_CODE, HEAD_SIZE, LOG_ERR, n_log, neterrno, netstrerror(), and SOCKET_SIZE_FORMAT.
| ssize_t send_ssl_data | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
SSL Writing to a socket.
SSL Writing to a socket.
| netw | connected NETWORK in SSL mode |
| buf | pointer to buffer |
| n | number of characters we want to send |
Definition at line 5172 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_SOCKET_DISCONNECTED, NETW_SOCKET_ERROR, and u_sleep().
Referenced by handle_request(), main(), netw_accept_from_ex(), netw_set_crypto(), netw_set_crypto_pem(), netw_ssl_server_handshake_ex(), netw_ssl_server_handshake_once(), netw_ssl_start_client(), and server_fn().
| ssize_t send_ssl_data_once | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
SSL single-attempt write (see send_data_once contract).
SSL single-attempt write (see send_data_once contract).
One SSL_write attempt; WANT_READ/WANT_WRITE are surfaced to the caller's event loop instead of being spun on. Requires SSL_MODE_ENABLE_PARTIAL_WRITE (set at SSL_CTX creation) so a short write can be resumed from the caller's buffer + offset. Note: a TLS send can return NETW_IO_WANT_READ mid-renegotiation, the caller must retry after the next READABLE event.
| netw | the NETWORK to use (crypto must be active) |
| buf | pointer to buffer |
| n | number of bytes to try to send (> 0) |
Definition at line 5388 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_IO_WANT_READ, NETW_IO_WANT_WRITE, NETW_SOCKET_DISCONNECTED, and NETW_SOCKET_ERROR.
Referenced by io_full(), netw_accept_from_ex(), netw_set_crypto(), netw_set_crypto_pem(), netw_ssl_server_handshake_ex(), netw_ssl_server_handshake_once(), and netw_ssl_start_client().
| ssize_t send_udp_data | ( | void * | netw, |
| char * | buf, | ||
| uint32_t | n ) |
UDP send data to connected peer or specified addr.
UDP send data to connected peer or specified addr.
| netw | connected NETWORK |
| buf | pointer to buffer |
| n | number of bytes to send |
Definition at line 3961 of file n_network.c.
References __n_assert, _netw_capture_error(), _str, endif, FreeNoLog, LOG_DEBUG, LOG_ERR, n_log, neterrno, netstrerror(), netw, NETW_SOCKET_DISCONNECTED, NETW_SOCKET_ERROR, and SOCKET_SIZE_FORMAT.
Referenced by main(), netw_bind_udp(), netw_connect_udp(), and run_client().
|
inlinestatic |
1.0.2 stand-in for SSL_set1_host(): set the expected peer name of ssl, returning 1 on success and 0 on failure
Definition at line 286 of file n_network.h.
Referenced by netw_ssl_do_handshake().
|
inlinestatic |
1.0.2 stand-in for SSL_set_hostflags(): set the X509_CHECK_FLAG_* host-check flags of ssl
Definition at line 279 of file n_network.h.
Referenced by netw_ssl_do_handshake().
 1.15.0